
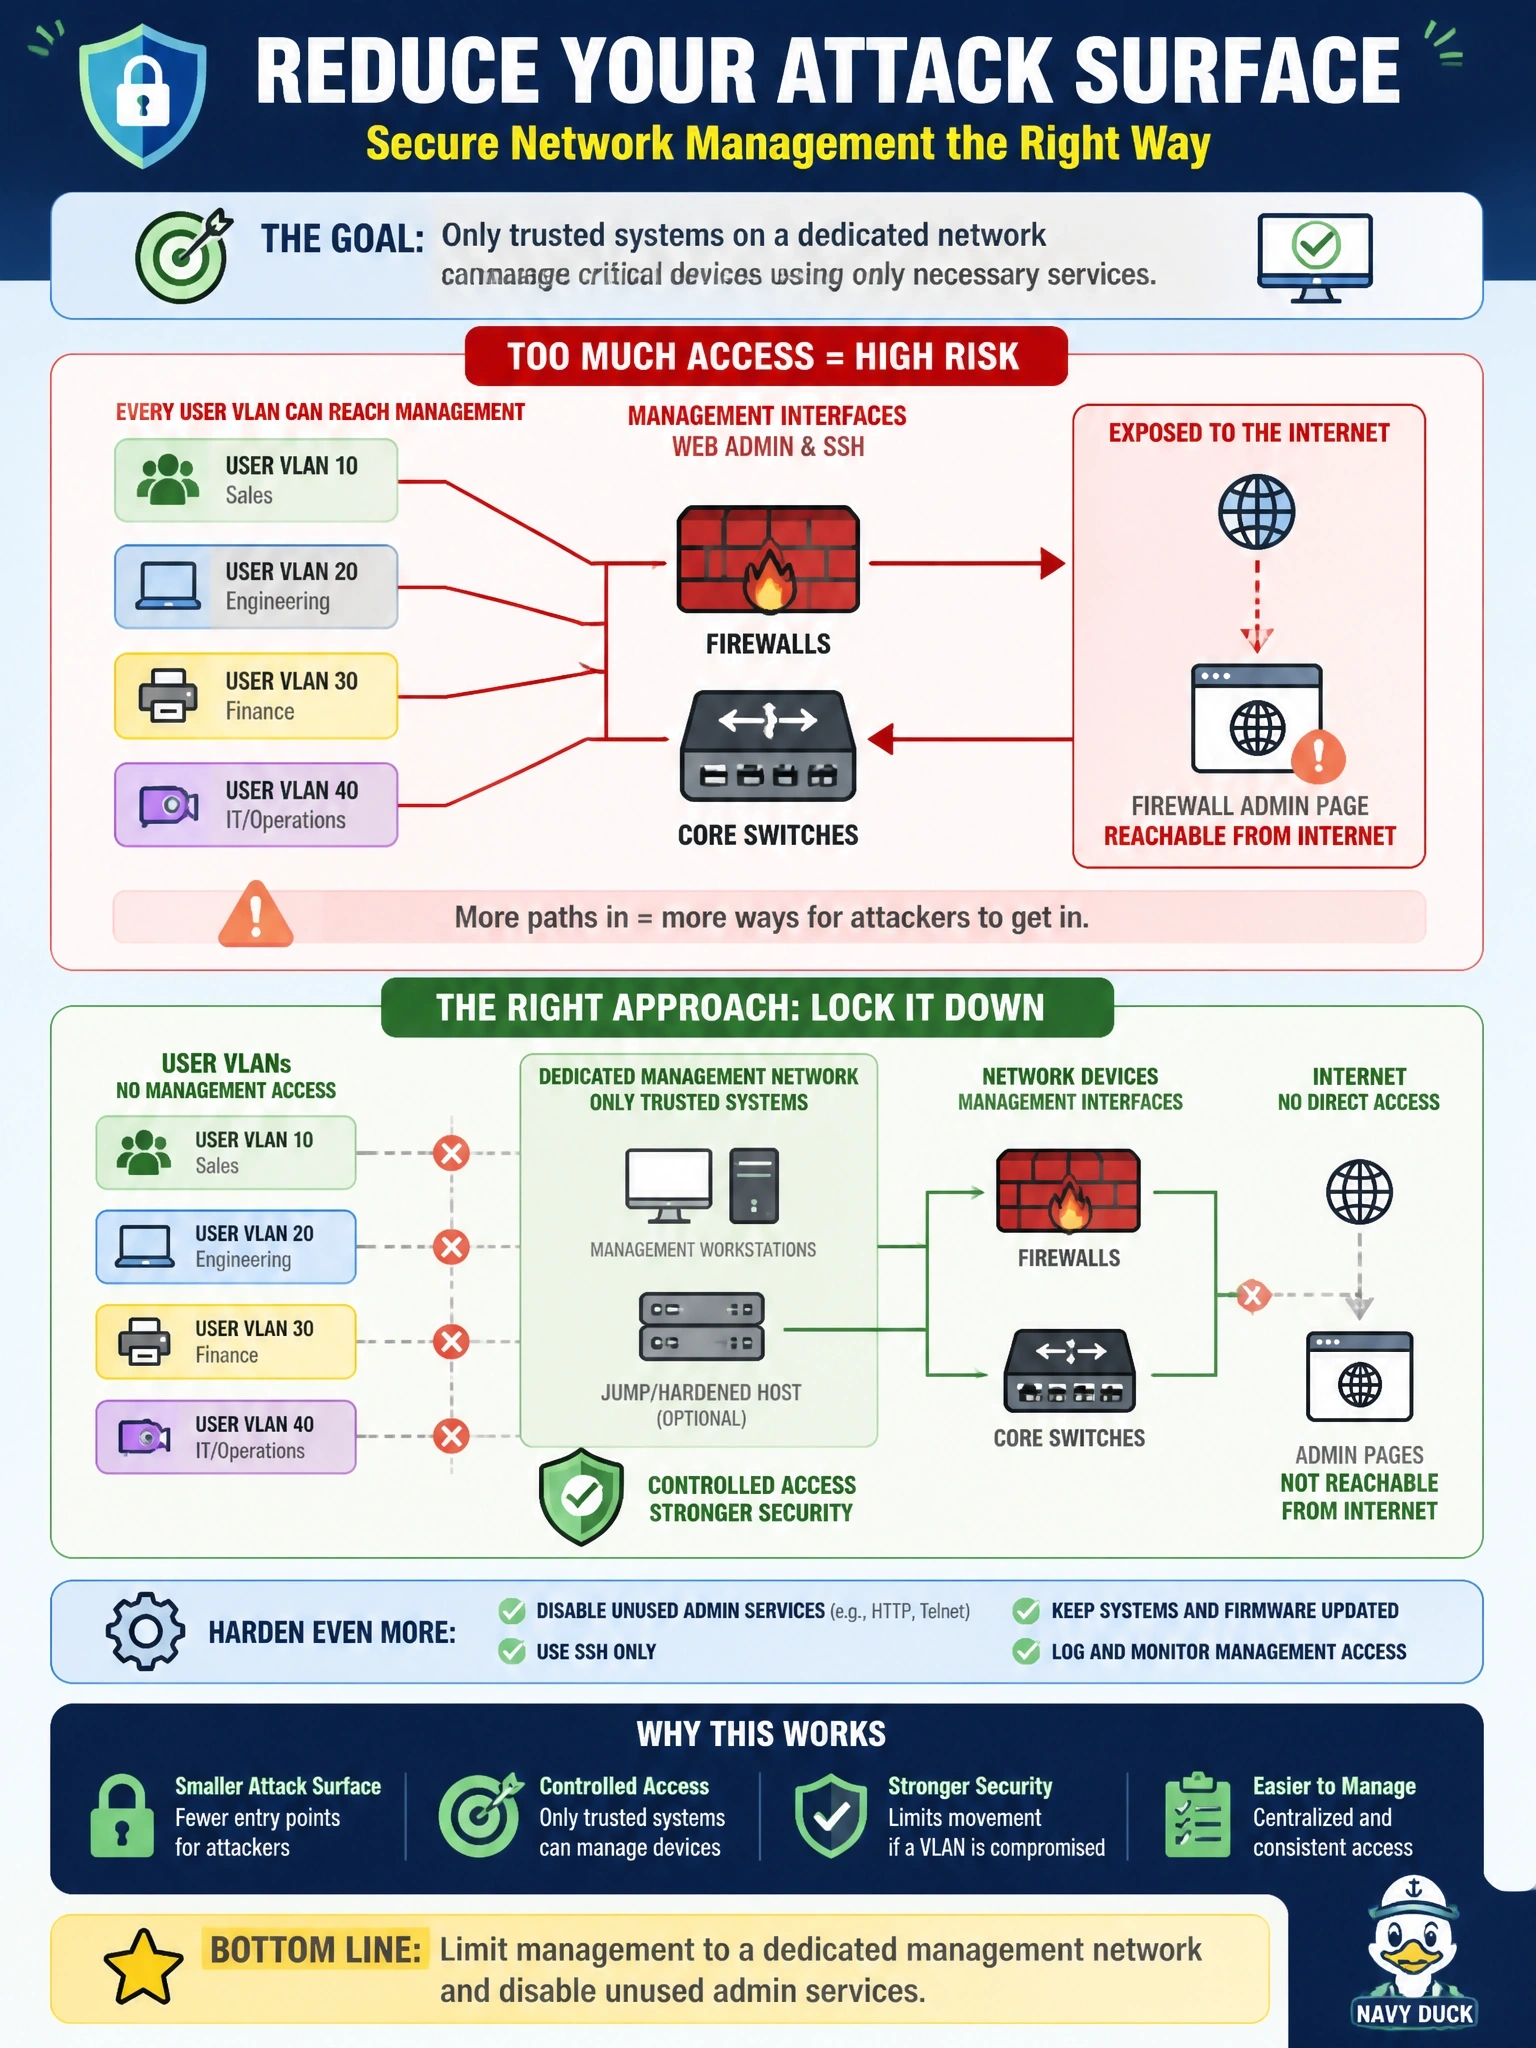
An external scan shows that the web administration interfaces and SSH services on the company's firewalls and core switches are reachable from every user VLAN, and one firewall's admin page is reachable from the internet. Which action MOST effectively reduces this attack surface?
Select an answer to reveal the explanation.
Short Explanation
If every hallway in the building leads to the server room, you don't need a better lock, you need fewer hallways. Restricting management to its own network and shutting off what you don't use removes the paths entirely. Port-hopping's the trap; it hides the door, it doesn't remove it.
Full Explanation
Attack surface reduction removes or restricts the points at which an attacker can interact with a system. Management interfaces are high-value targets because they grant full control of infrastructure, so they should be reachable only from a dedicated management network or jump host, enforced by access control lists, and any management services that are not needed should be disabled. Removing internet exposure and user VLAN access eliminates the paths rather than merely making them harder to use. Moving interfaces to nonstandard ports is security through obscurity; a full port scan still discovers them, and the services remain reachable from every location that could reach them before. Longer passwords strengthen authentication but leave the interfaces reachable, so they remain exposed to vulnerabilities in the management software itself, credential stuffing, and other attacks that do not depend on guessing passwords. An intrusion detection system that alerts on login attempts is a detective control; it may reveal an attack in progress but does not reduce the number of exposed interfaces. Exam caveat: attack surface questions favor answers that remove or restrict exposure over answers that add monitoring or harden what remains exposed, although both are valuable in depth. Operational check: rescan from user VLANs and from the internet to confirm the interfaces are unreachable, and verify that administrators can reach them only through the management network.