
An organization hosts public web servers that must be reachable from the internet, but if one is compromised, the attacker must not have direct access to internal workstations and databases. Which design BEST meets this requirement?
Select an answer to reveal the explanation.
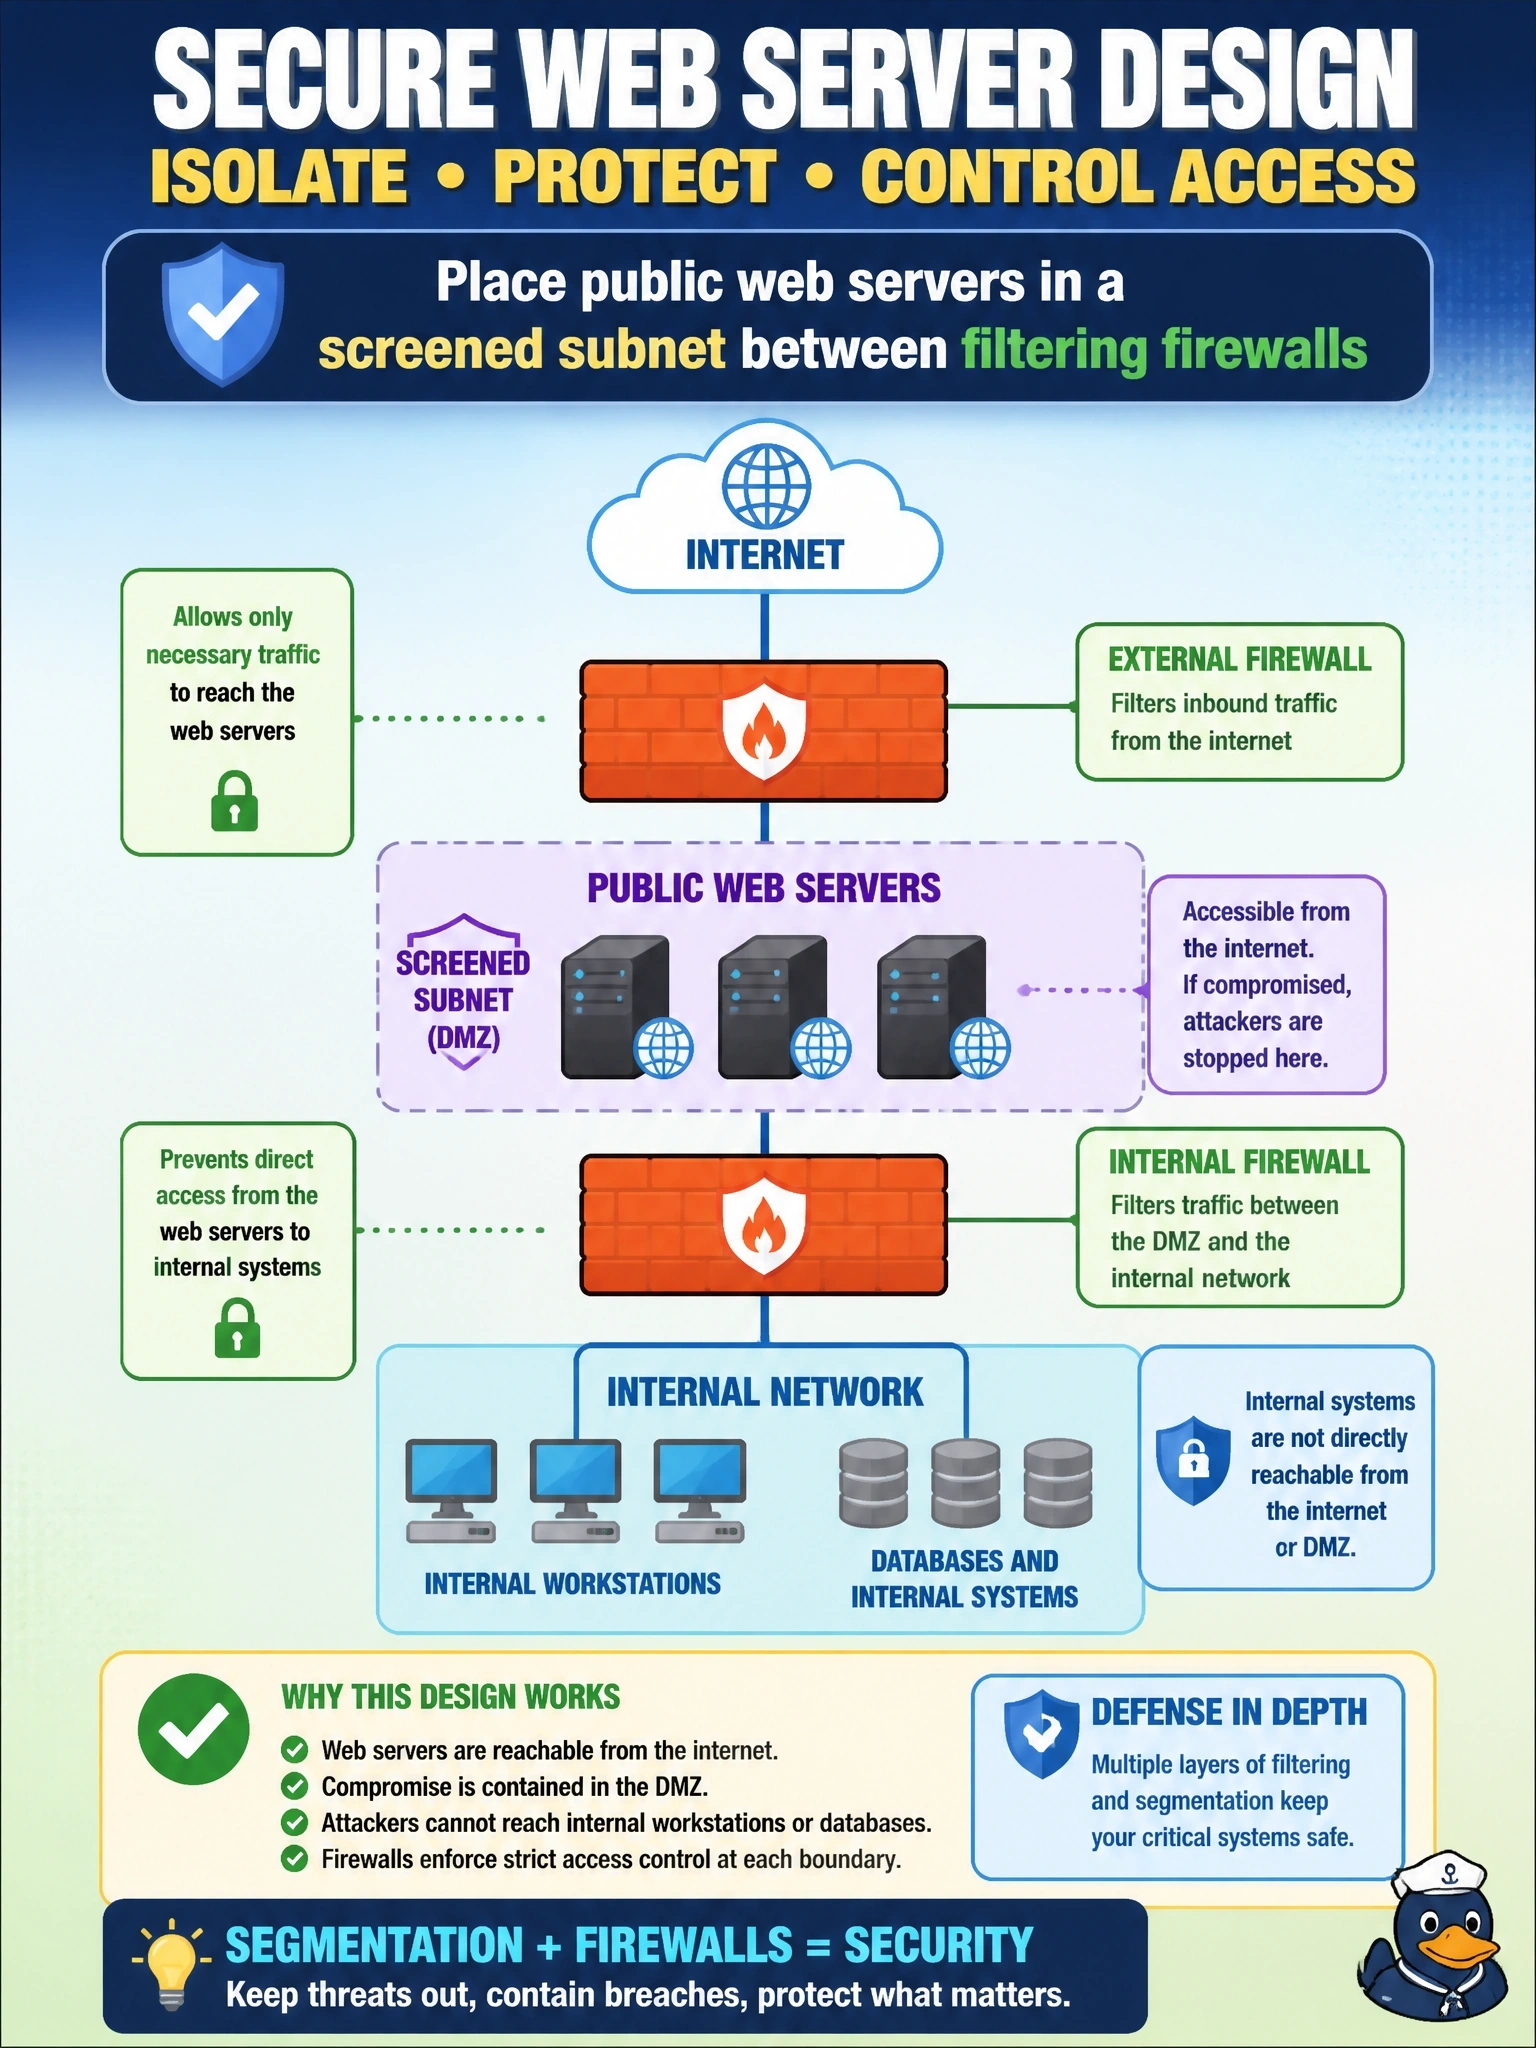
Short Explanation
A screened subnet is the lobby of the building: visitors get in, but they still hit a locked door before the offices. Put public servers there and a compromised one doesn't hand you the keys to the internal LAN. The trap is the 'behind the edge firewall' answer, which lets internet traffic land right next to your users.
Full Explanation
A screened subnet, historically called a demilitarized zone, is a separate security zone for systems that must accept connections from untrusted networks. Firewalls, or a single firewall with multiple interfaces, filter traffic both from the internet into the screened subnet and from the screened subnet into the internal network, so a compromised public server still faces restrictive rules before it can reach workstations or databases. Placing the web servers on the internal LAN means inbound internet connections terminate inside the trusted zone, and a compromise immediately places the attacker alongside internal systems. Putting them in the database VLAN with host firewalls enabled puts the most exposed systems next to the most sensitive data and relies on per-host configuration instead of zone separation. Placing them outside the edge firewall with no filtering exposes every service on those servers directly to the internet and offers no protection for the servers themselves, even though the internal network remains behind the firewall. Exam caveat: only the specific ports needed should be allowed from the screened subnet to internal systems, for example a single database port to a single server, because broad rules undo the zone's value. Operational check: review the firewall rules between the screened subnet and the internal network, confirm only required flows are permitted, and test that a host in the screened subnet cannot initiate connections to workstations.