
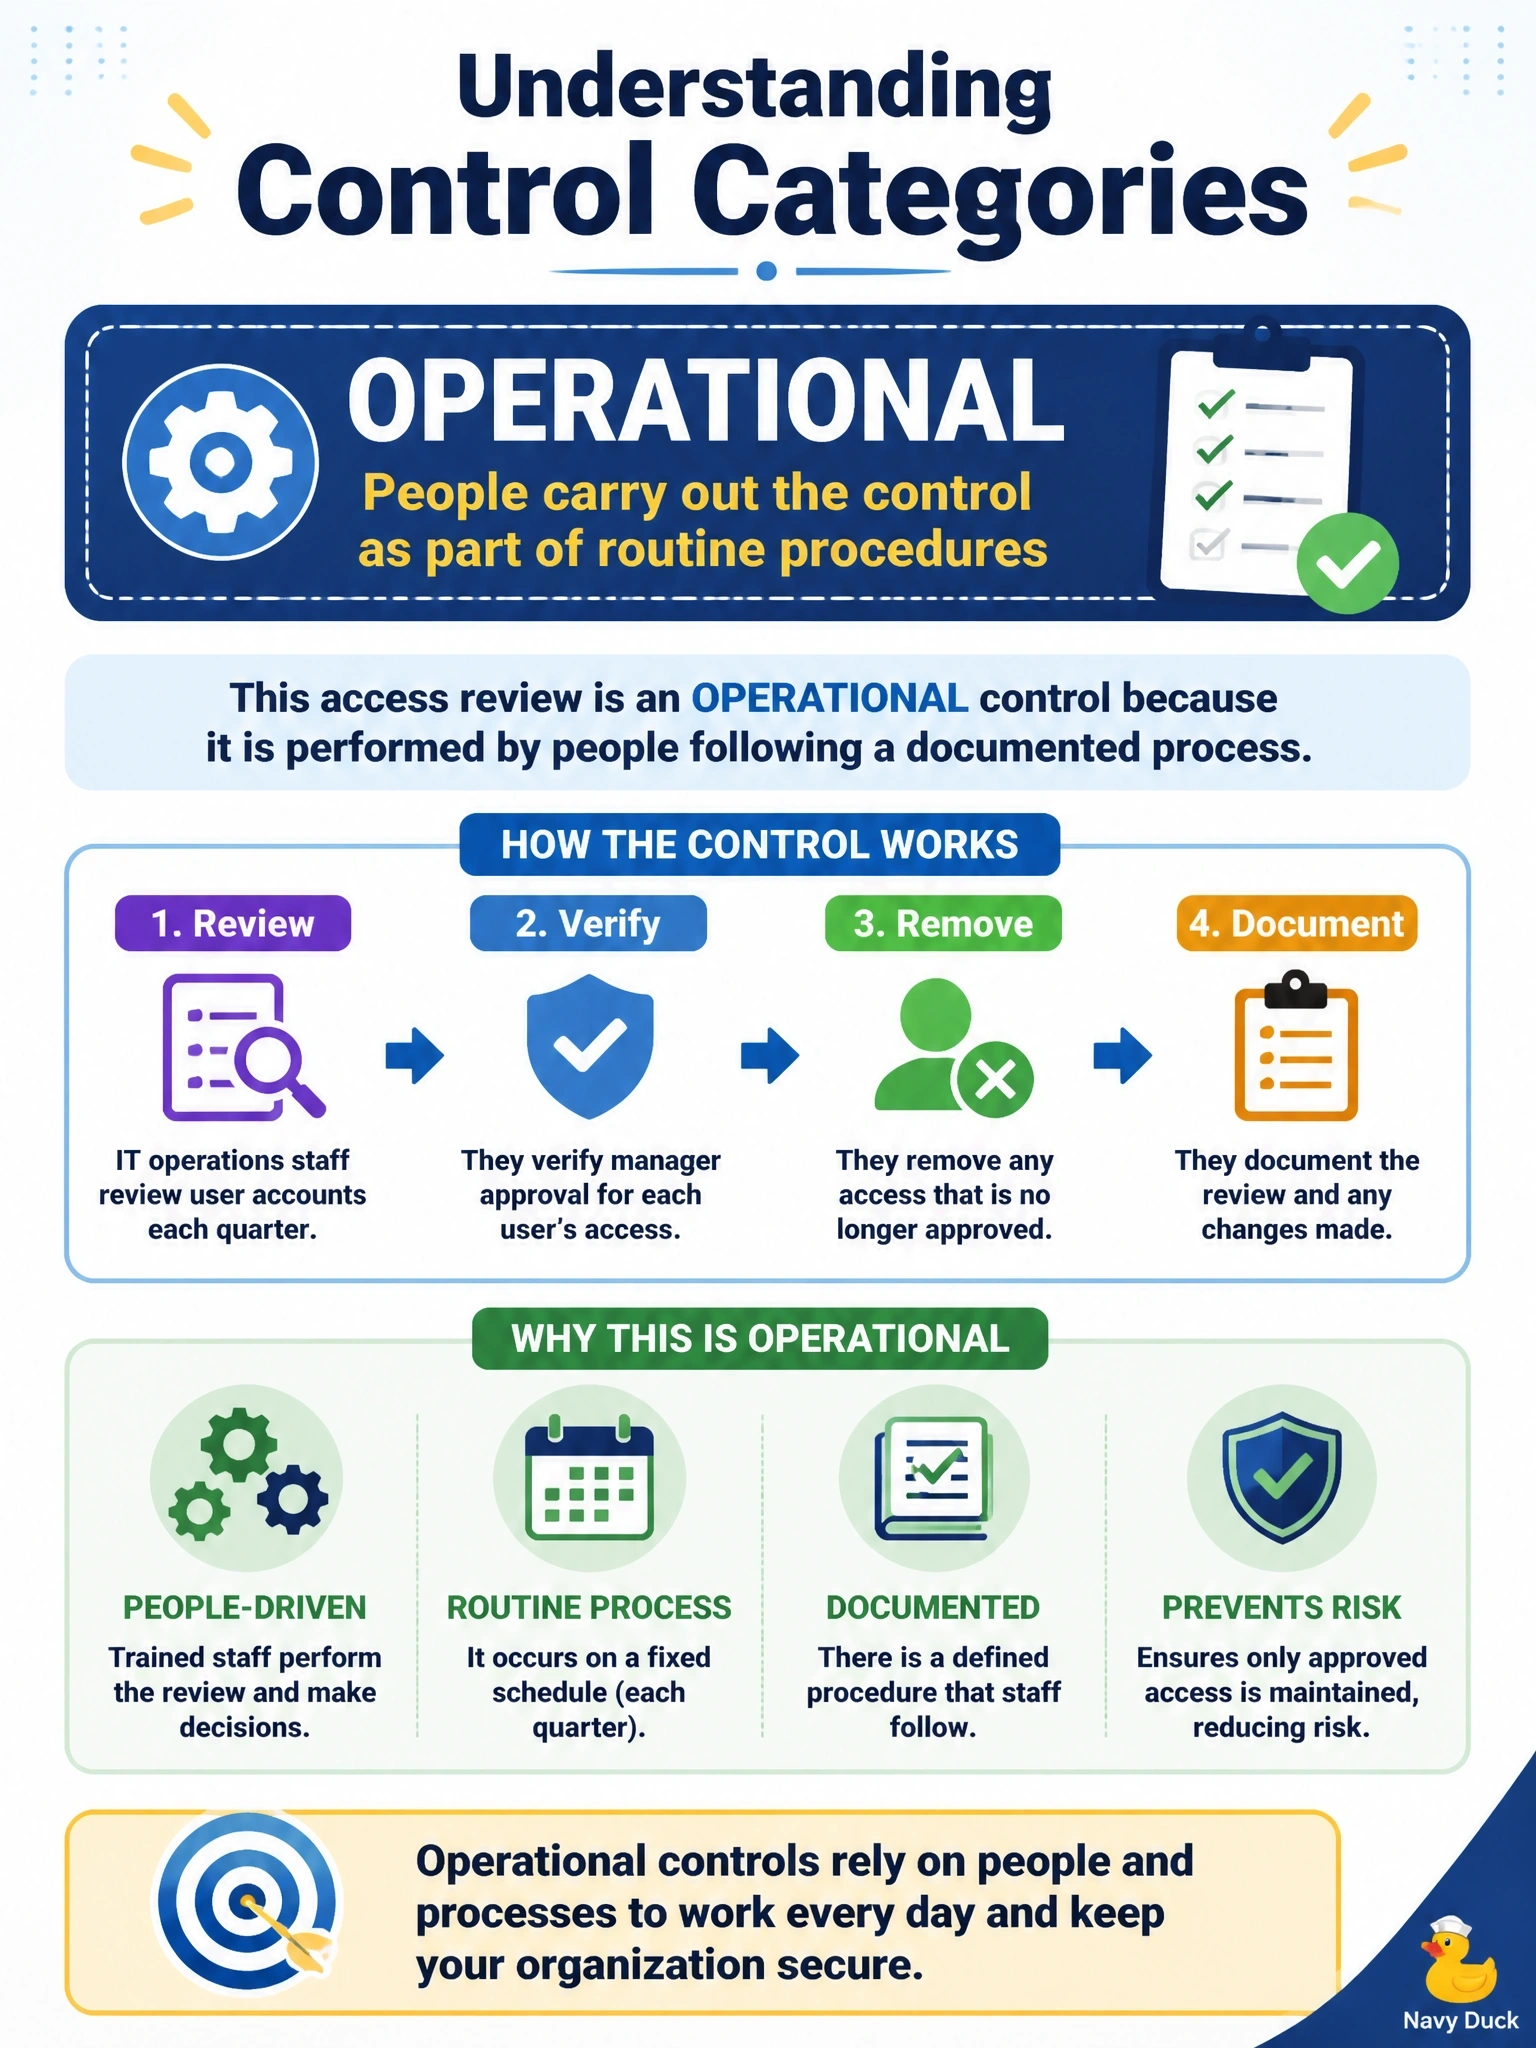
Each quarter, IT operations staff follow a documented procedure to review user accounts and remove any access that managers no longer approve. The review is carried out by people rather than enforced automatically by a system. Which control category BEST describes this access review?
Select an answer to reveal the explanation.
Short Explanation
Here's the trick: who actually does the work? If it's people running a process day to day, it's operational. Don't let the word "documented" pull you toward managerial, because nearly everything is written down somewhere.
Full Explanation
Operational controls are security activities executed primarily by people rather than by systems: guards on patrol, staff performing backups by procedure, awareness training delivery, and periodic account reviews carried out by operations personnel. The scenario stresses that staff perform the review on a schedule, which places it in the operational category. Managerial controls set strategy and oversight, such as policies, risk assessments, and the decision that access reviews must happen; the existence of a written procedure does not convert the execution of that procedure into a managerial control. Technical controls are enforced by hardware or software without human execution, such as automated deprovisioning triggered by an HR system; the review may result in permission changes, but the control itself is the human examination and decision. Physical controls restrict tangible access to spaces and equipment; signing a form in person is incidental and does not make the control physical. Exam caveat: many controls involve documents, people, and systems at once, so classify by the primary mechanism that delivers the protection. Operational check: confirm the procedure names who performs the review, what evidence is retained, and how removals are tracked to completion, then sample last quarter's review to verify that unapproved access was actually removed.