
A visitor on a campus access port sends frames with a new source MAC address until the switch MAC table is full. Legitimate frames then leave every port. Which attack is this?
Select an answer to reveal the explanation.
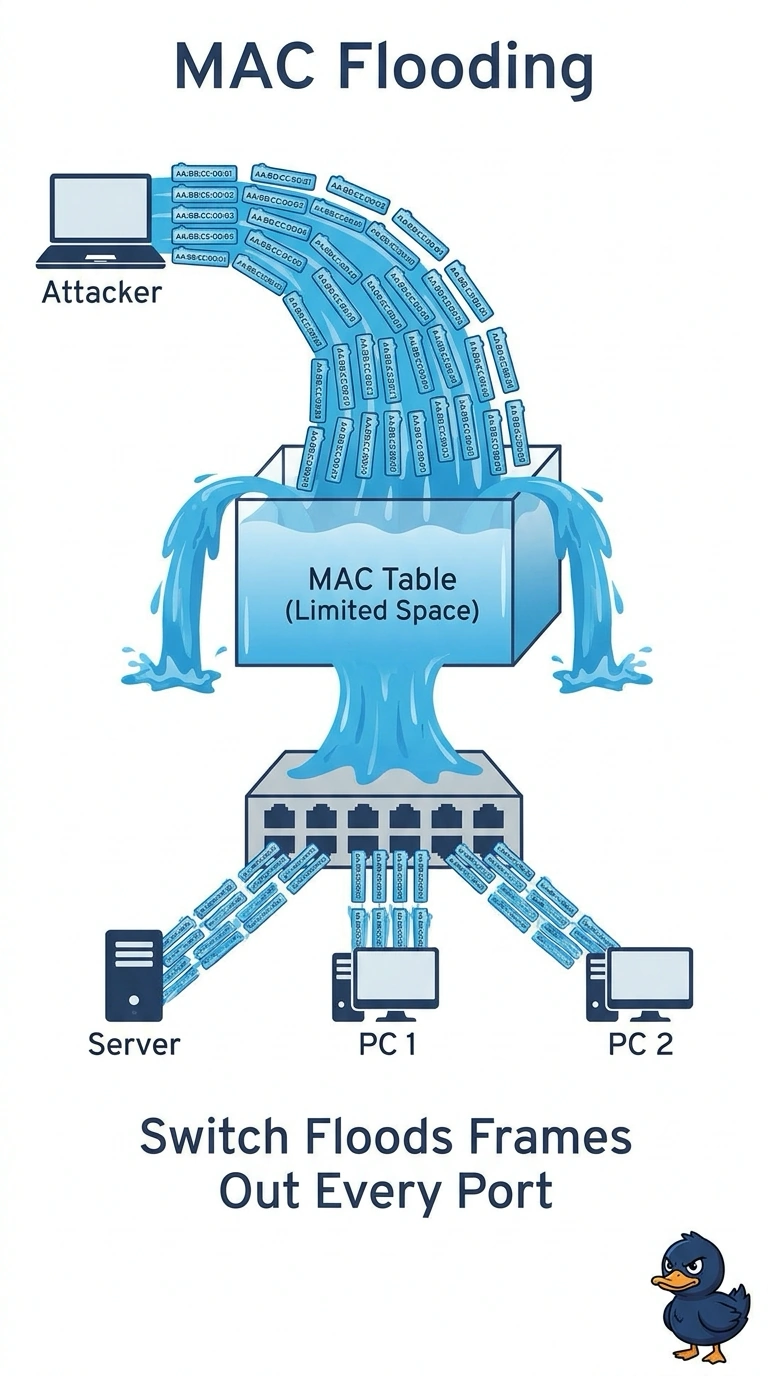
Short Explanation
The switch keeps a seating chart of which MAC sits on which port, and if you flood that chart with fake names it gives up and shouts every conversation into every seat. That overflow is MAC flooding. Poisoning an ARP cache, cloning a wireless name, or draining a DHCP pool are different tricks, even when somebody describes them with the same words.
Full Explanation
A switch learns source MAC addresses into a finite table and forwards unicast frames out the matching port. When that table is full of bogus entries, the switch cannot look up legitimate destinations and floods those frames out the ports in the VLAN, which is what the visitor caused. That attack is MAC flooding. ARP poisoning sends forged ARP replies so hosts map an IP address to the attacker's MAC. Double-tagging is a VLAN-hopping method, not ARP, and neither one is what filled this MAC table. An evil twin is a wireless access point that copies a legitimate SSID. It does not fill a wired switch's MAC table by using a network name. DHCP exhaustion consumes address leases so clients cannot obtain a lease. The stem describes flooded frames after a full MAC table, not a pool with zero free leases. Exam caveat: port security with a MAC limit is the usual control that shuts or restricts a port before a flood can fill the table. Operational check: look for a rapidly growing MAC count on the visitor's port, enable port security with a small maximum, and confirm unicast traffic is no longer flooded after the bogus entries age out.