
A campus must revoke one departing student without changing a passphrase that every other student still uses. A RADIUS server is already available. Which wireless authentication fits?
Select an answer to reveal the explanation.
Short Explanation
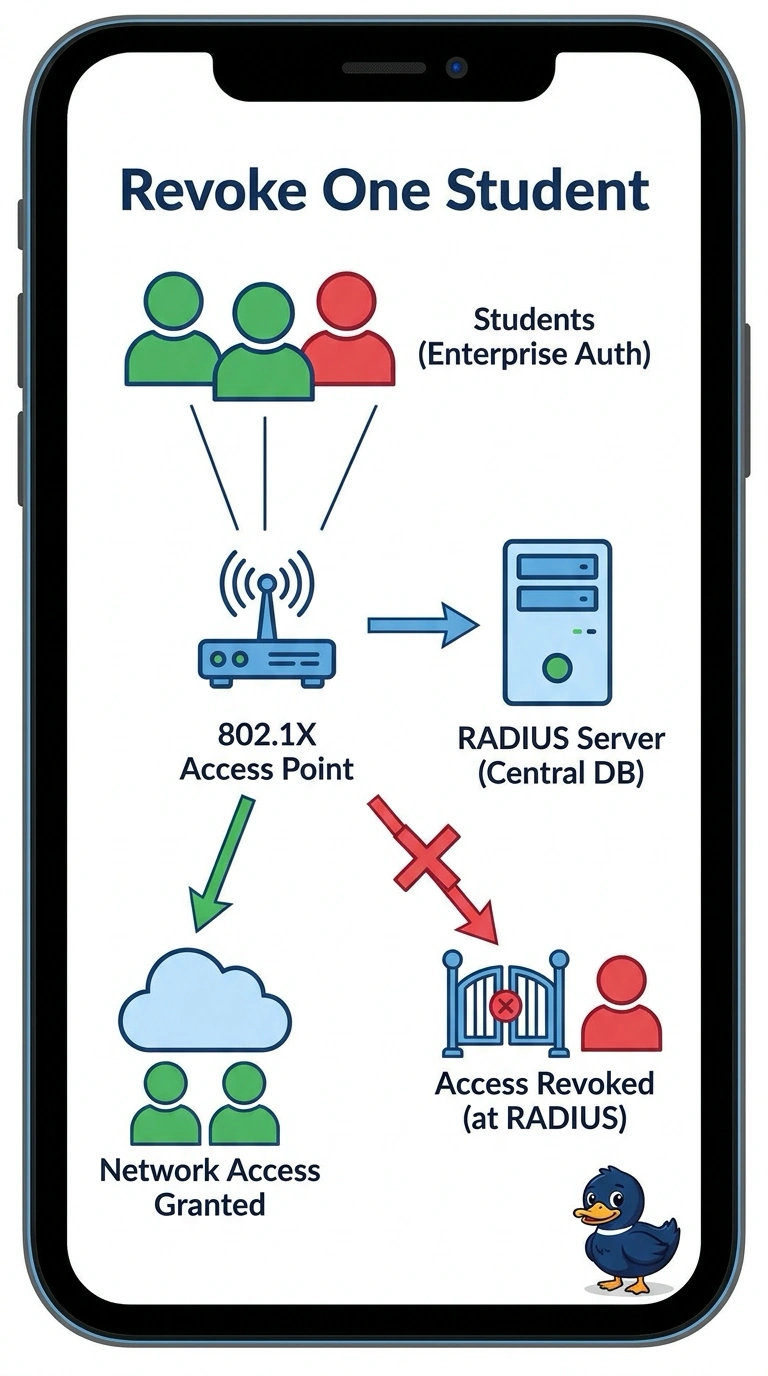
A shared door code forces you to rekey the whole building when one person moves out. You want enterprise authentication with 802.1X against the RADIUS server the campus already has, so one student can be disabled and everyone else stays connected. A personal passphrase, even a newer one, or a hardware-address list does not revoke that account.
Full Explanation
Enterprise wireless authentication uses 802.1X. RADIUS checks the individual student, so disabling that account revokes access without rotating a passphrase everyone else knows. WPA2-Personal uses one pre-shared key. Removing one person means changing that key for every remaining student. WPA3-Personal is the tempting twin because it is the newer personal mode. It still uses one shared passphrase, and it does not give the campus a RADIUS account to disable. MAC filtering can block the student's laptop. It is not the account on the RADIUS server the stem already has, and a new laptop with a new address walks around the list. Exam caveat: an account disabled in the directory and still accepted by a stale RADIUS rule is not revoked. Operational check: disable a test student, confirm that account fails 802.1X, and confirm a second student still connects without a new passphrase. Confirm the access point is in enterprise mode. A personal passphrase left on a second SSID would bypass the revocation.