
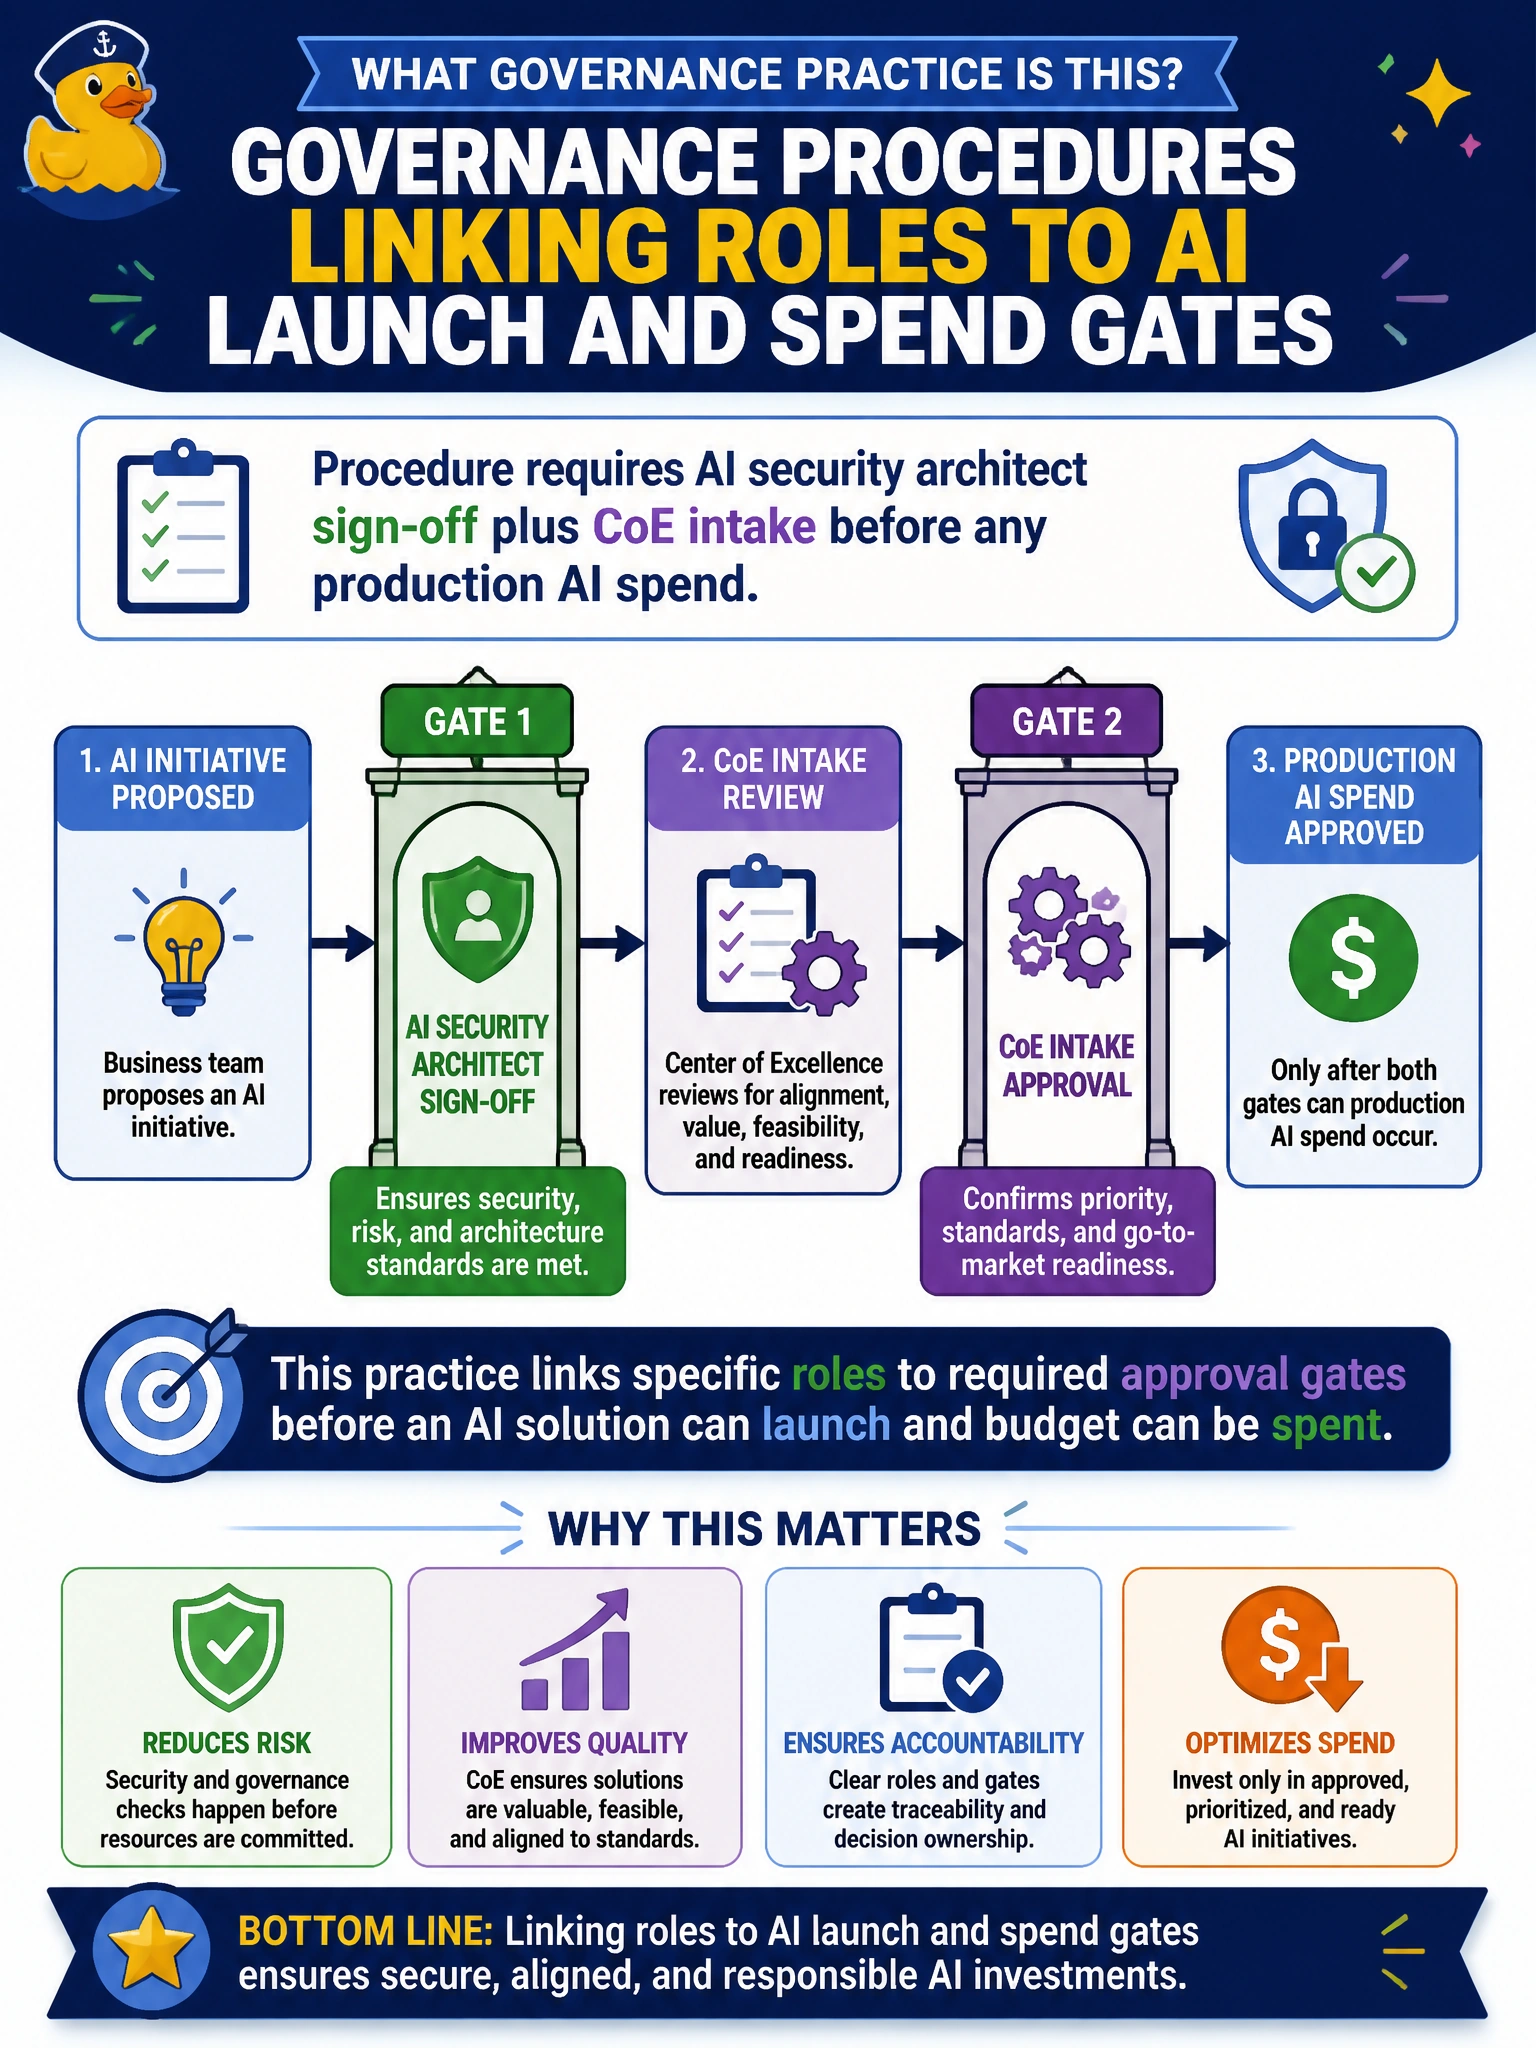
Procedure requires AI security architect sign-off plus CoE intake before any production AI spend. What governance practice is this?
Select an answer to reveal the explanation.
Short Explanation
Want production AI budget? Get CoE intake and the AI security architect’s sign-off first — roles wired into the spend gate. A centralized vendor assessment or MLOps release control alone won't stop shadow AI—those don't wire the architect sign-off and CoE intake into the spend gate. FinOps dashboards tracking consumption for chargeback won't wire the architect and CoE into the spend gate either.
Full Explanation
Governance procedures linking roles to AI launch and spend gates are demonstrated when procedure requires AI security architect sign-off plus CoE intake before any production AI spend. Binding named roles and intake steps to money and production authority works because shadow purchasing and unreviewed launches are common municipal failure modes. The procedure makes architecture and CoE coordination prerequisites—not optional centralized vendor assessments that review third-party model risk without requiring architect sign-off and CoE intake as a gate.
FinOps dashboards tracking production AI consumption for monthly departmental chargeback reporting fail because they track spend after the fact, not because they enforce architect sign-off and CoE intake before any production AI spend. Centralized vendor assessments reviewing third-party model risk before procurement approval fail because they assess vendor risk without requiring the AI security architect's sign-off and CoE intake as a spend gate. MLOps release controls requiring performance validation before production model promotion fail because they validate model performance, not because they link the AI security architect and CoE intake to production spend authority.
Exam caveat: a procedure that exists on paper but is bypassable via MLOps release controls alone is not an effective spend gate; exam scenarios may test enforcement versus documentation. Operational check: integrate CoE intake IDs and architect sign-off into procurement/production checklists, block deployment credentials without those artifacts, and periodically reconcile AI-related spend to intake records—because MLOps release controls alone only validate performance and don't enforce the required sign-off and intake gate.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.