
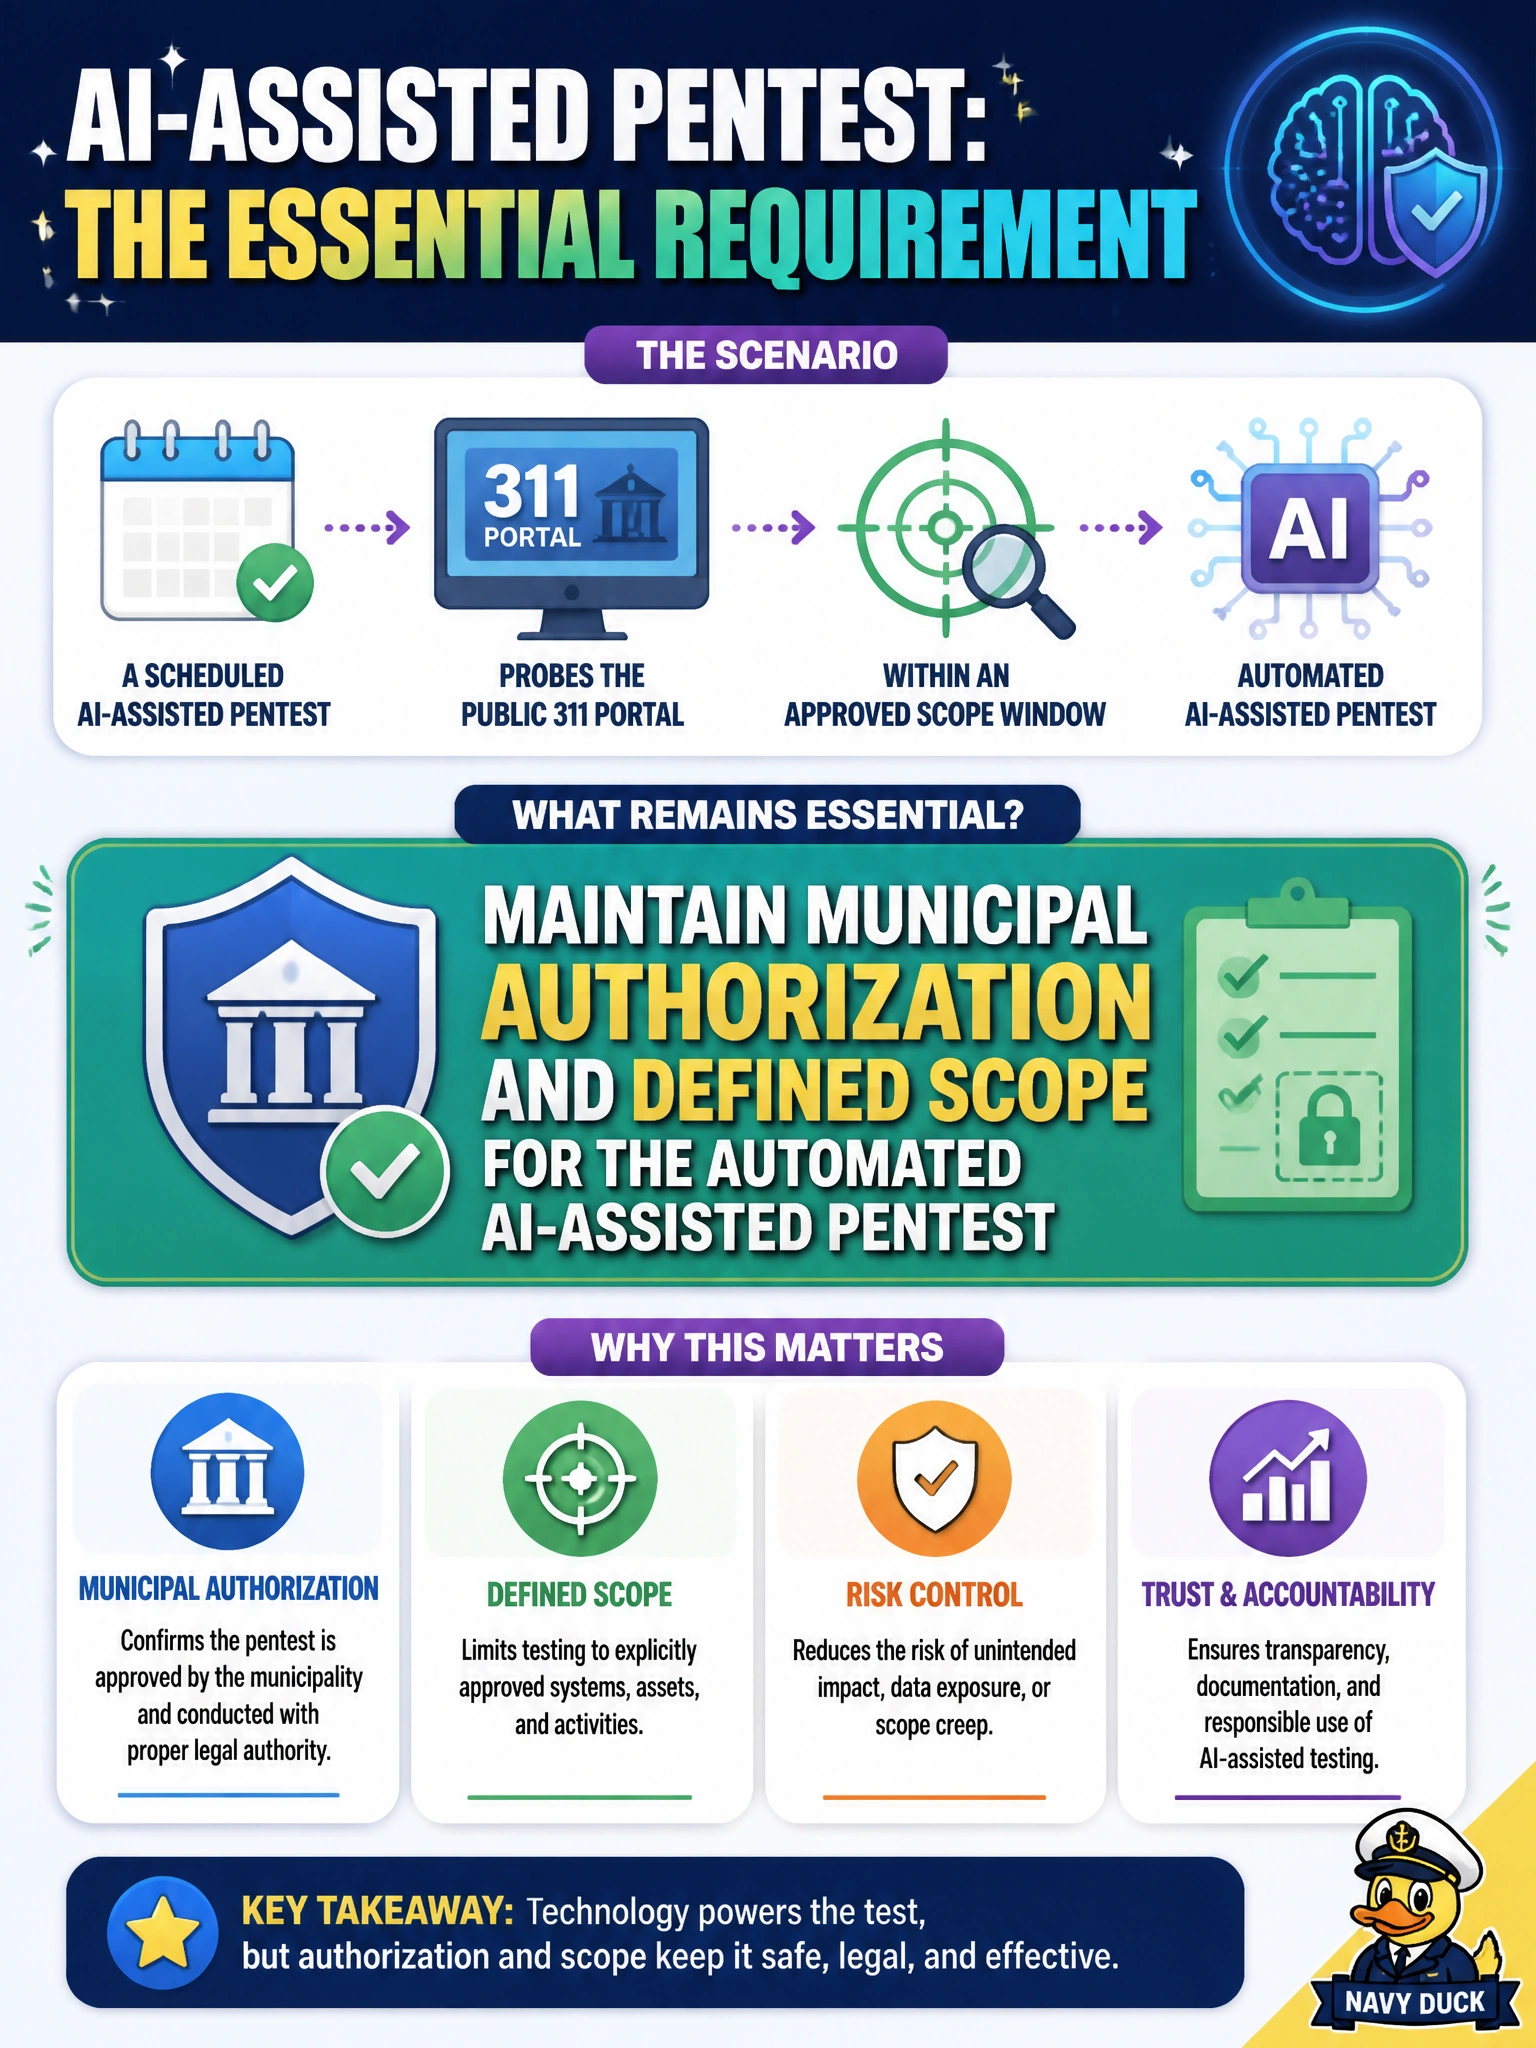
A scheduled AI-assisted pentest probes the public 311 portal within an approved scope window. What requirement remains essential?
Select an answer to reveal the explanation.
Short Explanation
AI can help poke the 311 portal—but only inside the permission slip and time box. Don't assume the public portal terms give you permission, don't count on an annual review to cover this window, and don't limit your approval to linked backend APIs when you're testing the portal.
Full Explanation
Maintaining municipal authorization and defined scope for a scheduled AI-assisted pentest of the public 311 portal remains essential because automation and AI do not waive rules of engagement, legal authority, or change control. AI-assisted testing can increase probe speed and creativity, which makes unscoped activity more dangerous, not less. Civic environments especially require written approval, time boxes, and target lists to protect residents’ services and neighboring systems.
Verifying municipal authorization via public portal terms for the automated AI-assisted pentest fails because publicly accessible terms of use are not pentest authorization—only explicit municipal approval naming the 311 portal targets grants permission to probe. Renewing municipal authorization at annual contract review for the automated AI-assisted pentest fails because authorization must be current and window-specific—an annual review does not provide valid approval for this scheduled scope window. Restricting municipal authorization to linked backend APIs for the automated AI-assisted pentest fails because the approved target is the named 311 portal—limiting approval to backend APIs leaves the portal itself unauthorized and wrongly pulls neighboring out-of-scope systems into scope.
Exam caveat: “the annual review already renewed our authorization” is not a defense—operators own scope enforcement, kill switches, and allowlists and still need written approval for this scheduled window regardless of contract-cycle timing. Operational check: issue a signed rules-of-engagement document naming the 311 portal URLs/IPs, test window, and prohibited targets—public portal terms do not verify authorization, annual contract review does not renew authorization for this scheduled window, and authorization is not restricted to linked backend APIs; monitor for outbound probes beyond scope; keep logging enabled; and halt immediately if the tool touches non-authorized networks.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.