
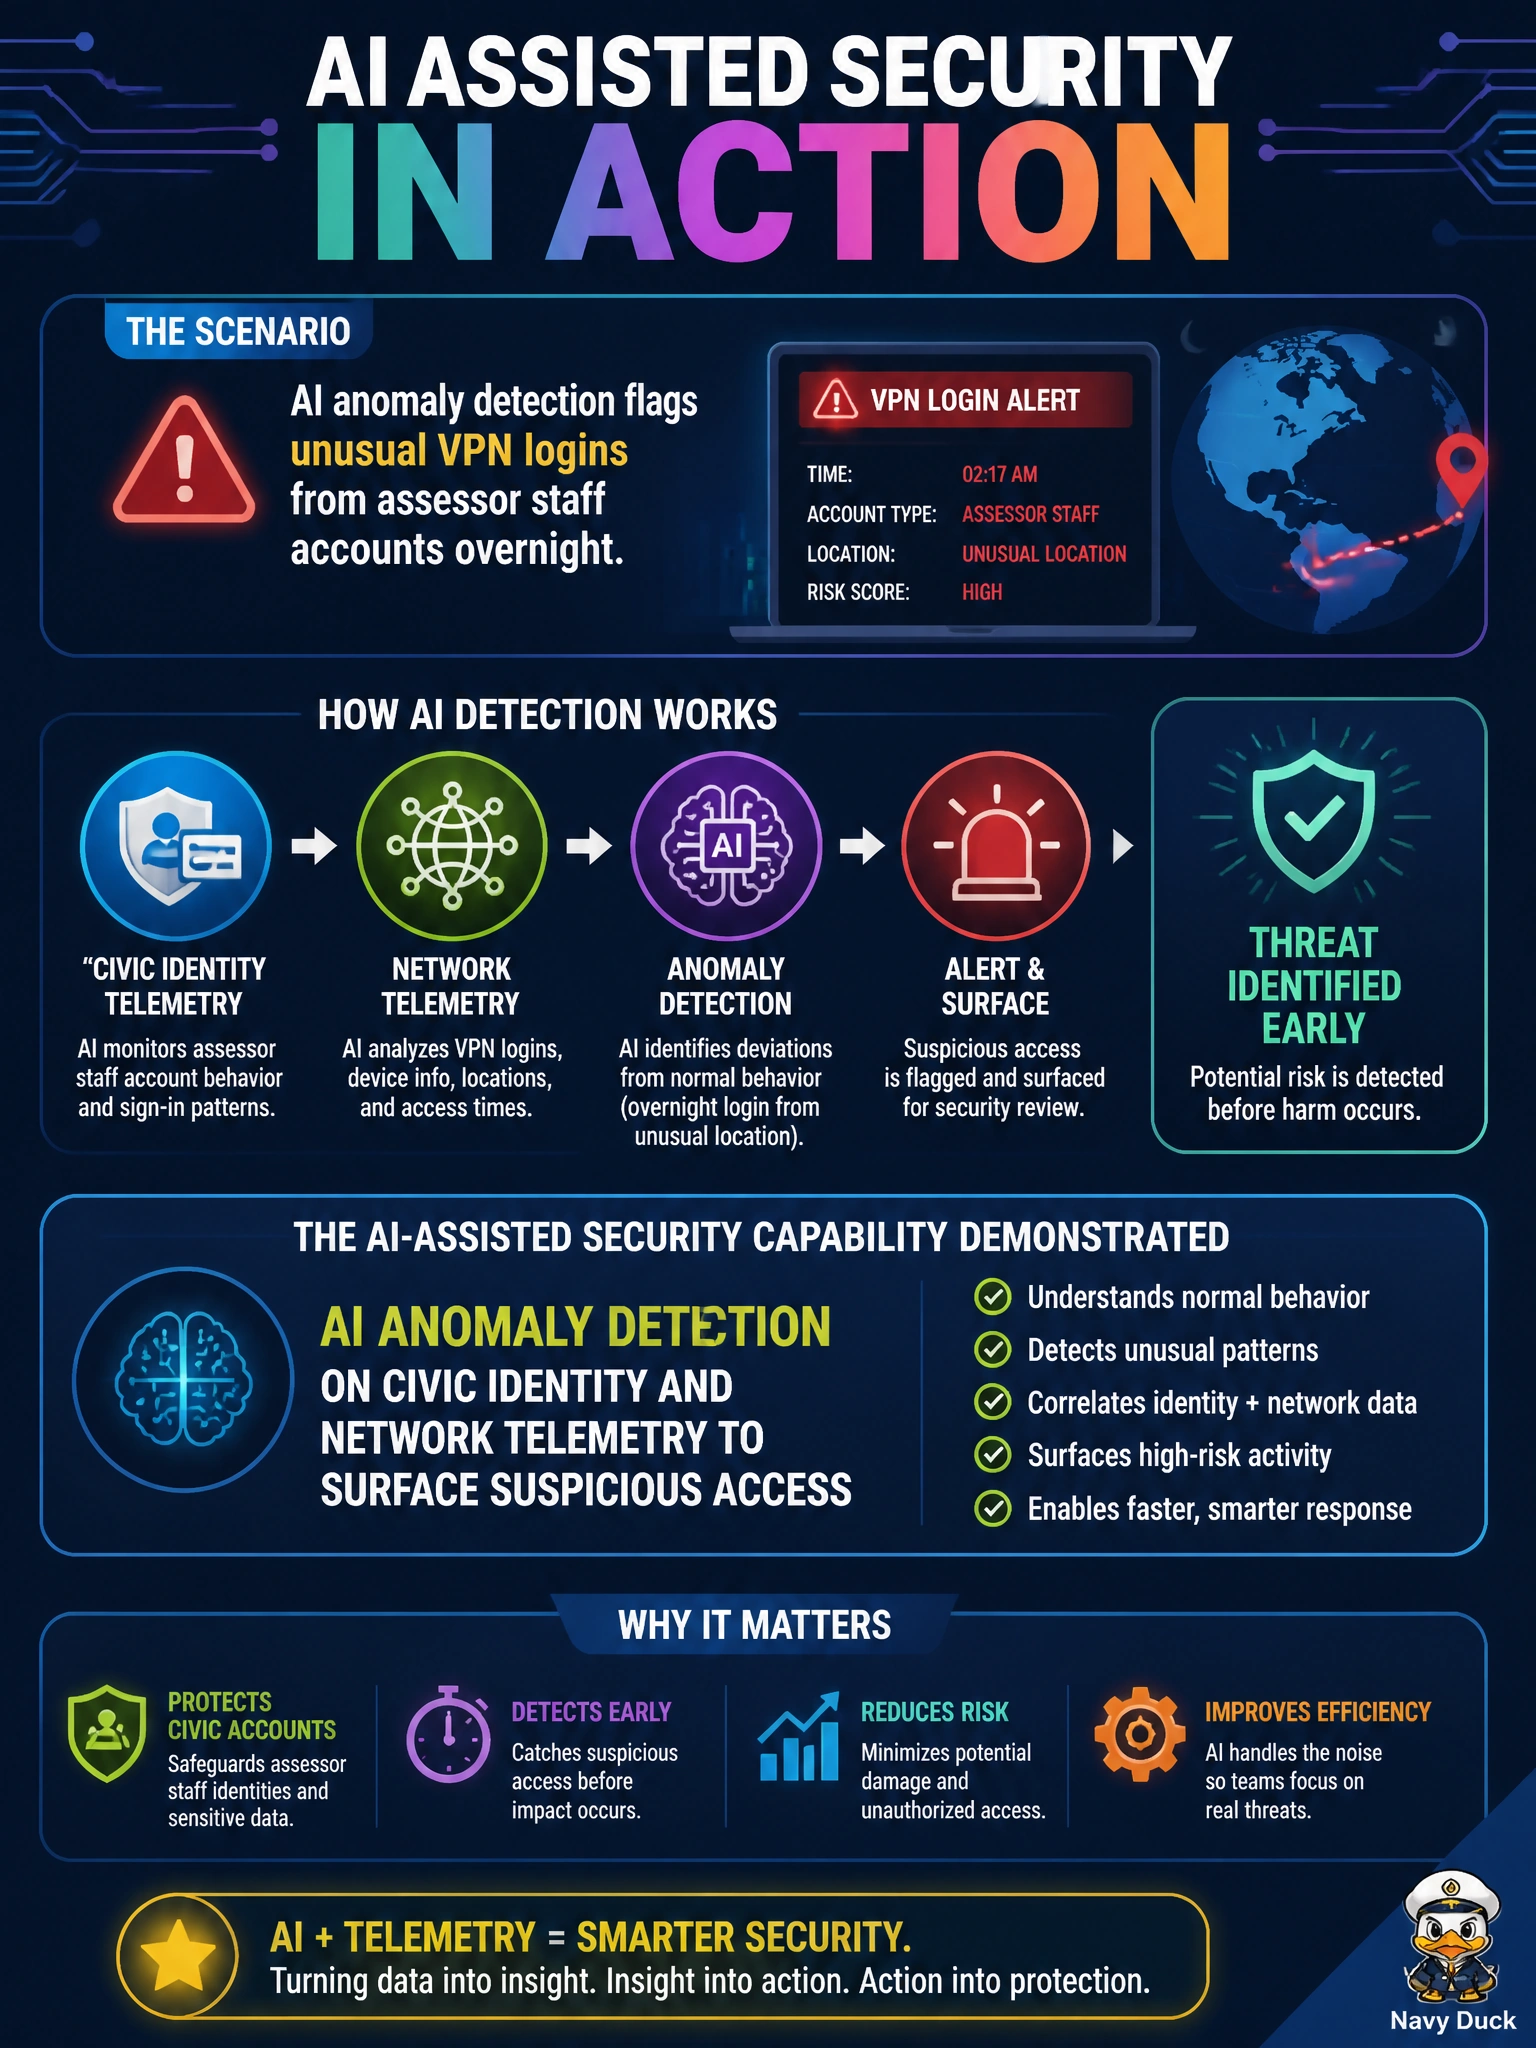
AI anomaly detection flags unusual VPN logins from assessor staff accounts overnight. What AI-assisted security capability is demonstrated?
Select an answer to reveal the explanation.
Short Explanation
Weird midnight VPN hits from assessor accounts? That's AI anomaly detection doing its job — surface the odd, then investigate. You'll see vulnerability scans and patch history, email gateway logs, or firewall allowlists each do something else — they don't catch a live login like this.
Full Explanation
AI anomaly detection that flags unusual VPN logins from assessor staff accounts overnight demonstrates AI anomaly detection on civic identity and network telemetry to surface suspicious access because the capability highlights deviations from learned baselines for investigation. Assessor accounts often access sensitive parcel and taxpayer-adjacent systems; odd overnight VPN use is a classic early signal for credential abuse. Domain 3 treats this as assisted detection that still requires human follow-up.
AI anomaly detection on vulnerability scan results and patch history to surface suspicious access fails to match the stem because reviewing scan results and patch history looks for unpatched vulnerabilities and remediation gaps; it does not surface a live, overnight anomaly for investigation the way the flag in the stem does. AI anomaly detection on email gateway logs and data filters to surface suspicious access fails because analyzing email gateway activity looks for messaging and filter anomalies, which is unrelated to detecting an unusual login pattern as it happens. AI anomaly detection on firewall allowlists and static asset records to surface suspicious access fails because checking static allowlists and asset records validates known policy and inventory, not for an anomalous login pattern from an otherwise-legitimate assessor account.
Exam caveat: shift work, on-call assessors, and travel can create legitimate overnight patterns; tune baselines with role and schedule context to limit alert fatigue without dismissing true positives. Operational check: correlate the VPN anomaly with MFA claims, source geolocation/ASN, and subsequent assessor-app actions; open a ticket for confirmed outliers; and verify that VPN and IdP logs remain retained per municipal policy.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.