
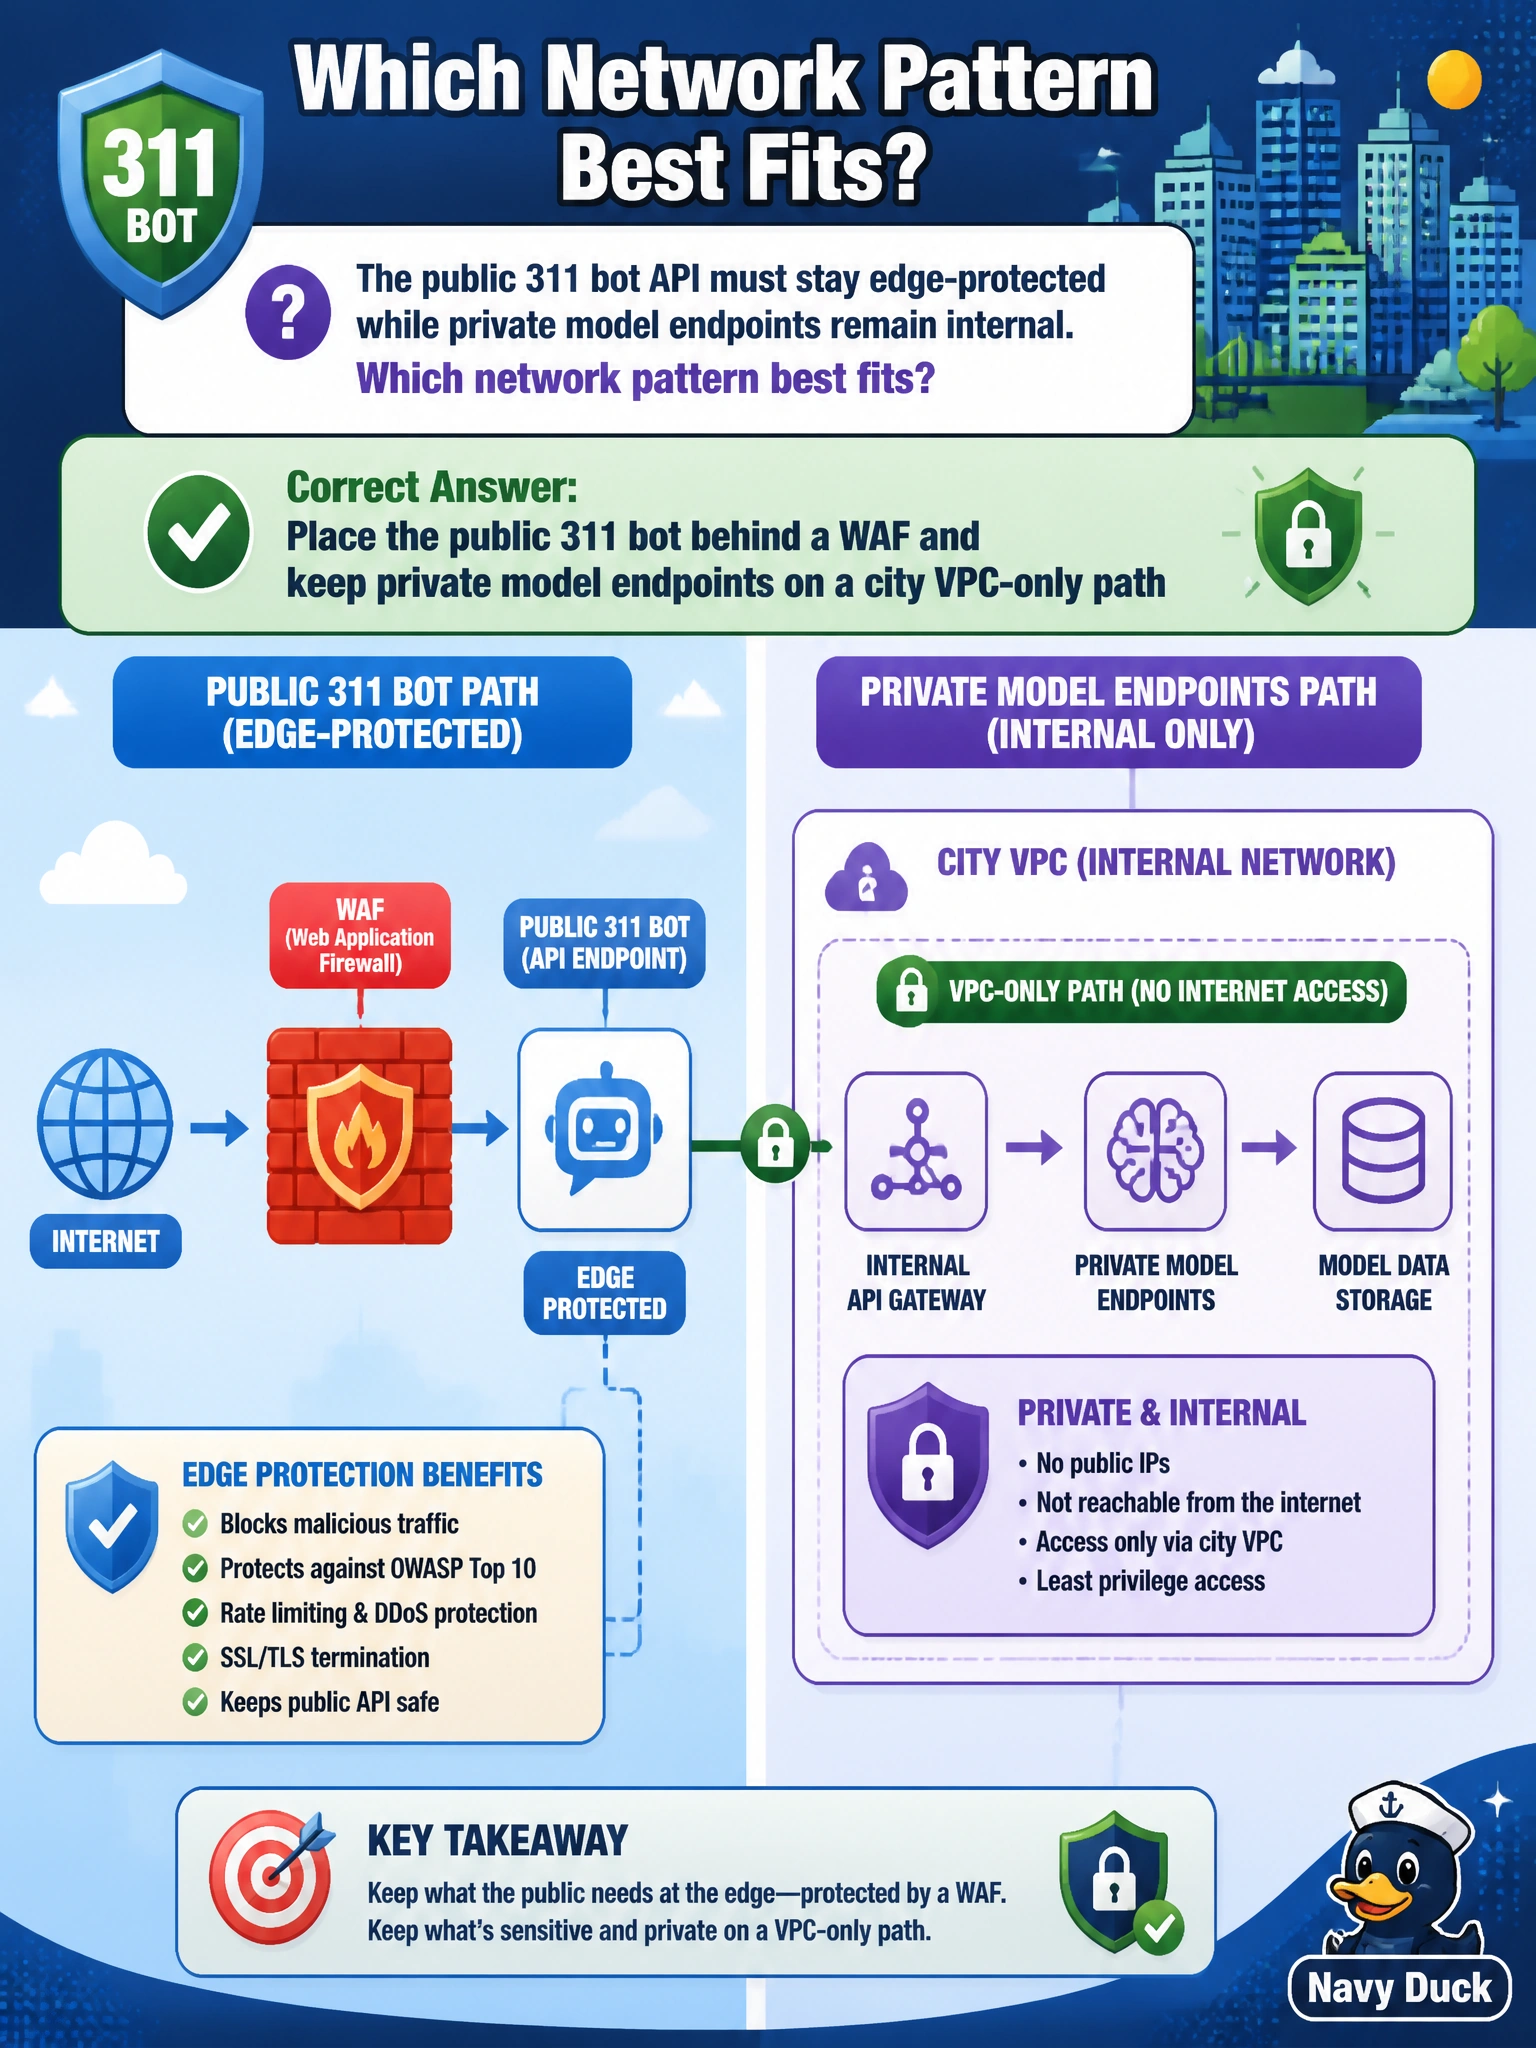
The public 311 bot API must stay edge-protected while private model endpoints remain internal. Which network pattern best fits?
Select an answer to reveal the explanation.
Short Explanation
Public doors get a guard; back-office model rooms stay inside the building. You put the 311 bot behind a WAF and keep private model endpoints on a VPC-only path. You'll miss it if your public bot sits on just an internet gateway or edge balancer without a WAF, or your private models use a NAT outbound path that's not truly VPC-only.
Full Explanation
Placing the public 311 bot behind a WAF and keeping private model endpoints on a city VPC-only path is the network pattern that protects the public API edge while leaving private inference internal. Public civic bots face Internet abuse and need edge protections such as a web application firewall. Private model endpoints that serve internal inference should not be Internet-exposed; restricting them to VPC-only paths preserves network segmentation between the resident-facing 311 surface and back-end municipal model infrastructure.
Placing the public 311 bot on an internet gateway and keeping private model endpoints on city VPC-only path fails because it leaves the public bot without WAF edge filtering, exposing the resident-facing API to Internet abuse even though private segmentation is preserved. Placing the public 311 bot behind an edge balancer and keeping private model endpoints on city VPC-only path fails because an edge balancer provides distribution without WAF inspection, so the public 311 edge still lacks the required application-layer protection. Placing the public 311 bot behind a WAF and keeping private model endpoints on a city VPC NAT outbound path fails because a NAT outbound path permits internet egress from the model tier, breaking strict VPC-only internal isolation and introducing exfiltration risk.
Exam caveat: Separate public AI edges (WAF-protected) from private model endpoints (VPC-only). Using an internet gateway or edge balancer without a WAF for the public bot, and using a NAT outbound path instead of VPC-only for private models, are common wrong patterns.
Operational check: Front the 311 bot with a WAF and auth, place model endpoints on private VPC networking only, verify external clients cannot reach private model URLs, confirm the bot still calls models over the internal path, and keep authentication enabled on both tiers.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.