
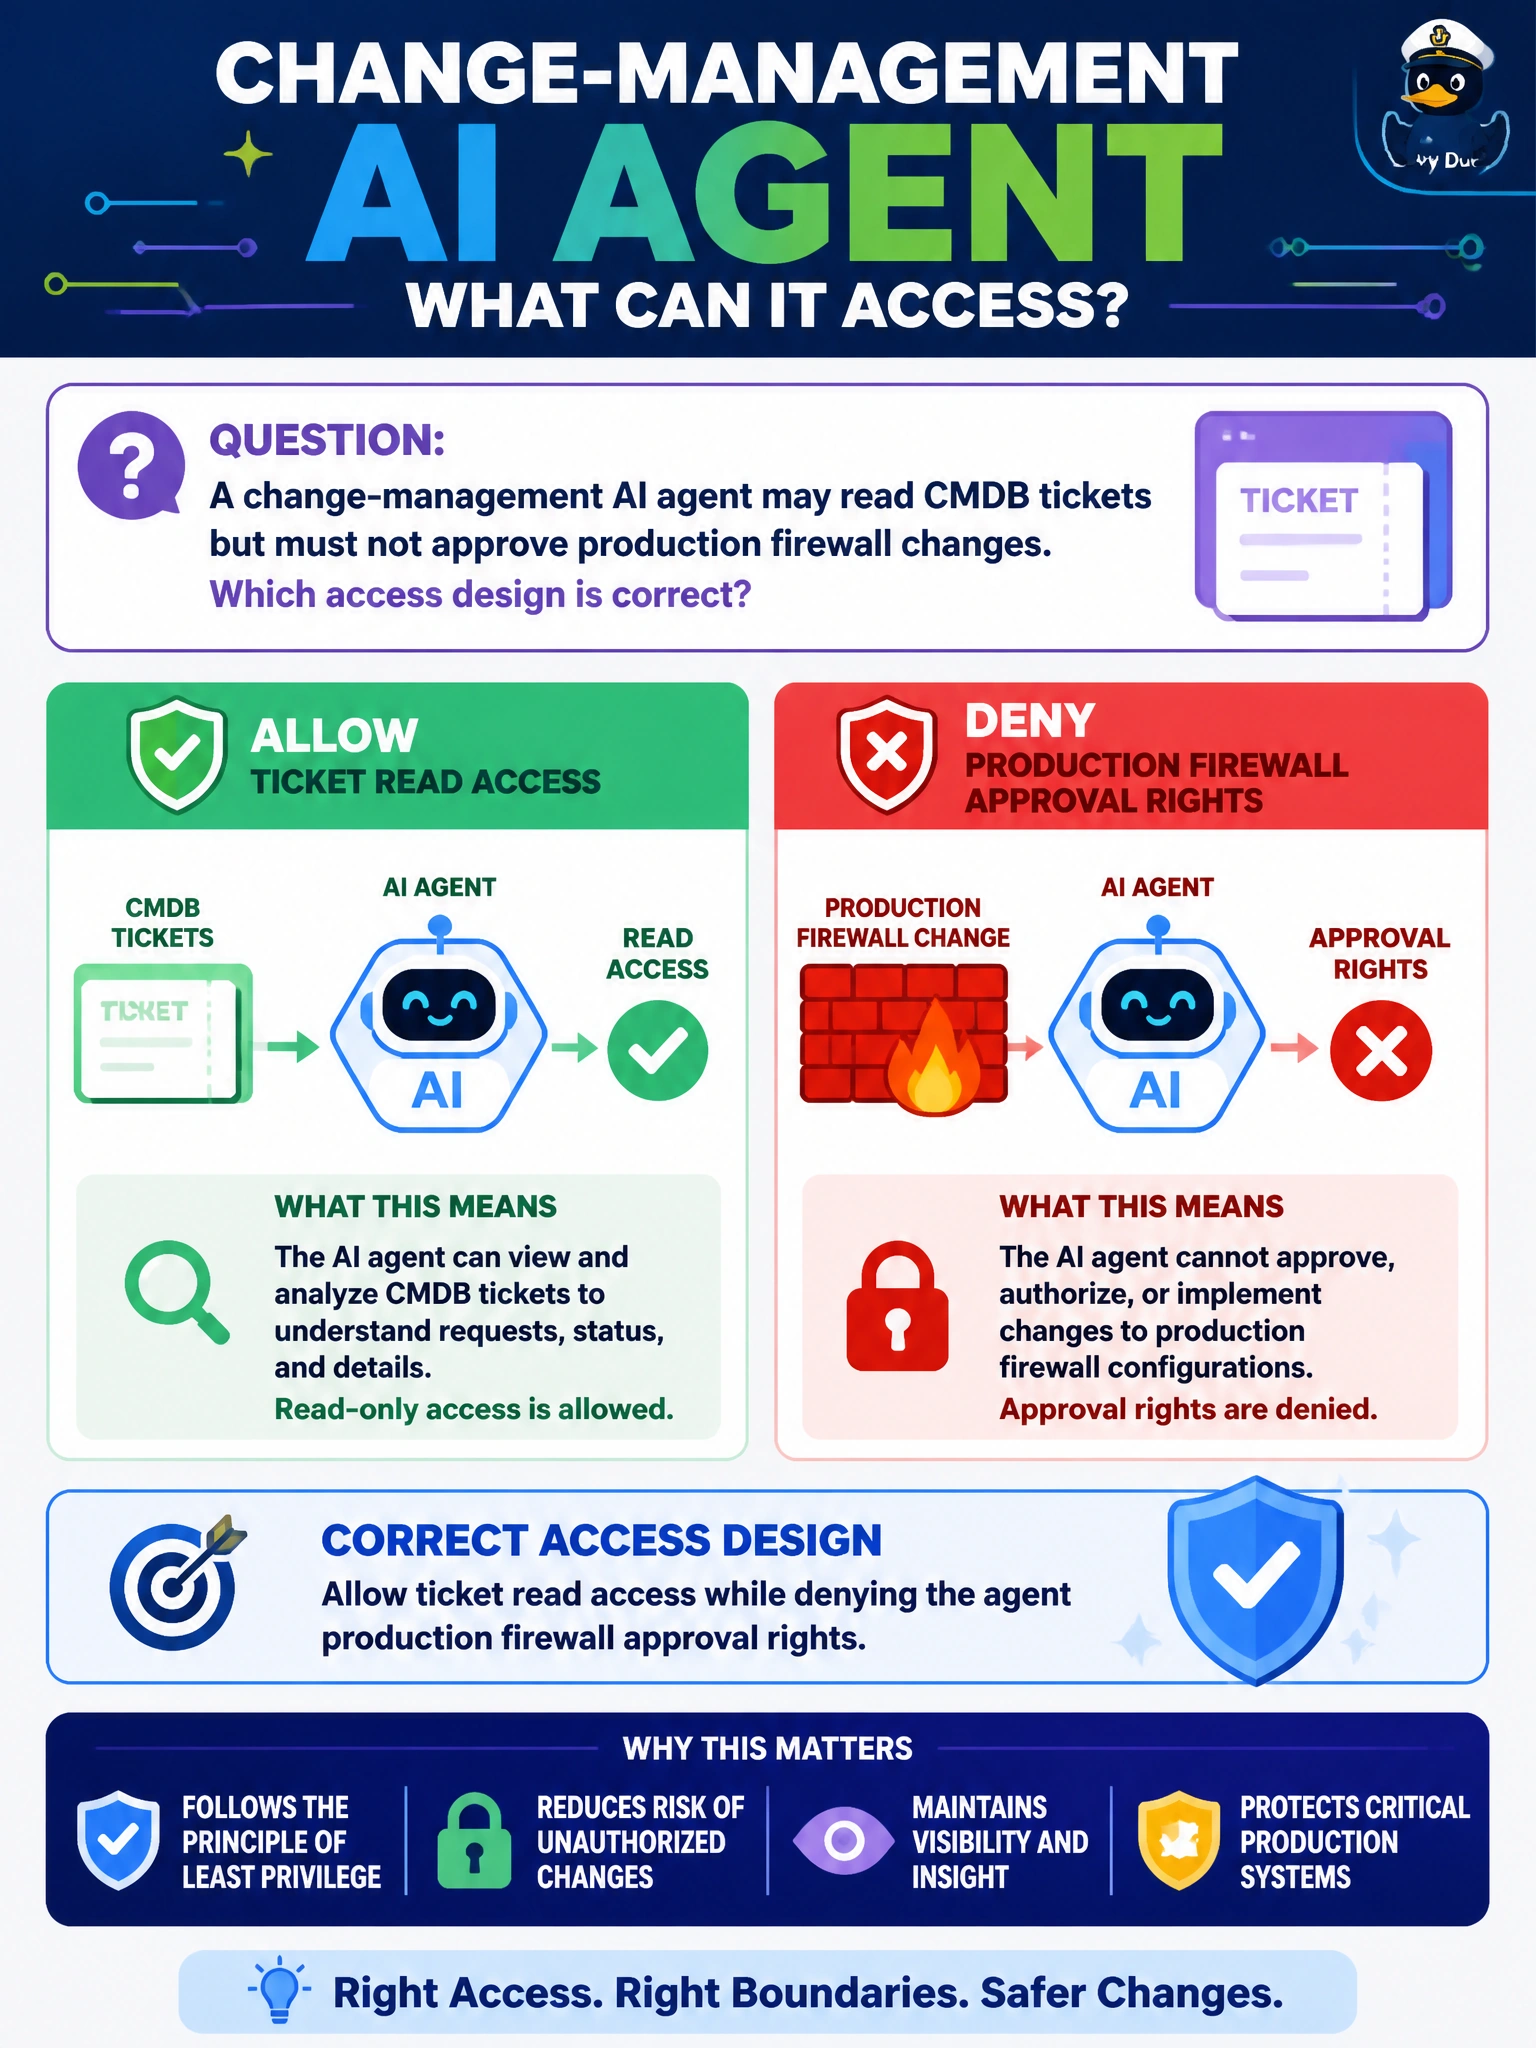
A change-management AI agent may read CMDB tickets but must not approve production firewall changes. Which access design is correct?
Select an answer to reveal the explanation.
Short Explanation
Reading the ticket board is fine; slamming production firewall rules is not. Constrain the agent to ticket reads and deny approval rights. You can't enforce denial by just instructing the agent to skip production approvals, and you won't fix risk by denying filing rights while leaving approval rights open.
Full Explanation
Allowing CMDB ticket read access while denying the agent production firewall approval rights is the correct access design for a change-management AI agent. Agent permissions should separate assistive analysis from high-impact change authority. Reading tickets helps summarize and triage municipal change work; approving production firewall changes can alter network security posture citywide and must remain with authorized humans or tightly controlled change workflows—not an unsupervised agent.
Allowing ticket read access while instructing the agent to skip production firewall approvals still relies on a prompt instruction rather than enforced access denial—prompt text can be ignored, overridden, or bypassed and does not satisfy the requirement to deny the agent production firewall approval rights. Allowing ticket read access while denying the agent production firewall request filing rights fails because it denies the wrong action—it blocks filing or drafting requests while leaving production firewall approval unaddressed, violating the requirement to deny the agent production firewall approval rights. Allowing ticket read access while denying the agent production CMDB ticket approval rights fails because it denies the wrong scope—it leaves production firewall approval unaddressed, violating the requirement that the agent must never hold production approval authority.
Exam caveat: Agent access questions often contrast read/summarize rights with approve/execute rights on production controls. Denying production CMDB ticket approval while leaving production firewall approval unaddressed is a severe distractor.
Operational check: Grant the change agent CMDB ticket read only, deny firewall approval and push actions, attempt an approval (blocked), confirm ticket summaries still work, ensure no firewall secrets sit in prompts, and require MFA-bound human identities for production firewall changes.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.