
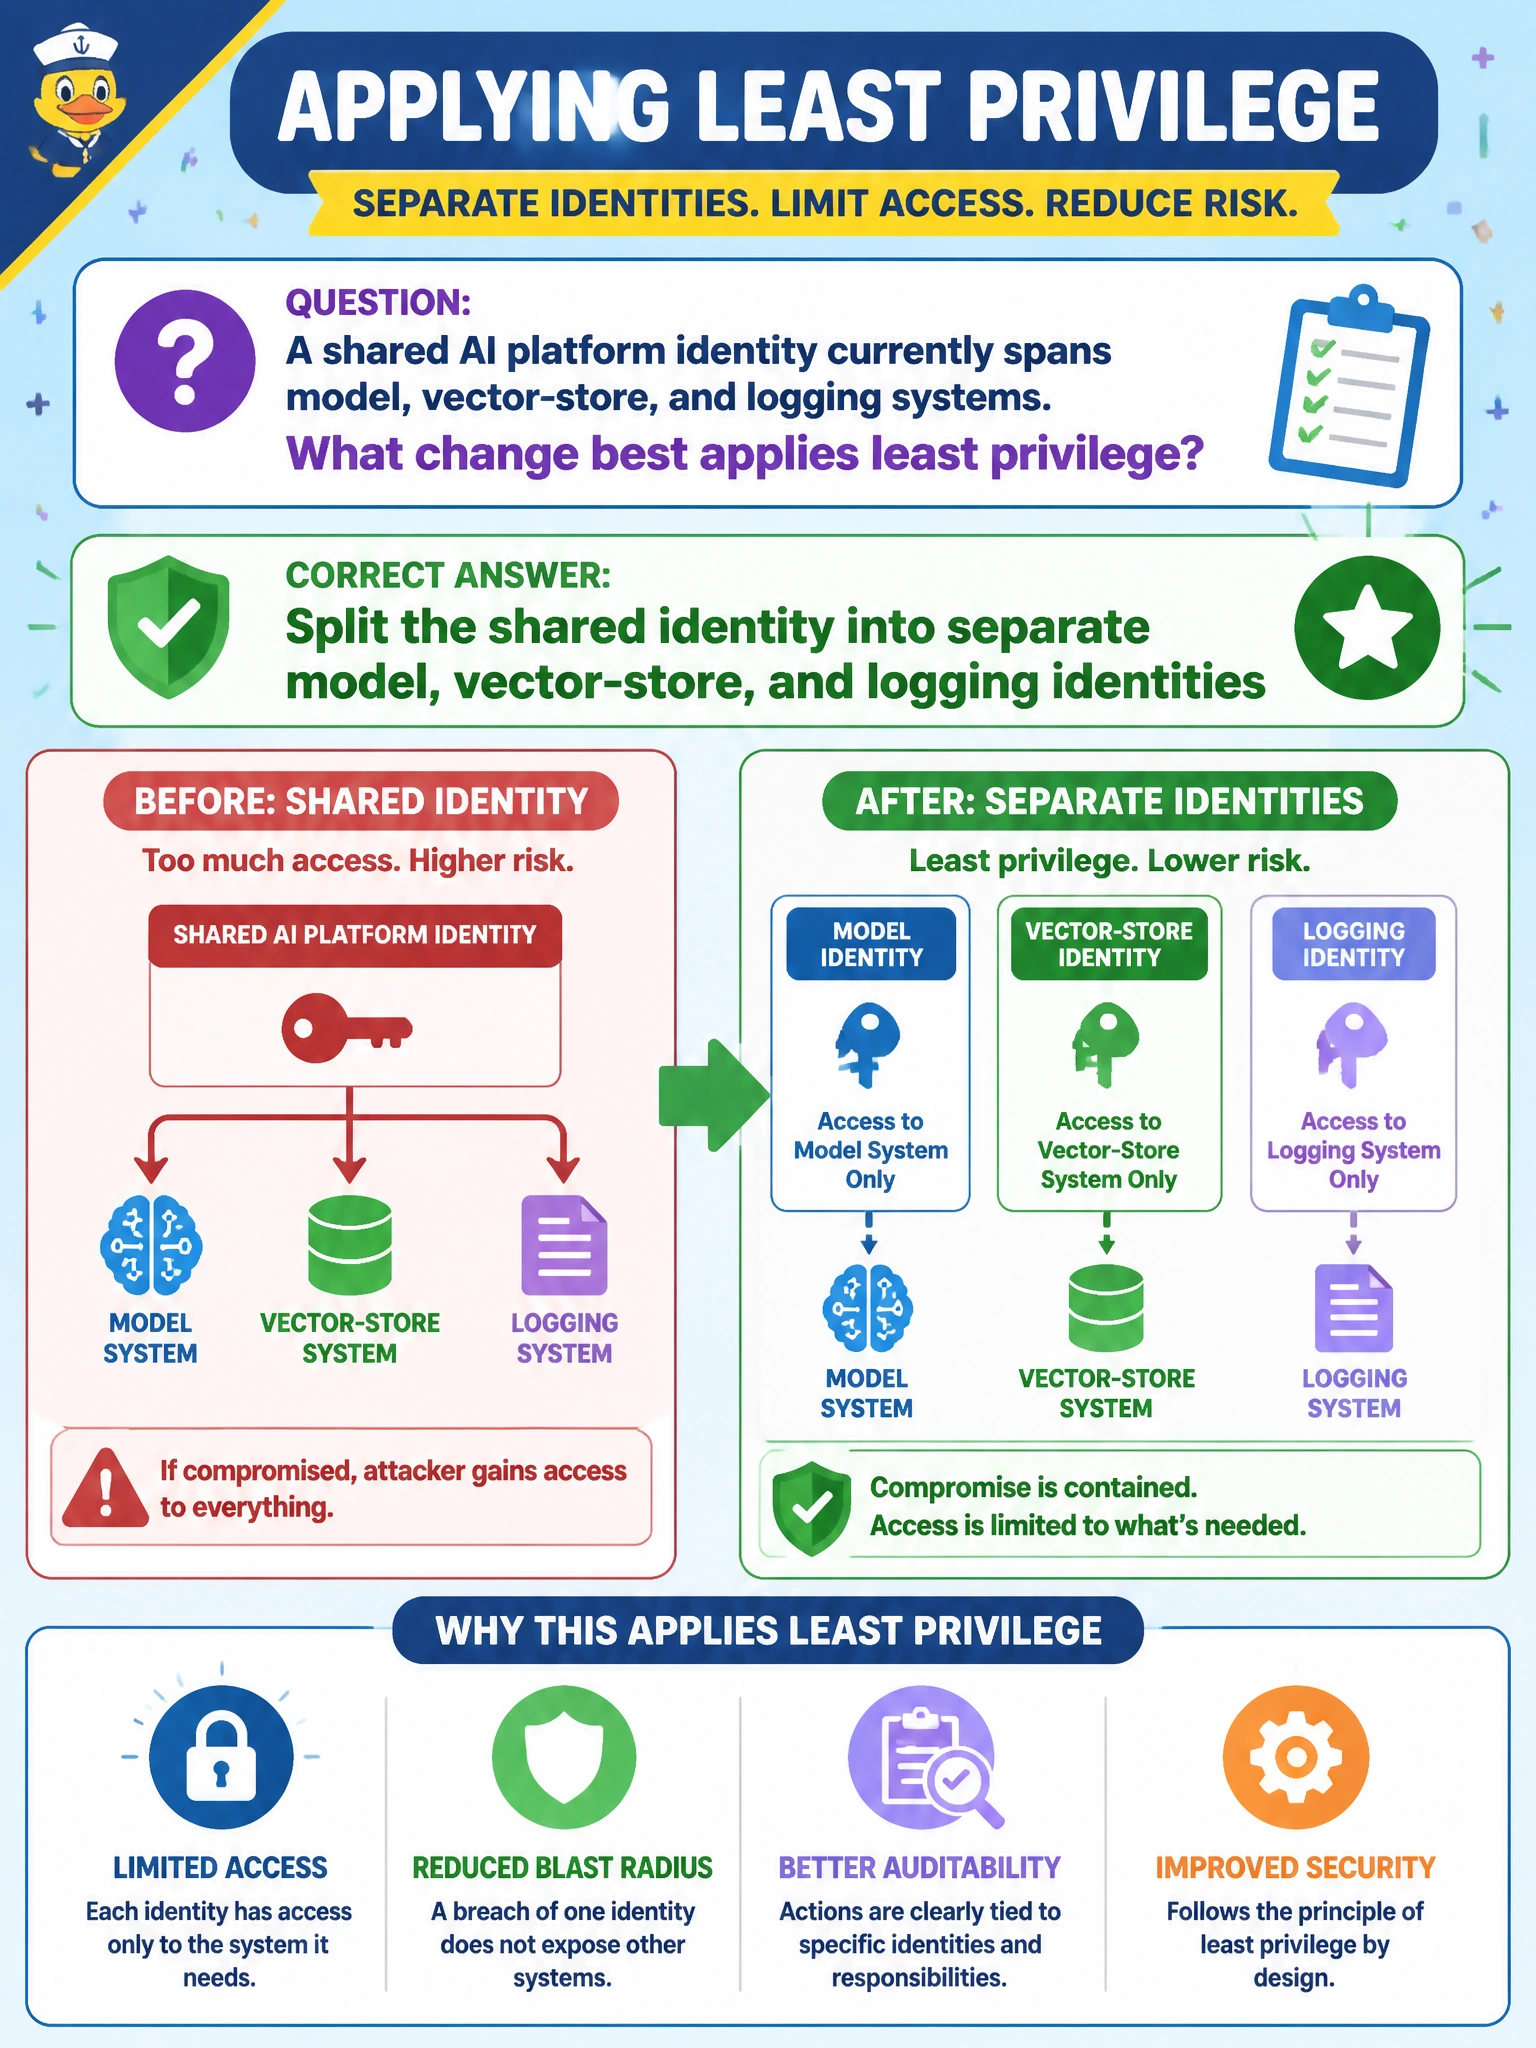
A shared AI platform identity currently spans model, vector-store, and logging systems. What change best applies least privilege?
Select an answer to reveal the explanation.
Short Explanation
One master key for model, vectors, and logs is a single point of disaster. Split into separate identities so each AI component only gets what it needs. Keeping that one shared identity but making it read-only won't help you, since you'll still have one key spanning everything and you'll break the writes your model, vectors, and logs need to work.
Full Explanation
Splitting the shared identity into separate model, vector-store, and logging identities best applies least privilege when one platform identity currently spans those systems. Distinct service identities limit blast radius: compromise of a logging credential should not yield vector-store write or model-admin rights, and vice versa. Municipal AI platforms that share one identity across model invocation, RAG storage, and telemetry concentrate risk and complicate audit attribution.
Scoping the shared identity to read-only permissions for model, vector-store, logging fails by concept because keeping one identity across all three planes leaves blast radius intact and a blanket read-only scope is not least privilege; least privilege requires separate identities that each hold only the permissions its own plane needs, including necessary writes. Restricting the shared identity with source IP checks for model, vector-store, logging fails because network location checks do not limit what the shared identity can do once the check passes; an allowed address can still exercise excessive model, vector, or logging rights and does not apply least privilege. Enabling detailed audit logging for the shared identity across model, vector-store, logging fails by concept because audit logging records activity but does not reduce privileges; without splitting into scoped-down permissions it leaves the shared over-privileged rights in place and does not apply least privilege.
Exam caveat: Least privilege for AI platforms means separate identities (or roles) per plane—model, data/vector, and logging—with each scoped to minimum rights, not keeping the shared identity across all planes with read-only scoping, IP checks, or audit logging.
Operational check: Replace the shared platform identity with scoped model, vector-store, and logging identities; revoke the old shared principal; confirm each component works with only its own rights; and verify a stolen logging credential cannot invoke the model or modify vector indexes.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.