
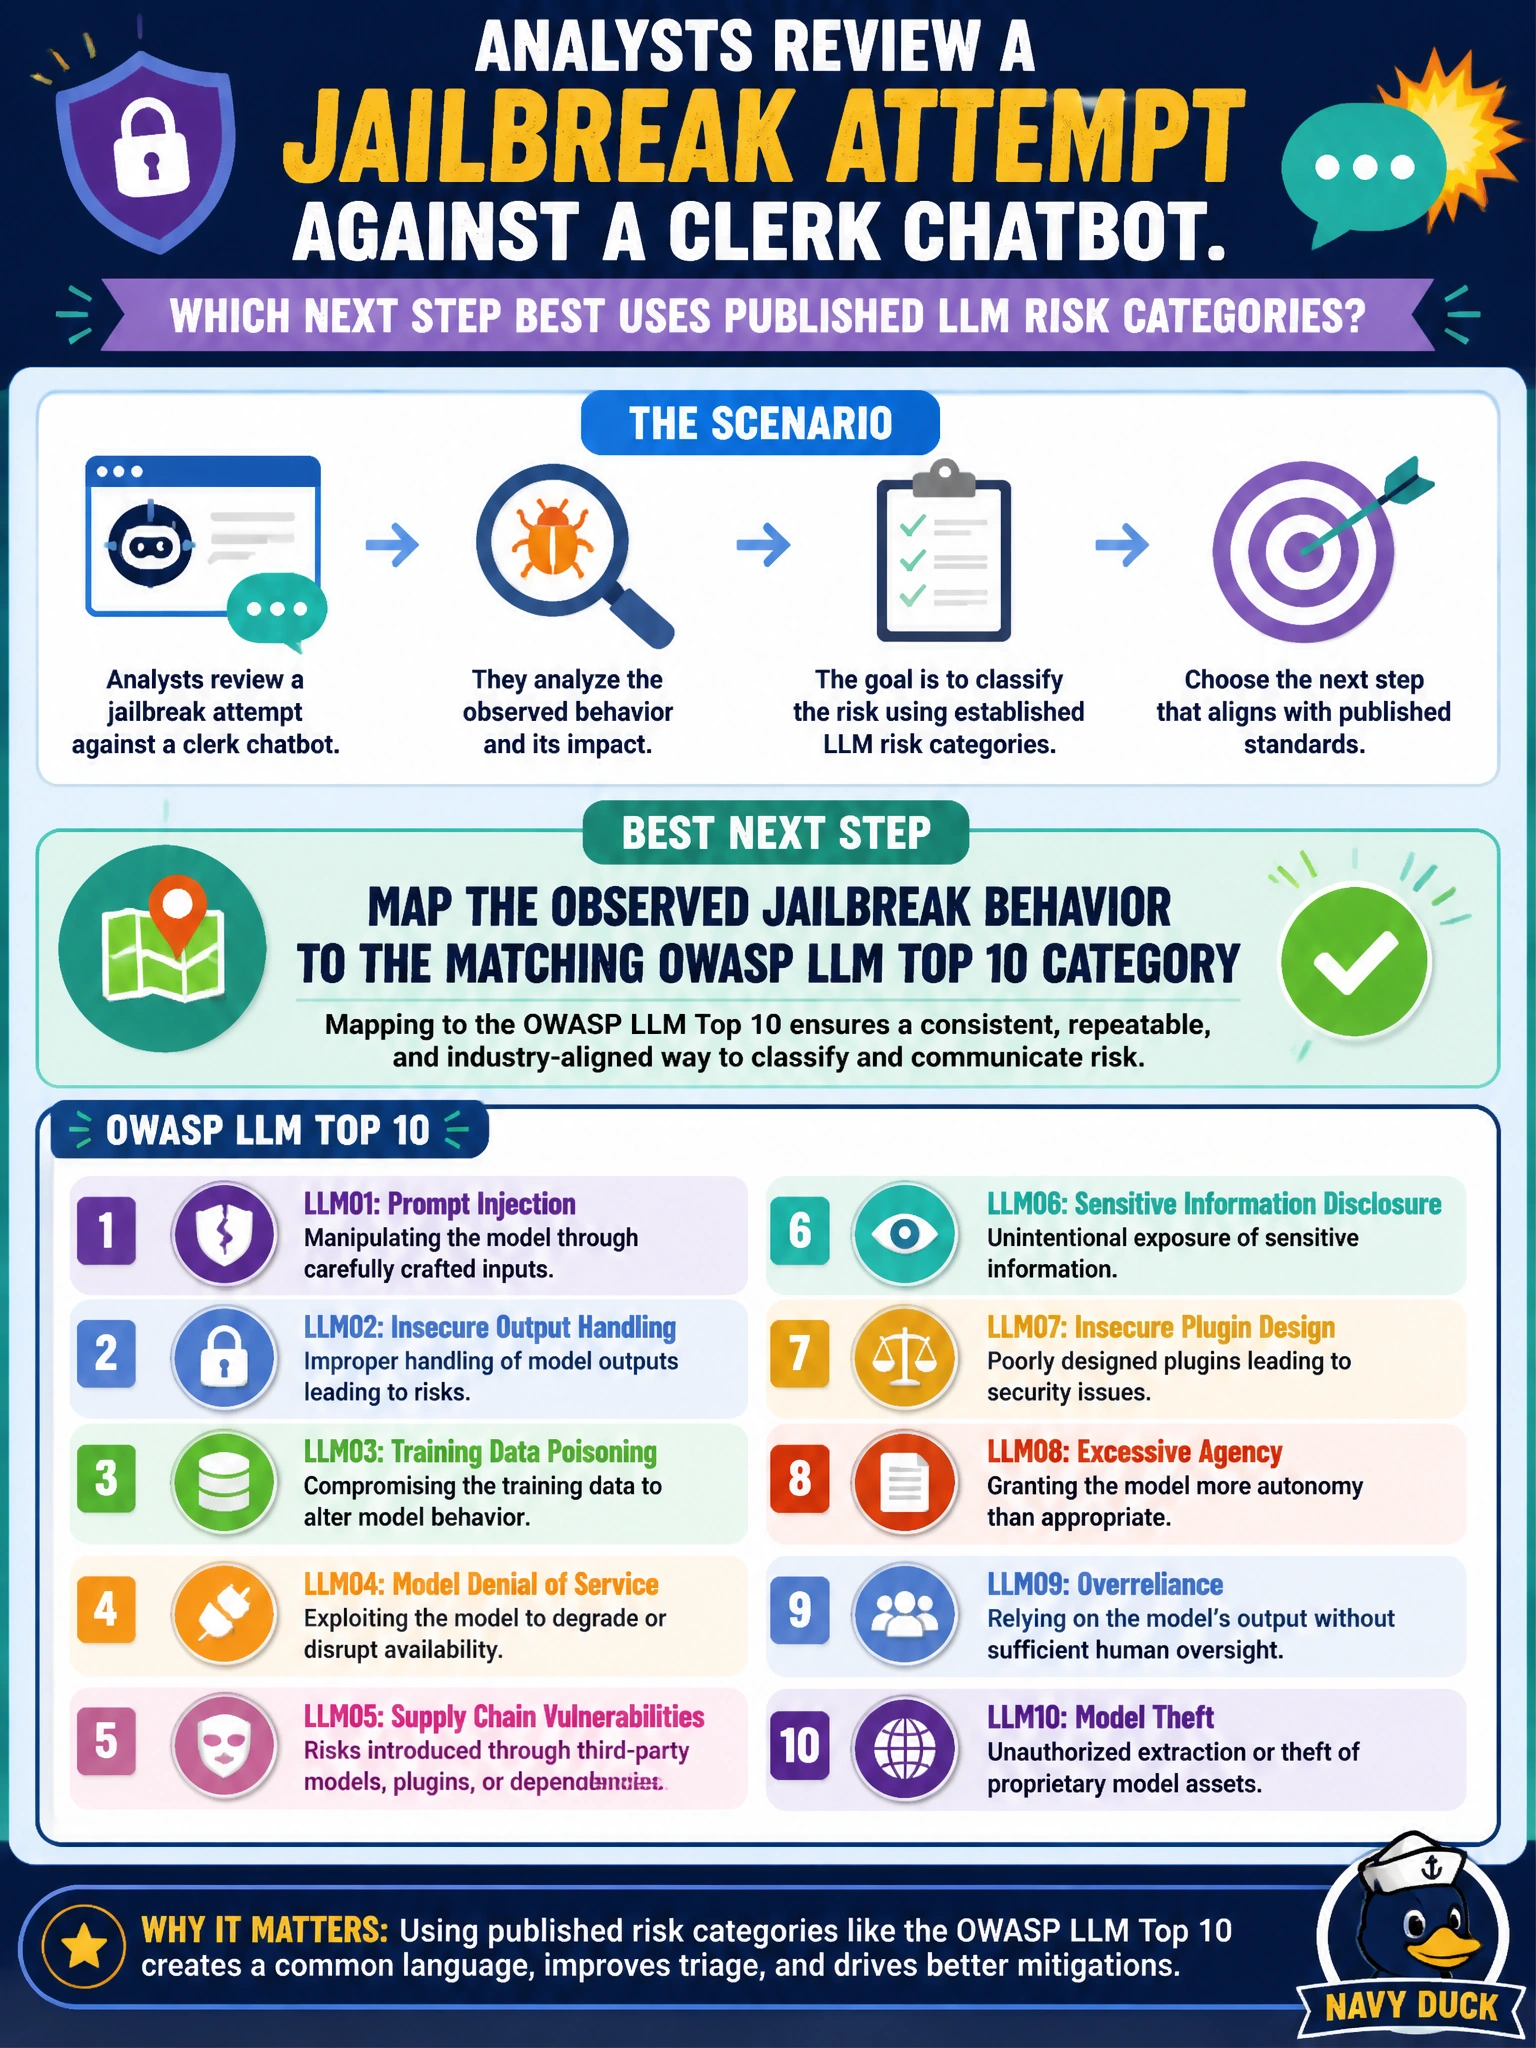
Analysts review a jailbreak attempt against a clerk chatbot. Which next step best uses published LLM risk categories?
Select an answer to reveal the explanation.
Short Explanation
Name the monster so the next shift recognizes it. Mapping the jailbreak to the right OWASP LLM category turns a one-off scare into reusable threat language. Don't file it as an ASVS web control, MASVS mobile control, or CVSS score — you've got an active jailbreak to contain, not a traditional web flaw, a mobile flaw, or a severity number.
Full Explanation
Published LLM risk categories turn one-off incidents into reusable municipal SOC language. When analysts review a jailbreak attempt against a clerk chatbot, the next step is to map the observed behavior to the matching OWASP LLM Top 10 category—commonly prompt injection or a related entry depending on the technique used. Category mapping standardizes severity discussion, highlights control gaps such as input filtering, output handling, or monitoring, and improves trend analysis across clerk-facing assistants so similar attempts are recognized quickly on later shifts. Mapping the jailbreak to the matching OWASP ASVS web control misapplies traditional web-application verification checks to an LLM-specific prompt-manipulation issue, so the SOC loses the prompt-injection language needed to drive input filtering and monitoring improvements. Mapping the event to the matching OWASP MASVS mobile control misattributes a runtime chatbot prompt-manipulation attempt to a mobile-platform security issue, which strips away the LLM-specific prompt-injection context needed for correct response. Mapping the jailbreak attempt to the matching CVSS vector severity score substitutes a severity number for LLM risk categorization, which does not identify the prompt-injection pattern or guide LLM-specific controls and trend analysis. Exam caveat: jailbreaks against LLM apps should be categorized as prompt manipulation under LLM risk taxonomies, not misfiled as a mobile-platform control gap under MASVS. Operational check: retain prompts and responses, tag the ticket with the OWASP LLM category, update detections and prompt-firewall rules, and brief adjacent chatbot owners on the observed pattern.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.