
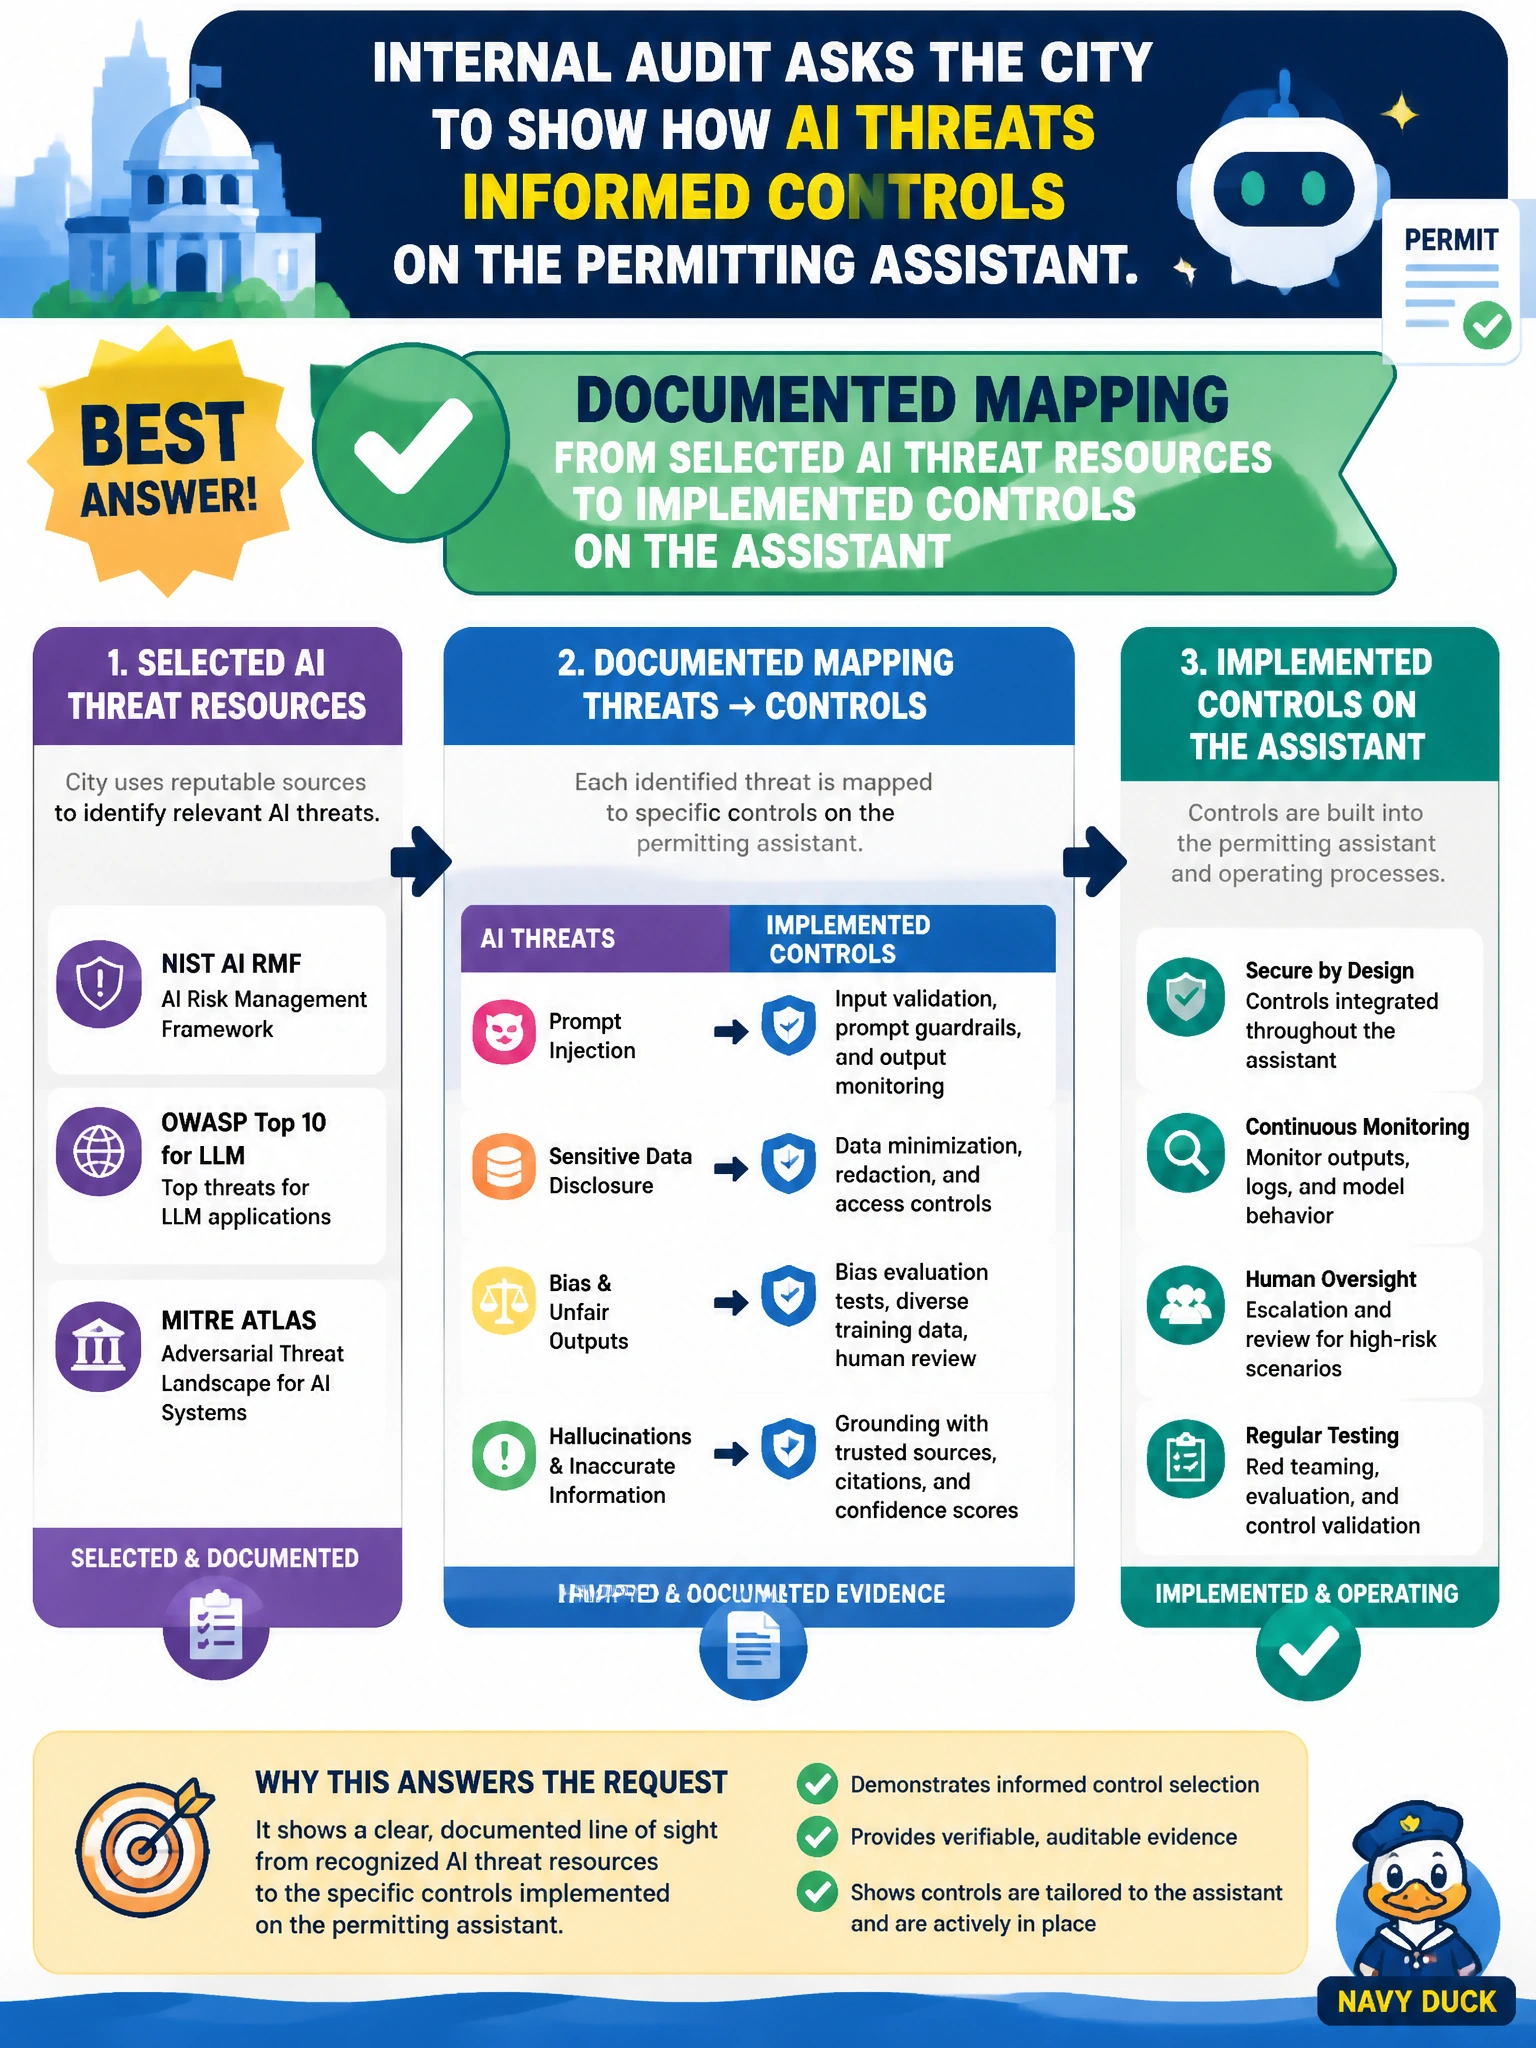
Internal audit asks the city to show how AI threats informed controls on the permitting assistant. Which evidence best answers that request?
Select an answer to reveal the explanation.
Short Explanation
You'll need a paper trail that links threats to controls, not a mapping from retired threat resources to controls or from threat resources to planned controls. Showing which AI threat resources drove which permitting-assistant controls closes that ask. A mapping from implemented controls back to threat resources won't prove your threats drove control selection either.
Full Explanation
Internal audit assurance for municipal AI hinges on evidence that identified threats drove control selection. Documented mapping from selected AI threat resources—such as OWASP LLM Top 10, MITRE ATLAS, or an adopted risk catalog—to implemented controls on the permitting assistant shows traceability from risks to mitigations. That artifact demonstrates intentional design rather than ad hoc tooling, supports repeatable reviews when the assistant changes, and answers how AI threats informed the control set in language auditors can sample and re-perform. Without a mapping, the city cannot prove that gateway filters, logging, or human review were chosen for specific AI abuse cases.
A documented mapping from retired AI threat resources to implemented controls on the assistant traces controls to outdated sources rather than to selected AI threat resources, so it does not show how current AI threats informed the controls and fails as audit evidence. A documented mapping from selected AI threat resources to planned controls on the assistant stops at planned controls rather than tracing to implemented controls, so it fails as evidence that AI threats informed the implemented controls. A documented mapping from implemented controls on the assistant to selected AI threat resources traces backward from controls to threats rather than showing threats drove control selection, so it does not demonstrate how AI threats informed the controls in a way auditors can sample and re-perform.
Exam caveat: auditors expect documented threat-to-control traceability for civic AI systems, not retired-threat-resource-to-control mappings, threat-resource-to-planned-control mappings, or control-to-threat-resource mappings. Operational check: maintain a living matrix linking each accepted threat resource item to specific permitting-assistant controls, owners, and test evidence, and present that matrix during internal audit fieldwork.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.