
A SOC lead needs to describe an attempted model-theft campaign against a municipal LLM API using adversarial AI techniques. Which resource is most appropriate?
Select an answer to reveal the explanation.
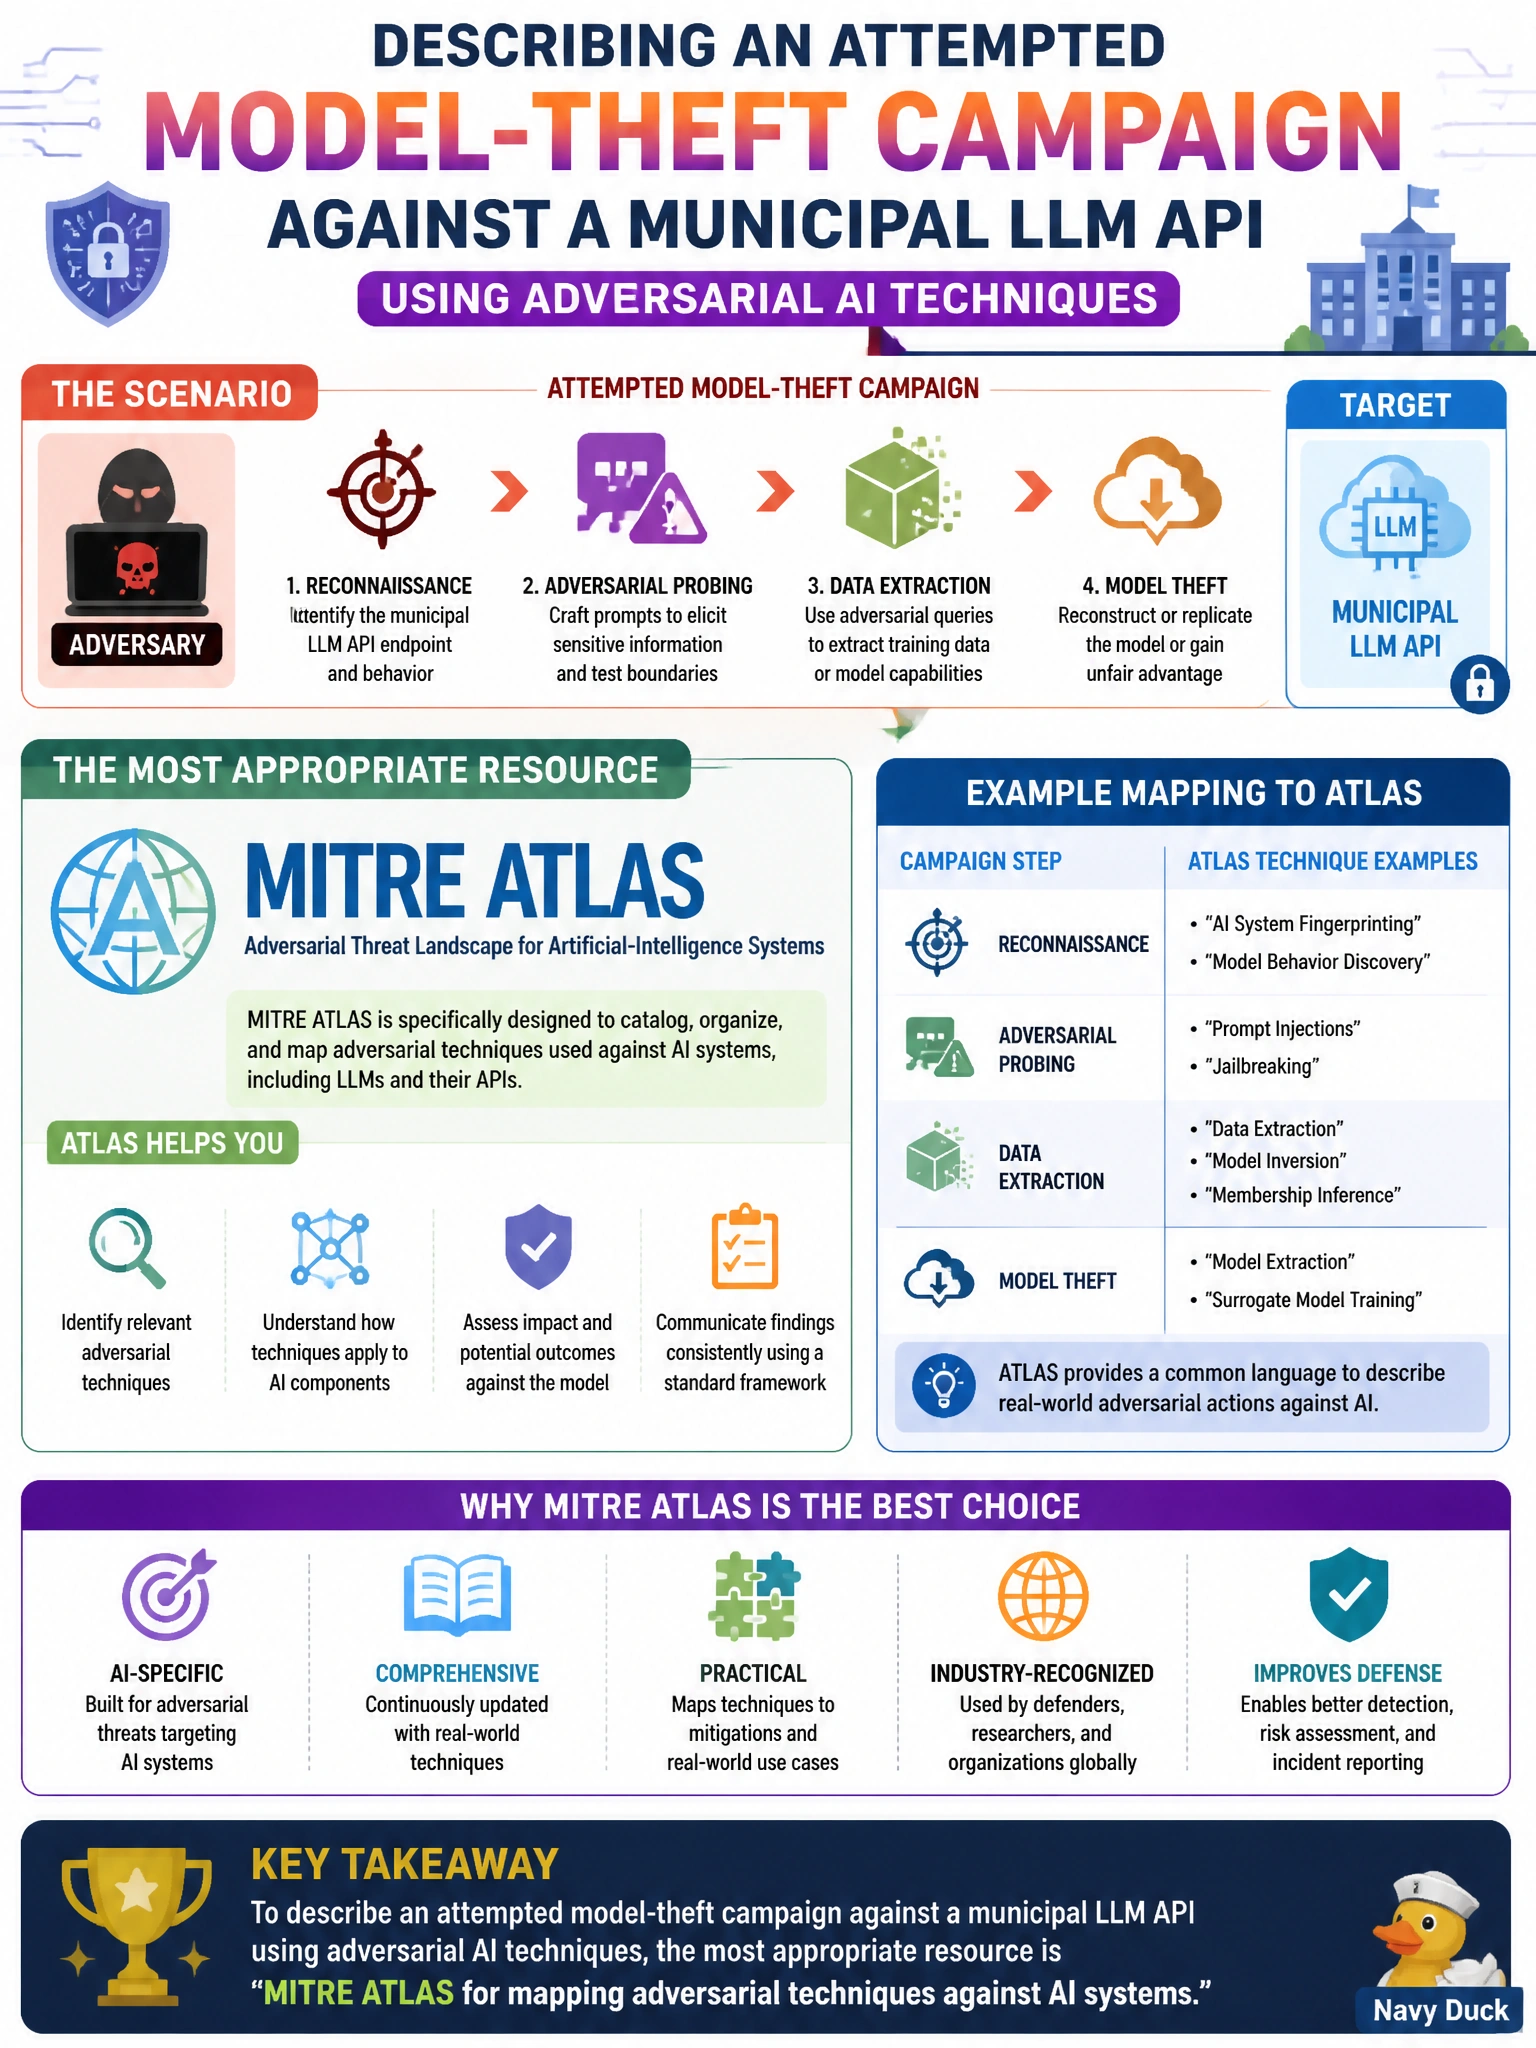
Short Explanation
Model theft is an AI fight, so you need an AI playbook. MITRE ATLAS gives SOC leads technique language for adversarial AI campaigns against municipal models. OWASP Top 10 for LLM lists risks, but it won't give you the adversary technique names for an API model-theft campaign.
Full Explanation
When a municipal SOC must describe adversarial activity against an AI system, it needs a technique framework designed for AI/ML—not generic office trivia. MITRE ATLAS maps adversary tactics and techniques targeting AI systems, including reconnaissance against model endpoints, resource development, initial access, model theft and exfiltration, evasion of detectors, and related procedures. Using ATLAS lets the SOC lead label an attempted model-theft campaign against a municipal LLM API with shared technique IDs, improve detection hypotheses, correlate gateway telemetry, and communicate consistently with peers, vendors, and leadership. Technique-level naming also feeds purple-team exercises and control gap analysis for API authentication, rate limits, and output monitoring.
MITRE ATT&CK maps enterprise intrusion tactics and techniques, but it is built for traditional IT infrastructure rather than AI/ML systems, so it lacks the AI-specific model-theft techniques needed for an LLM API campaign. OWASP Top 10 for LLM lists critical LLM application risks, but it is a risk catalogue rather than an adversary technique framework, so it lacks the structured, technique-level taxonomy spanning reconnaissance, access, and exfiltration that ATLAS provides and cannot fully describe an API-based model-theft campaign. NIST AI RMF governs AI risks across the system lifecycle, but it is a risk-management framework, not an adversary technique mapping, so it does not provide technique-level IDs for describing an attempted model-theft campaign.
Exam caveat: ATLAS is the go-to mapping resource for adversarial techniques against AI systems in exam and operational scenarios. Operational check: ticket the incident with ATLAS technique IDs, correlate API abuse telemetry to those techniques, update detection content for similar model-exfiltration patterns, and brief application owners on required API hardening.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.