
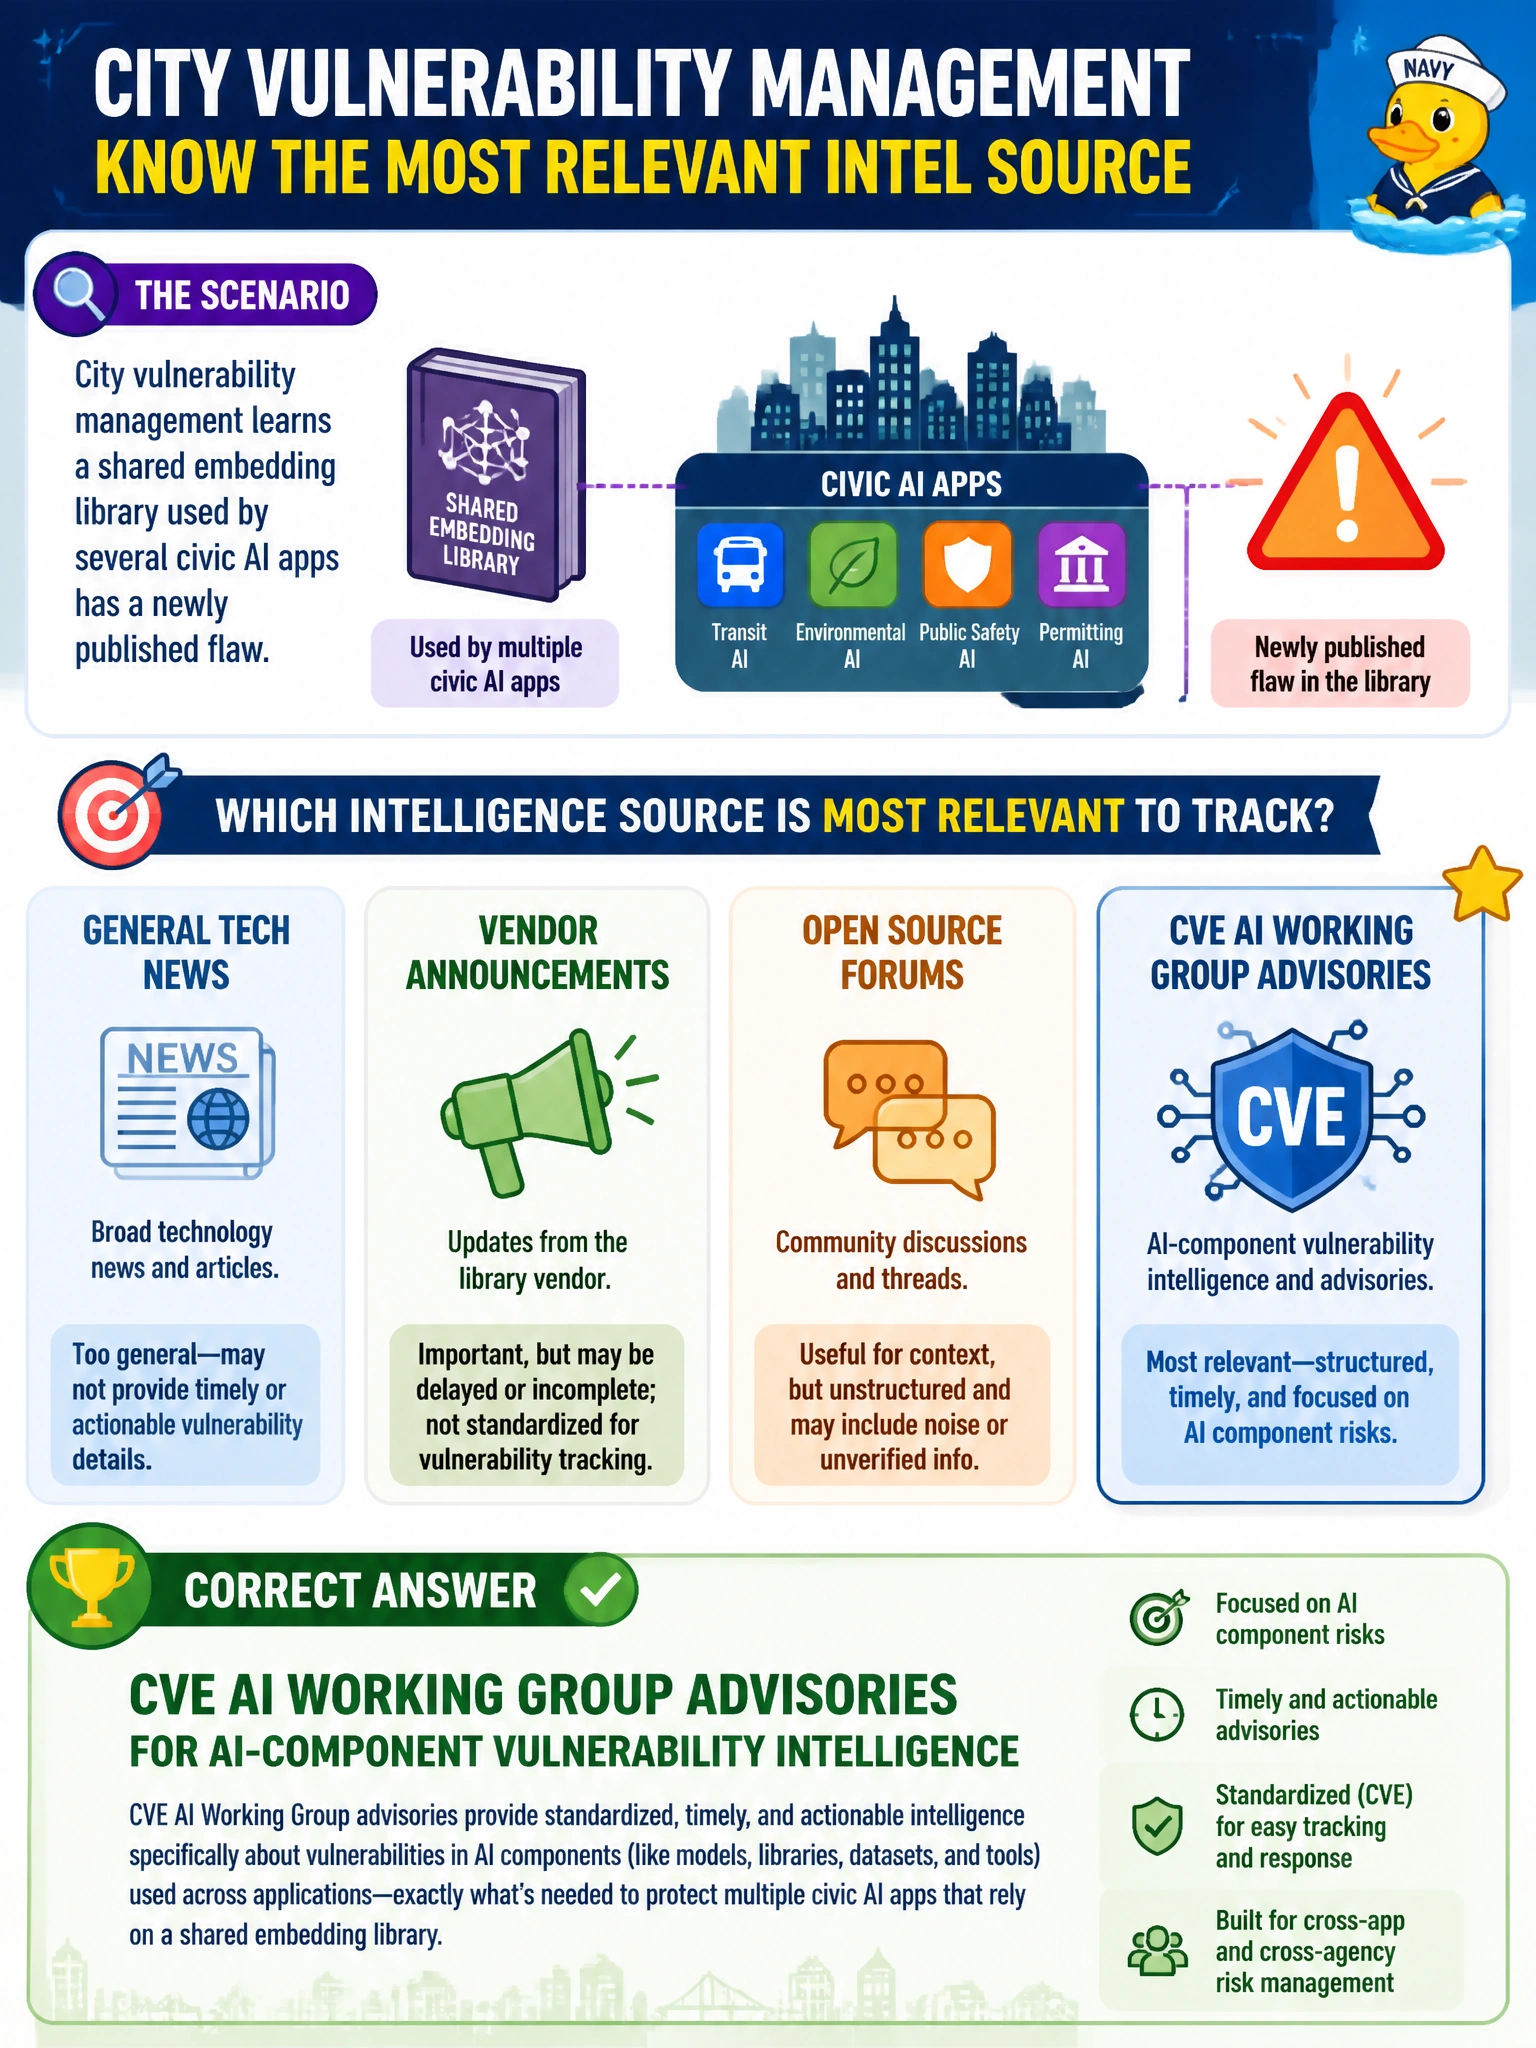
City vulnerability management learns a shared embedding library used by several civic AI apps has a newly published flaw. Which intelligence source is most relevant to track?
Select an answer to reveal the explanation.
Short Explanation
When the embedding library cracks, you watch AI-aware CVE channels — not general NVD severity scores, which lack AI-specific context. The CVE AI Working Group helps cities spot flaws in shared AI components. Missing that feed means the same bug walks through every chatbot.
Full Explanation
Vulnerability intelligence for AI components must track advisories specific to AI libraries and tooling. When city vulnerability management learns a shared embedding library used by several civic AI apps has a newly published flaw, CVE AI Working Group advisories are the relevant intelligence source for AI-component vulnerabilities. Monitoring that stream helps prioritize patching, inventory affected municipal applications that share the library, and reduce the window where compromised embeddings or related packages expose multiple services through a common dependency. AI-focused CVE tracking also clarifies severity context that general IT news feeds often miss for model-adjacent components.
CISA Known Exploited Vulnerabilities catalog entries track enterprise exploitation activity, but they are not the AI-focused advisories needed for a shared embedding library flaw. NVD severity scores provide general software weakness impact analysis, but they do not supply the AI-component vulnerability intelligence required for municipal embedding libraries. OWASP LLM Top 10 guidance addresses secure AI application design patterns, not vulnerability disclosure for specific embedding libraries.
Exam caveat: AI software supply-chain flaws are tracked through AI-focused vulnerability intelligence such as CVE AI Working Group outputs, not unrelated civic operational feeds. Operational check: subscribe vuln management to CVE AI WG and related AI advisories, map the embedding library across civic apps via SBOM or software inventory, and patch or isolate affected services on a defined SLA with change tickets.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.