
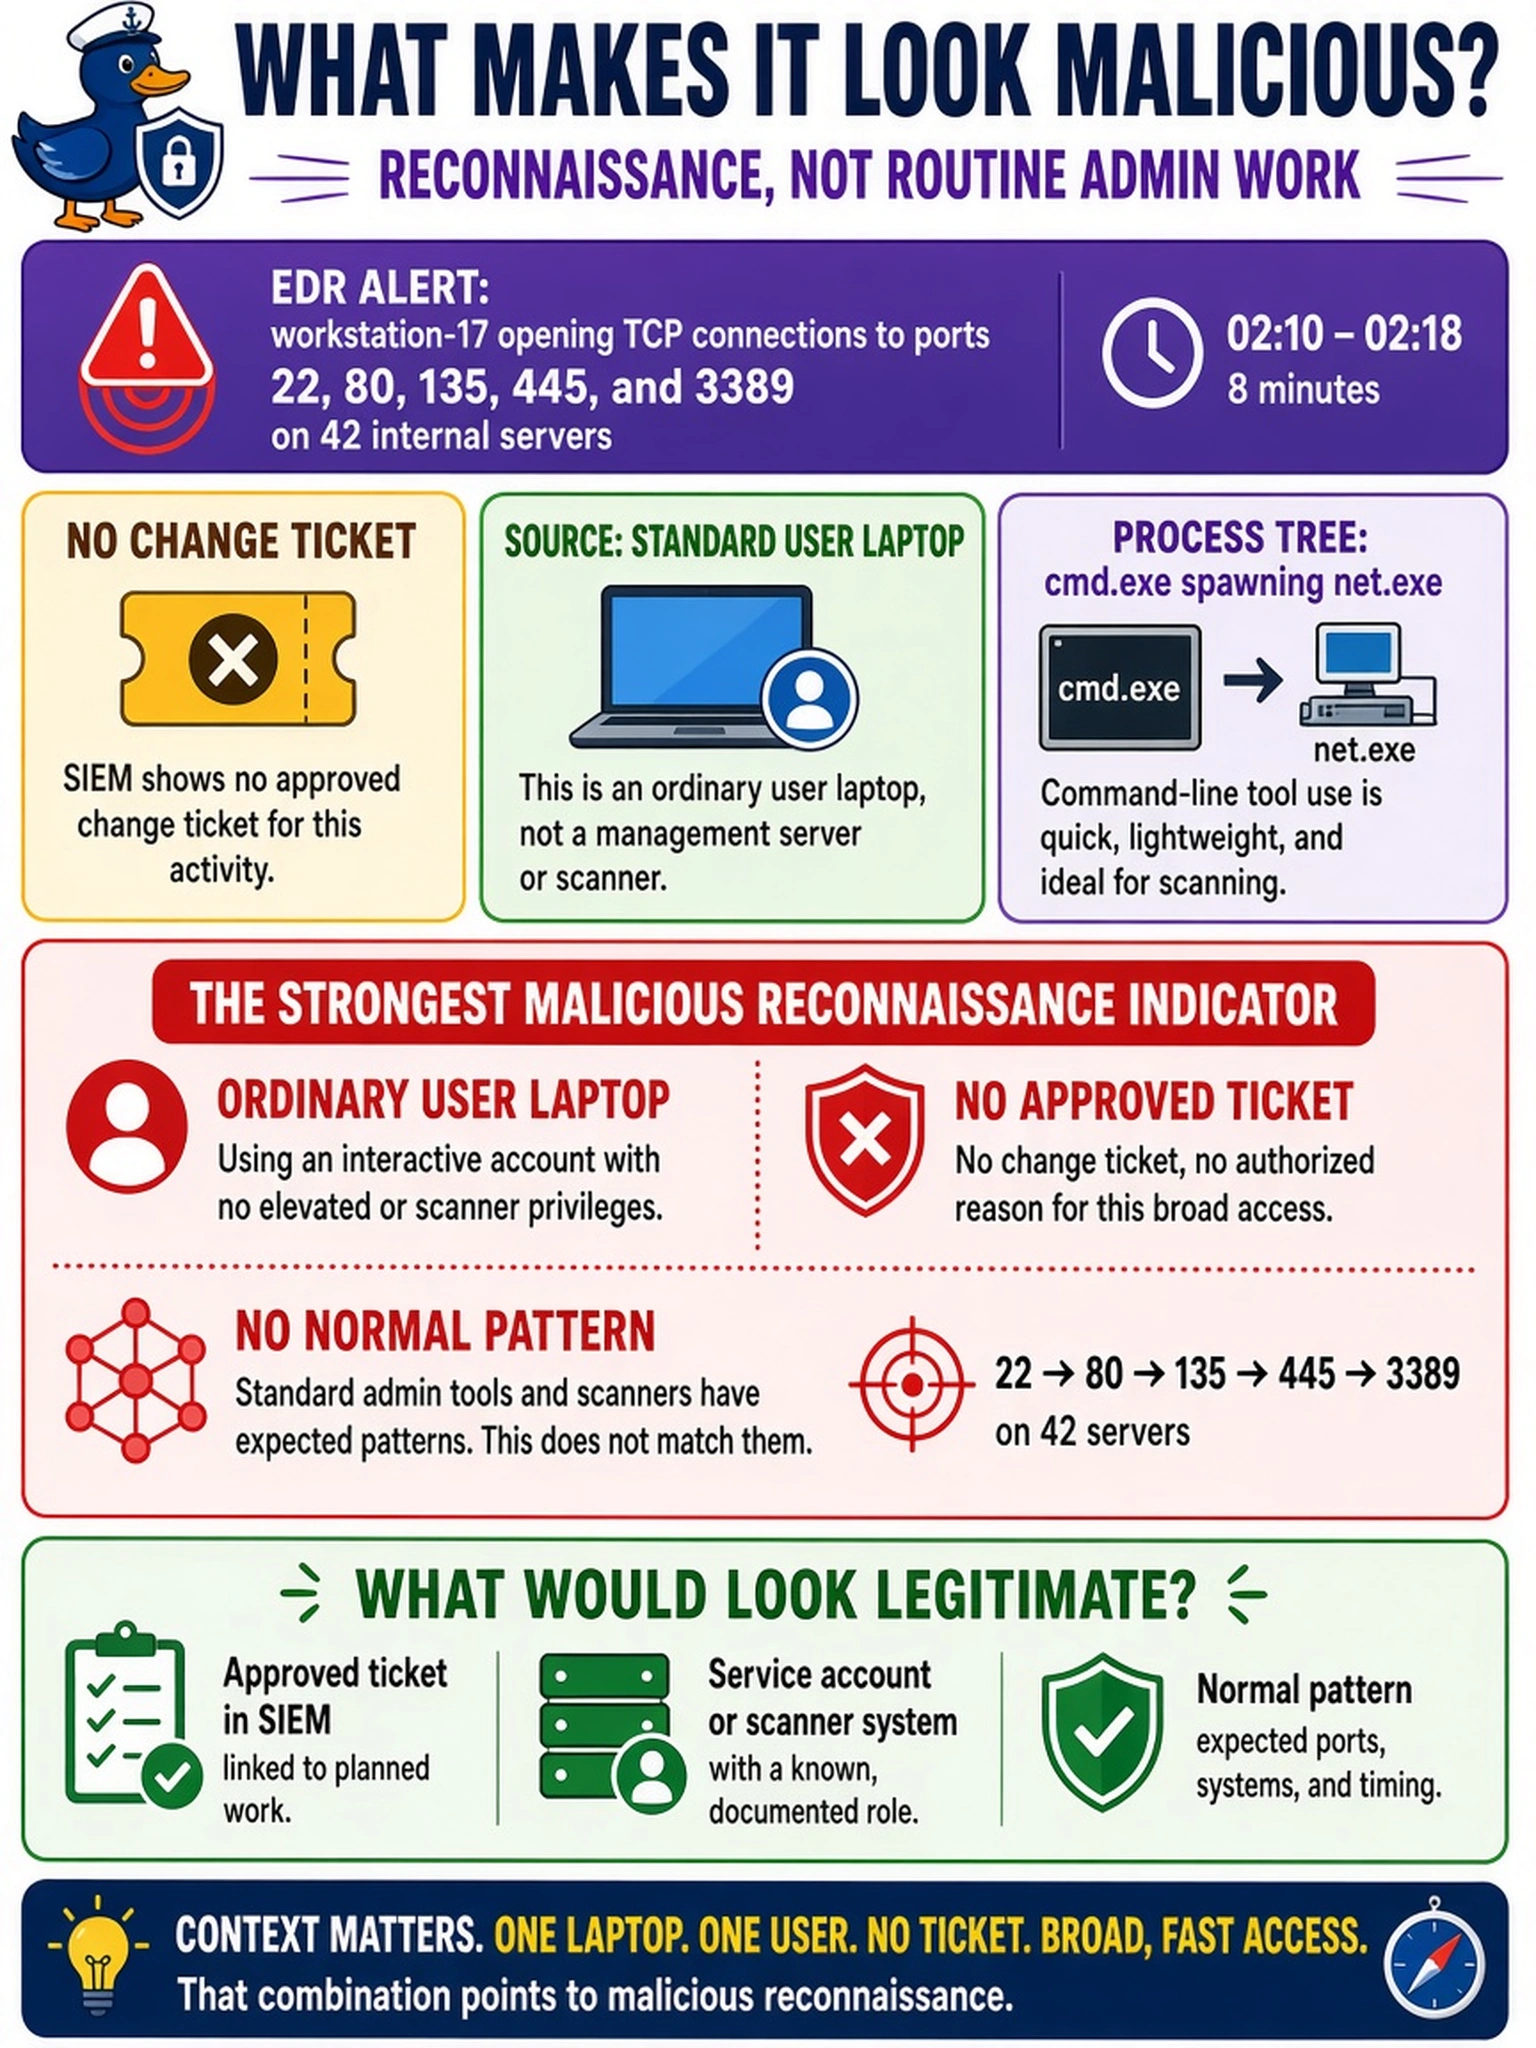
An EDR alert shows workstation-17 opening TCP connections to ports 22, 80, 135, 445, and 3389 on 42 internal servers between 02:10 and 02:18. The SIEM has no change ticket, the source is a standard user laptop, and the process tree includes cmd.exe spawning net.exe. Which finding most strongly indicates malicious reconnaissance rather than benign network administration?
Select an answer to reveal the explanation.
Short Explanation
Think of scanning like knocking on every door in a building: a maintenance tech with a work order looks normal, but a visitor knocking on forty doors at 2 a.m. doesn't. You want the context that separates approved admin work from recon: who ran it, why, and whether it fits the host's normal pattern. The trap is calling every port scan or native tool malicious without that context.
Full Explanation
Malicious reconnaissance is inferred from the convergence of actor, authority, timing, and behavior. A standard user endpoint that contacts many internal hosts across administrative ports, without a ticket or scanner service identity, creates an asset-discovery pattern consistent with lateral movement preparation. The analyst should correlate account type, approved change records, scanner exclusion lists, and historical access baselines before escalating. Targeting well-known ports is not conclusive because file sharing, remote desktop, and web administration can be legitimate. Native process names are weak indicators since administrators and malware can both use built-in utilities; process lineage, signing, and command-line arguments matter more. Off-hours timing increases suspicion but does not prove intent if backup, patching, or maintenance jobs run outside business hours. Exam caveat: Do not label scanning as malicious solely from destination ports, process names, or time of day; evaluate authorization and pattern deviation. Operational check: Query the SIEM for the source host's 30-day peer-to-peer port history and compare the alert to approved vulnerability-scanner schedules and change tickets.