
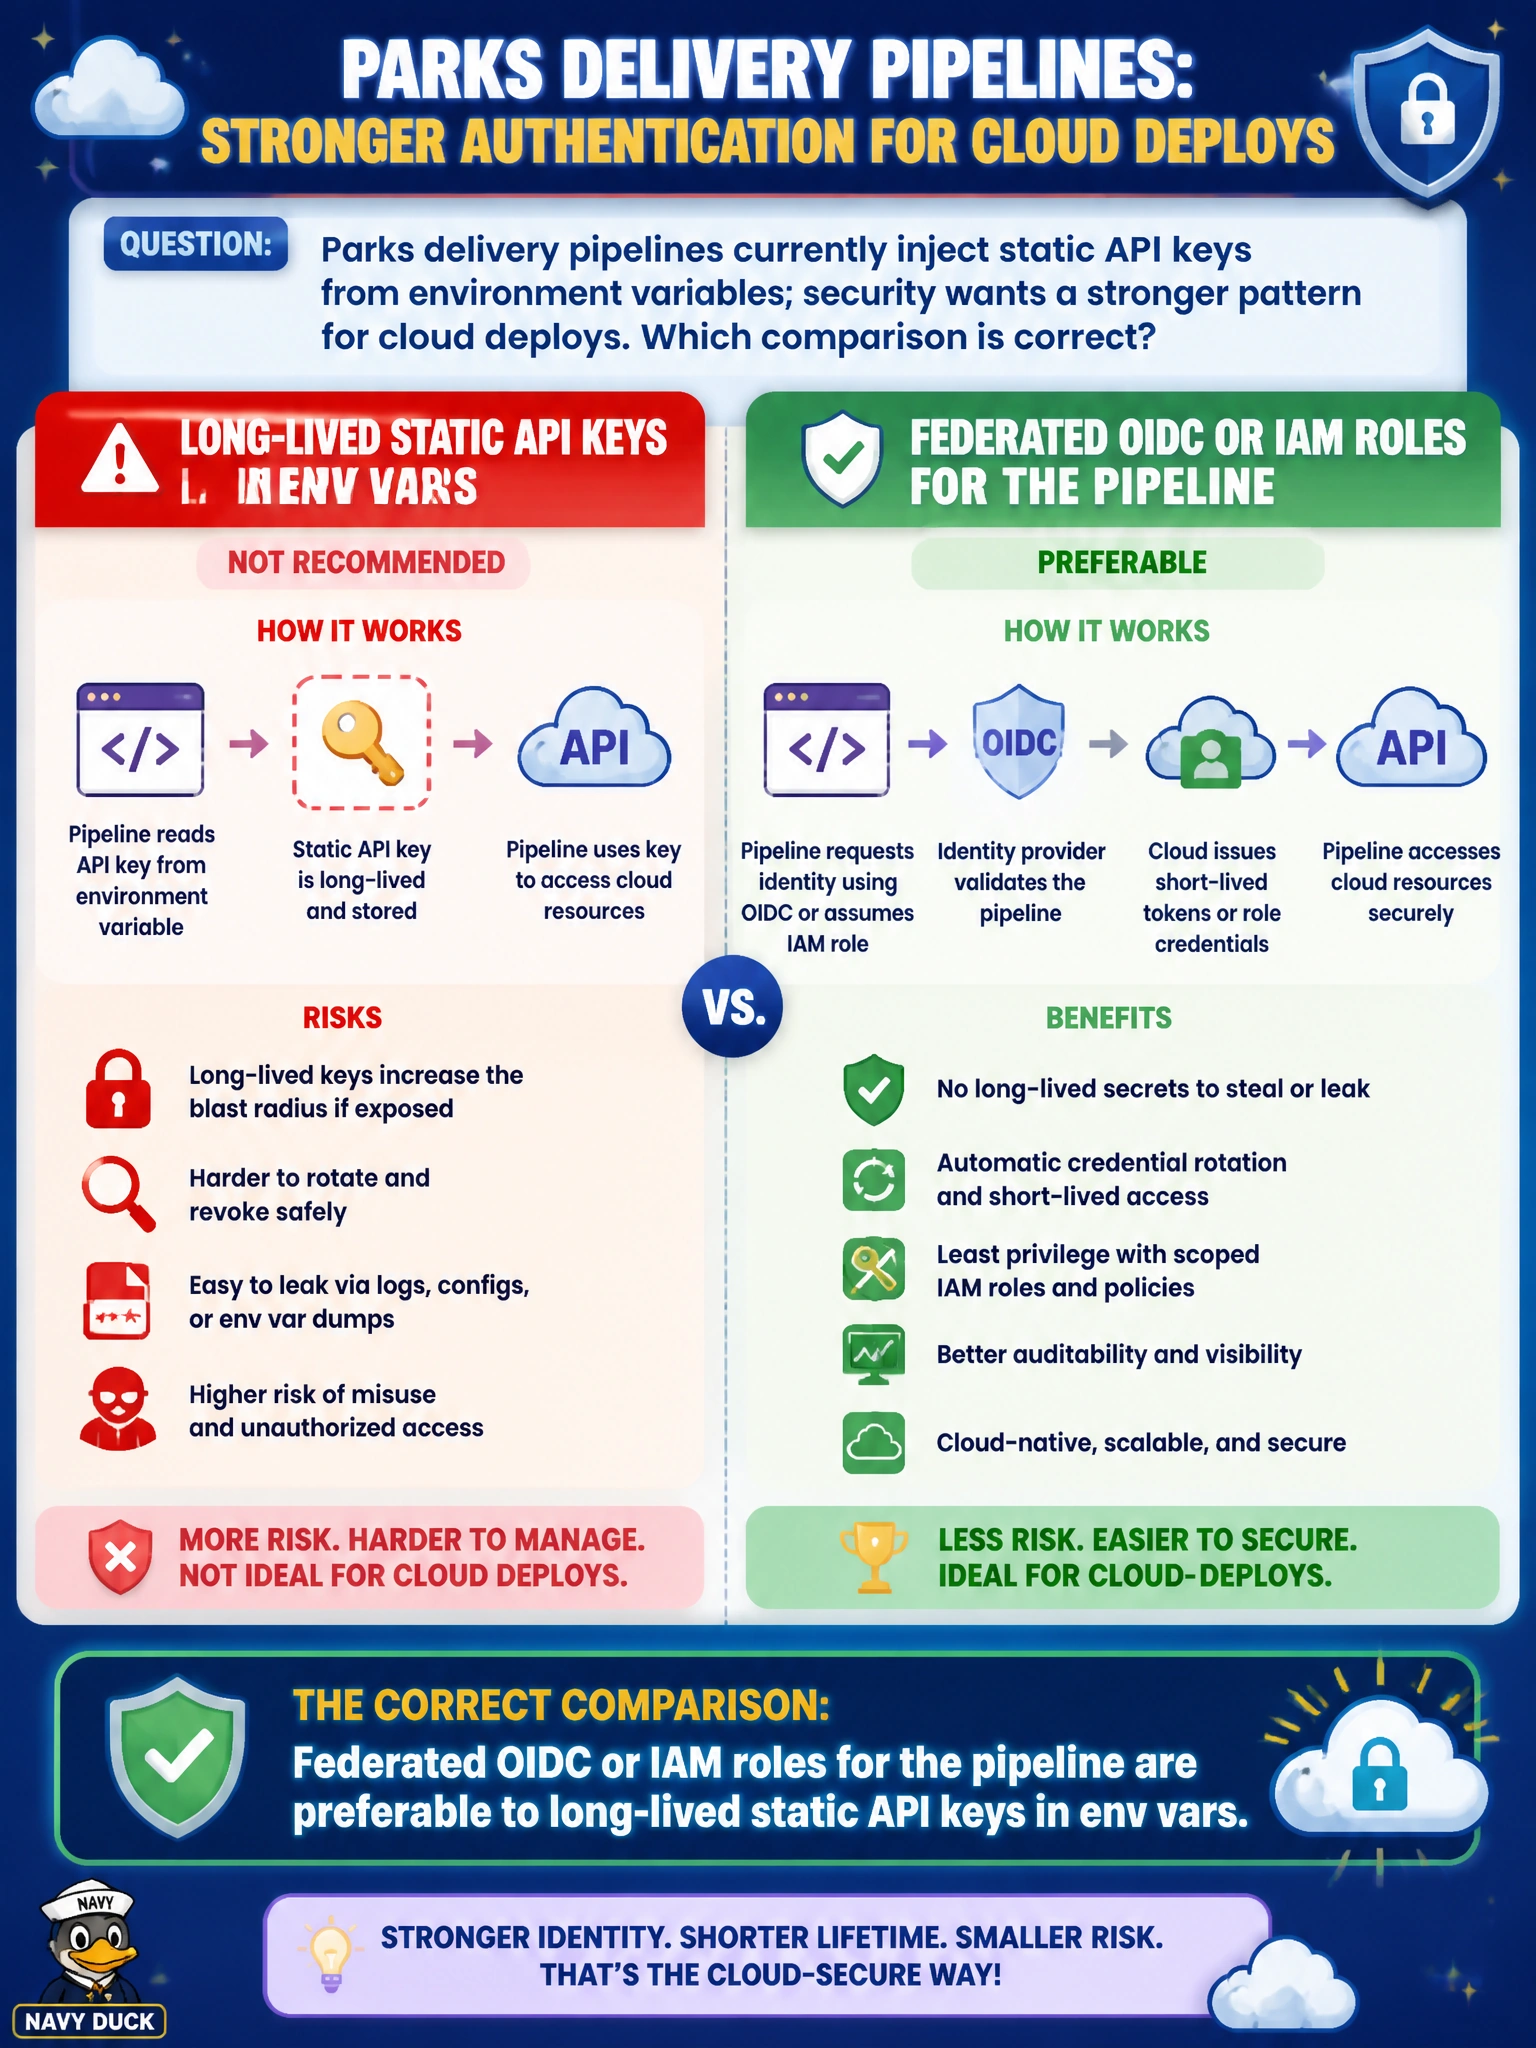
Parks delivery pipelines currently inject static API keys from environment variables; security wants a stronger pattern for cloud deploys. Which comparison is correct?
Select an answer to reveal the explanation.
Short Explanation
OIDC/IAM federation for CI is a temporary badge; static API keys in env vars are a badge that never expires. Prefer the badge that checks out when the job ends.
Full Explanation
Federated OIDC or IAM roles for CI issue short-lived, audience-bound credentials for cloud deploys, which is preferable to long-lived static API keys injected via environment variables. Parks delivery pipelines currently using static keys in env vars should move to federation so credentials expire with the job and are not standing secrets in variable stores or job logs.
Static API keys are not always safer than federated identity; they endure until rotated and leak easily through logs, variable exports, and screenshots. OIDC federation can and should be used from CI—it is designed for machine identity, not only interactive browser login by humans. Environment variables with static keys absolutely need rotation and audit; claiming they never do is false and leaves parks deploys with immortal credentials.
Exam caveat: configure trust conditions such as repository, branch, and environment on the OIDC identity provider so only intended parks pipelines can assume the deploy role. Operational check: replace static API keys with OIDC-to-IAM role assumption in the parks pipeline, delete or disable the old keys, and confirm deploys succeed with temporary sessions visible in cloud audit logs.