
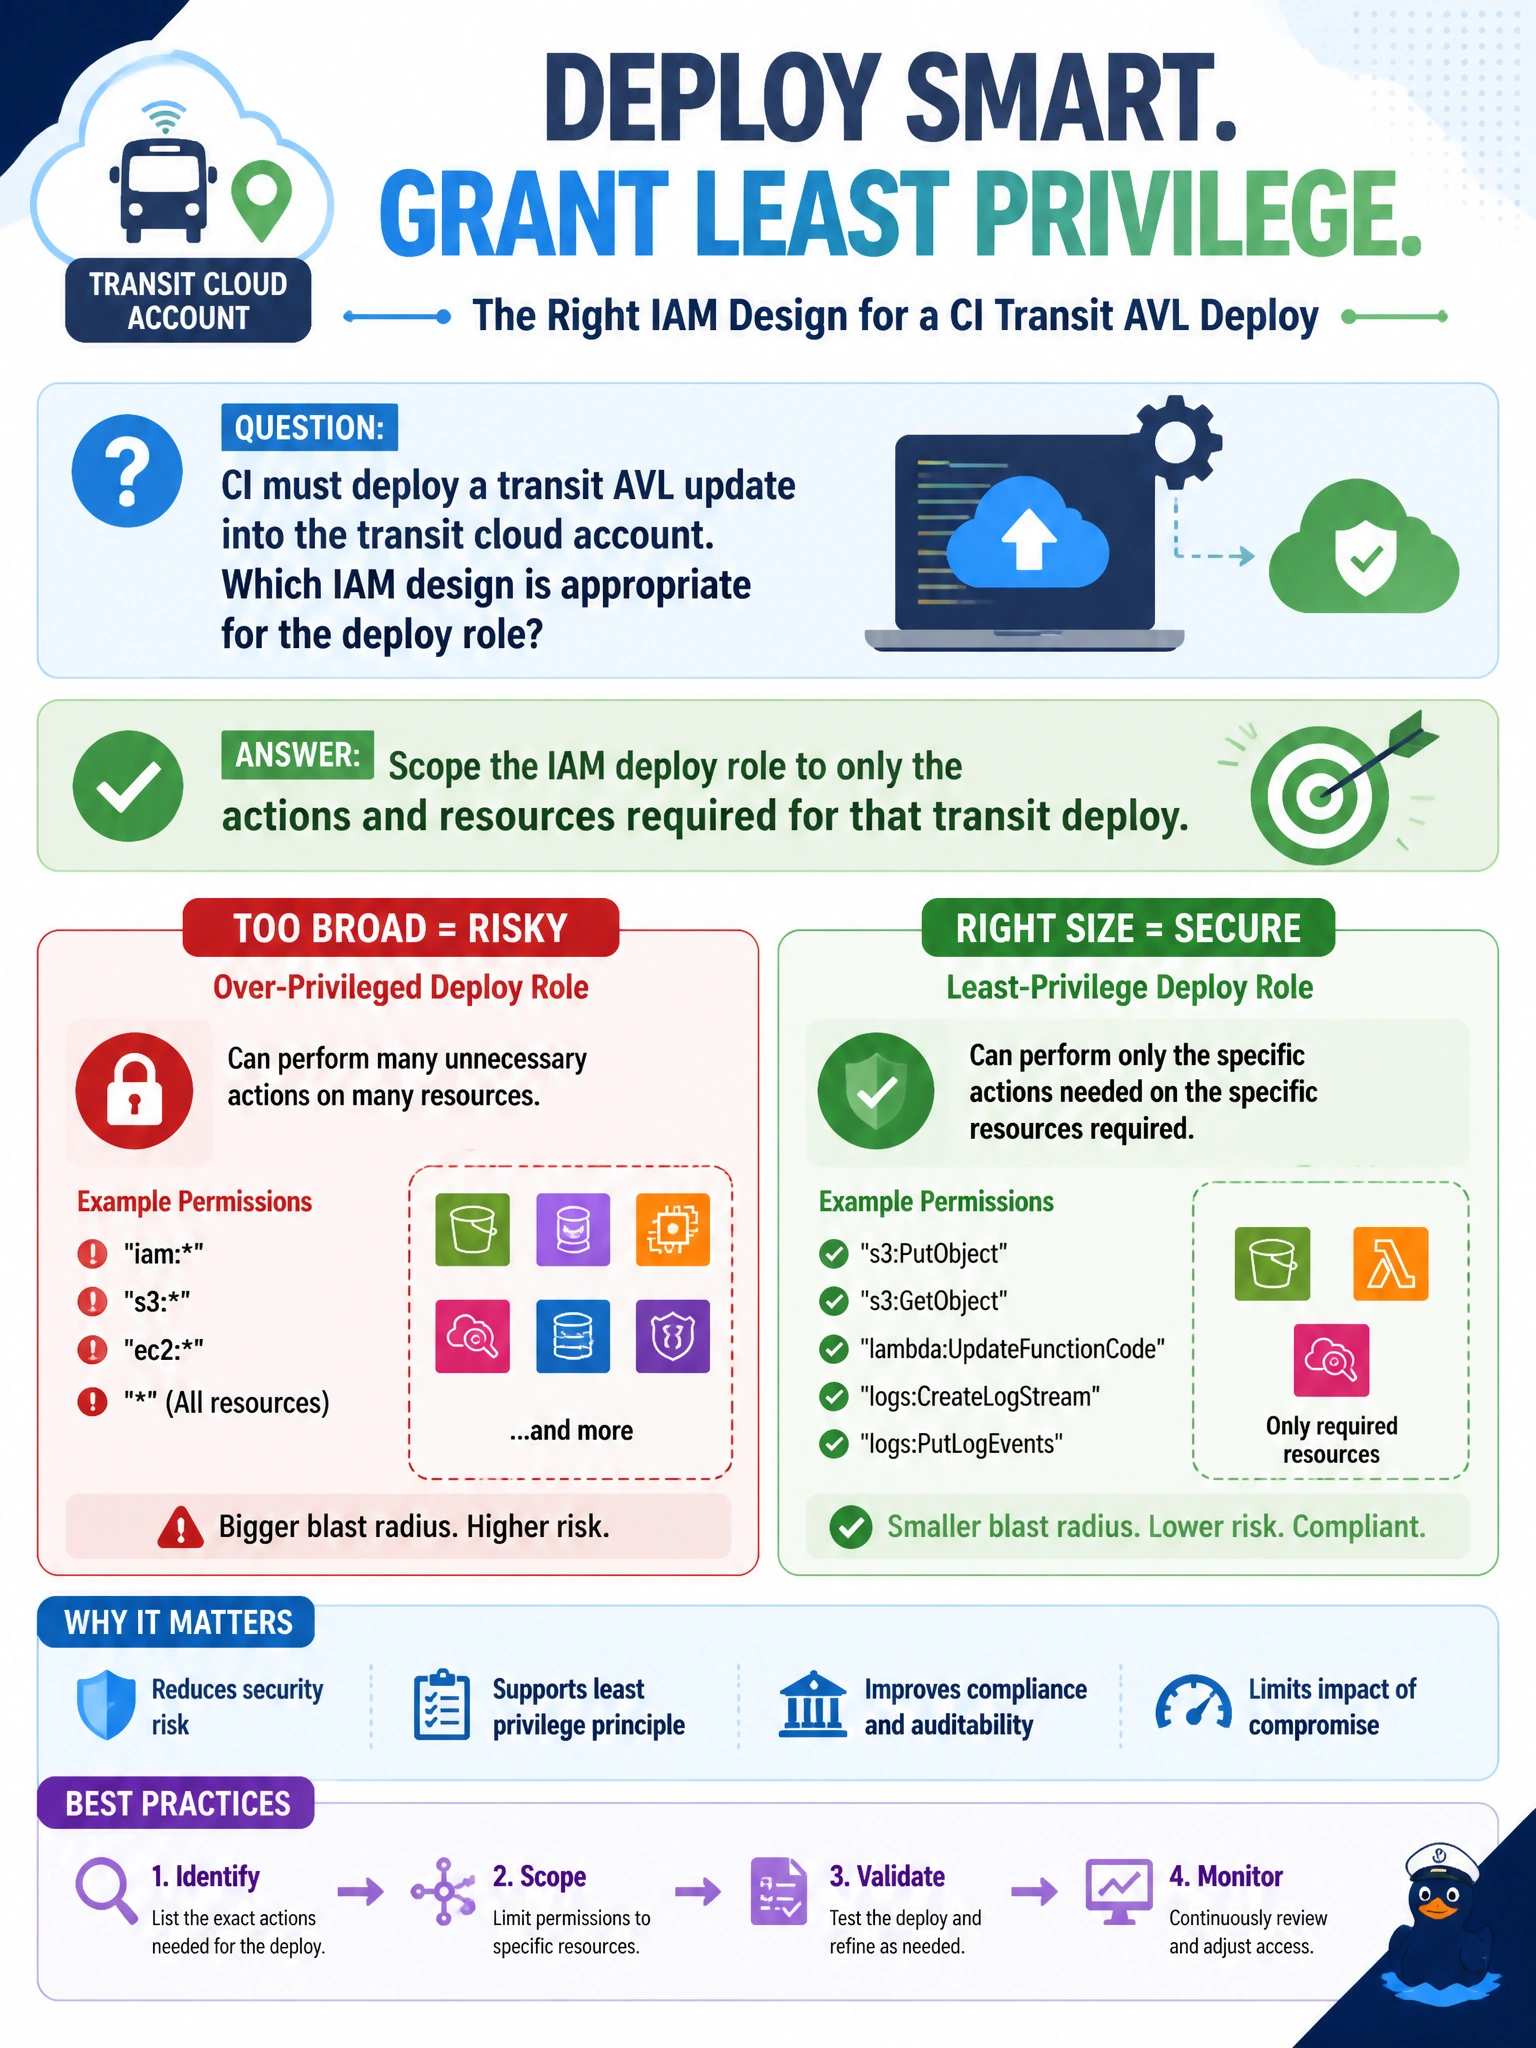
CI must deploy a transit AVL update into the transit cloud account. Which IAM design is appropriate for the deploy role?
Select an answer to reveal the explanation.
Short Explanation
Least privilege for the transit deploy role means only the knobs that release needs—not citywide admin. Shared personal logins and anonymous access are how blast radius becomes the whole cloud.
Full Explanation
Least privilege scopes an IAM deploy role to only the actions and resources required for that deploy, limiting blast radius if the pipeline credential is abused. CI deploying a transit AVL update into the transit cloud account should use a role limited to that transit deploy’s needed actions and resources—not citywide administrator rights that can touch unrelated agencies and data stores.
Granting the role full administrator rights across every city cloud account maximizes damage from a single pipeline compromise or leaked token. Reusing a personal operator login shared among the entire pipeline destroys attribution and usually over-permissions human accounts for automation. Disabling IAM entirely and opening the account with anonymous access removes identity controls altogether and is incompatible with municipal cloud governance.
Exam caveat: separate plan versus apply or build versus deploy roles when possible, and deny IAM privilege-escalation paths in the deploy role policy document. Operational check: review the transit deploy role policy for unused wildcards, run a deploy successfully with the scoped role, and verify a denied action outside scope fails as expected in a controlled test.