
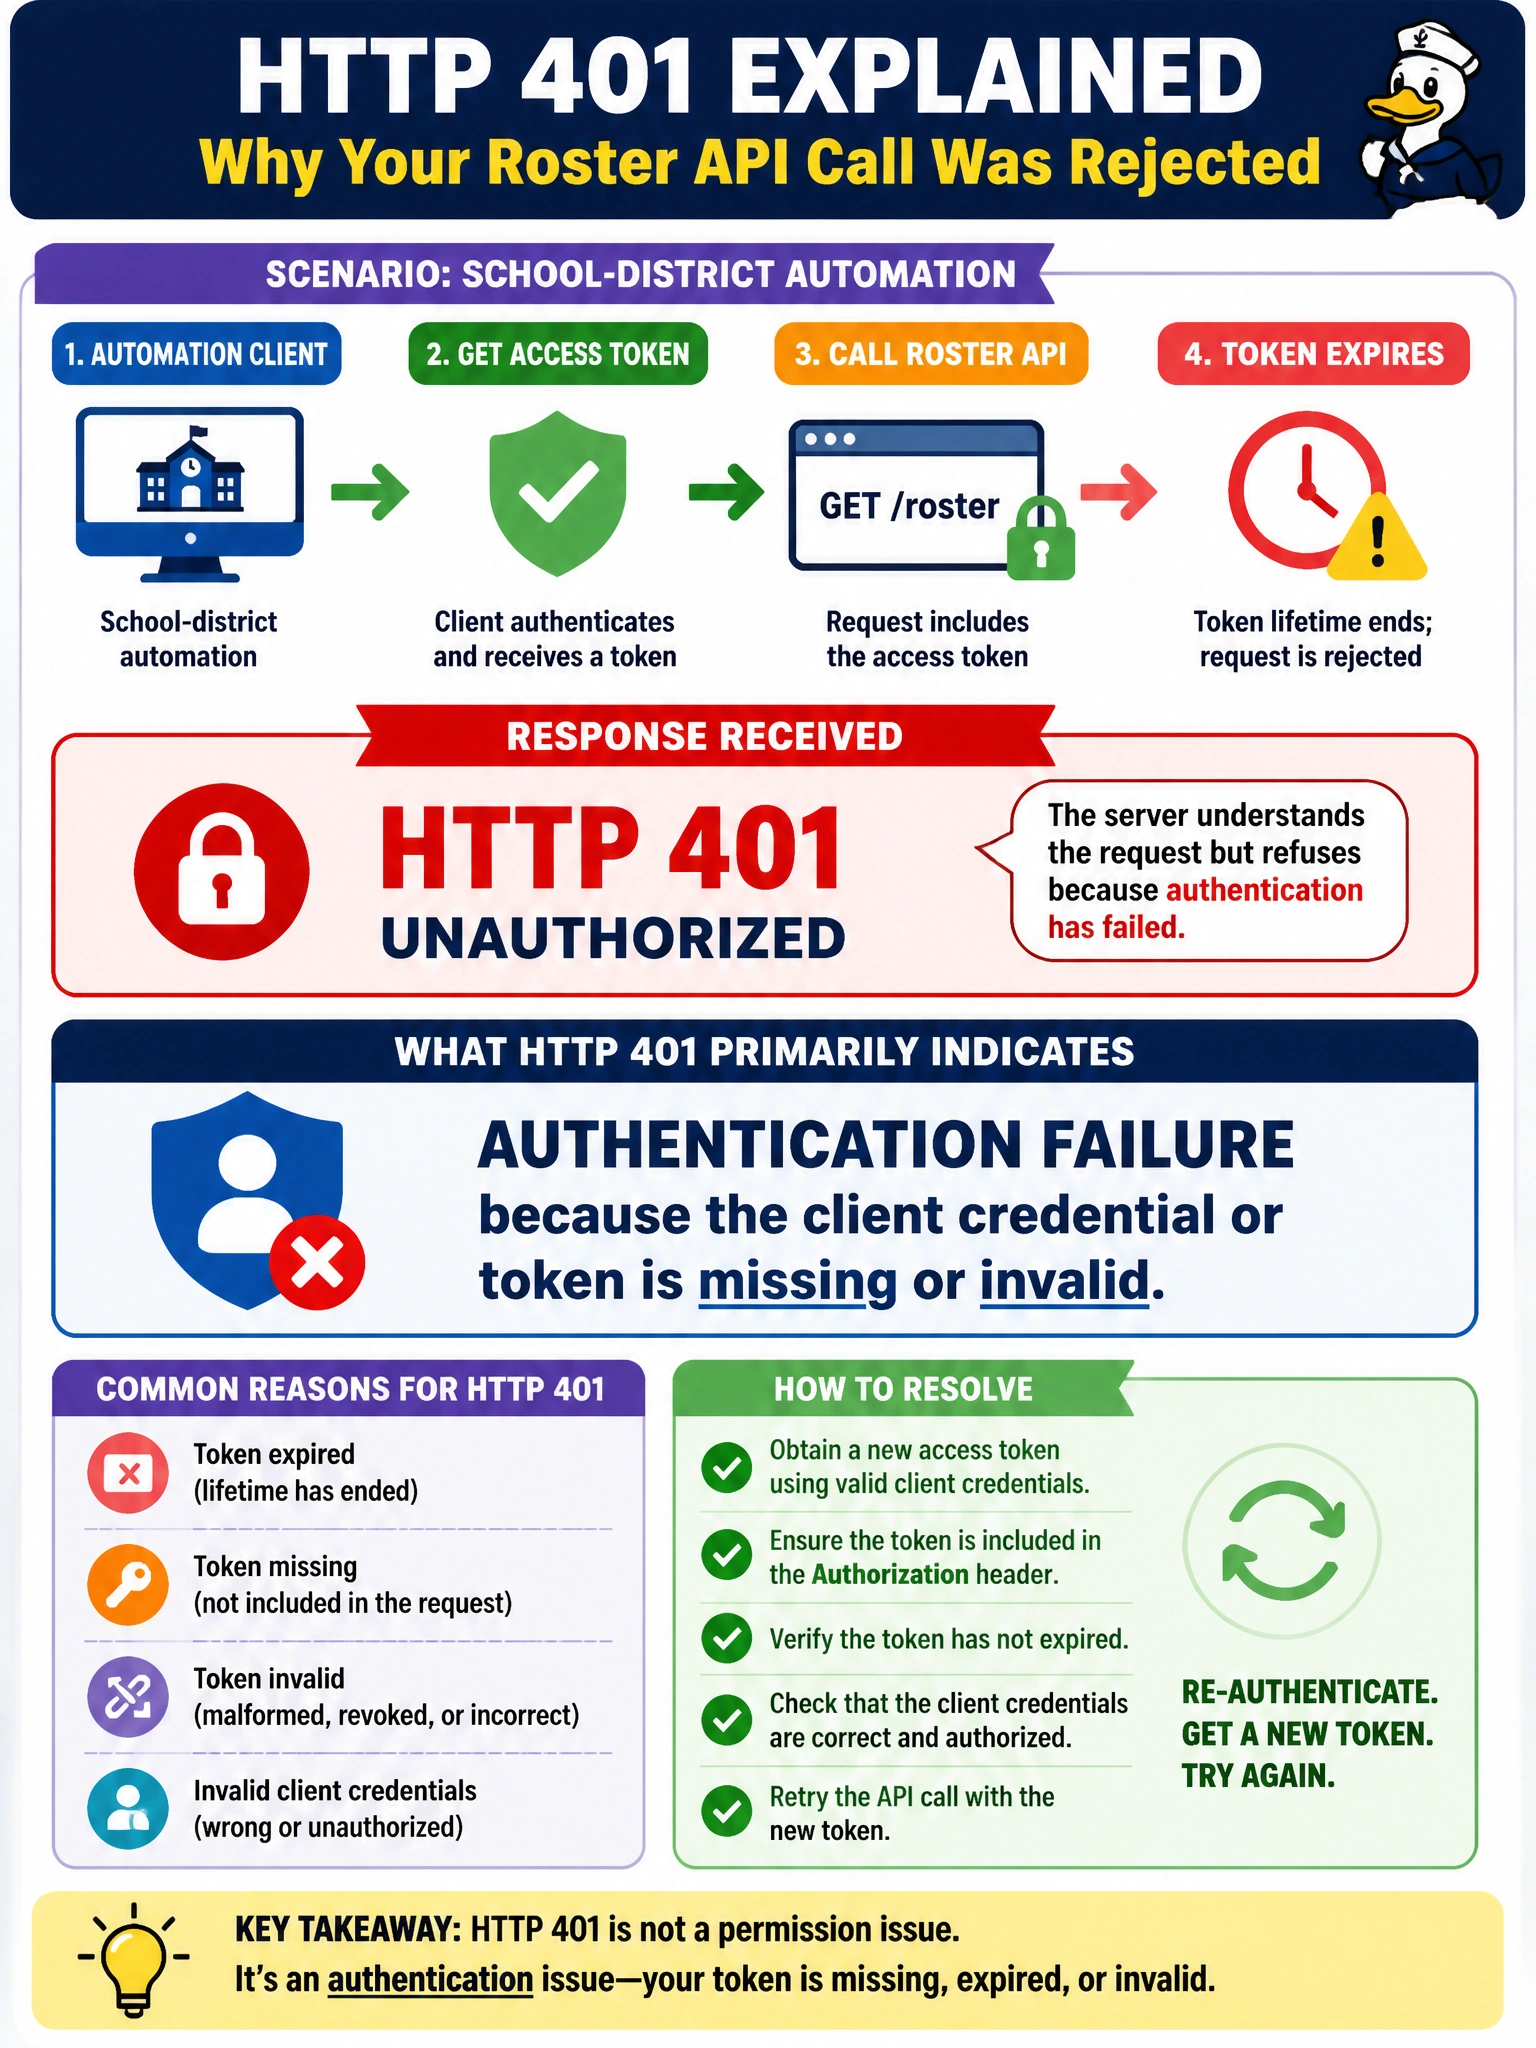
School-district automation receives HTTP 401 when calling the SSO-protected roster API after a token lifetime ends. What does that status primarily indicate?
Select an answer to reveal the explanation.
Short Explanation
401 is the bouncer saying your badge expired—not that the kitchen is on fire. Refresh or reissue the SSO token. Do not confuse it with create-success or server-down codes.
Full Explanation
When school-district automation calls an SSO-protected roster API after a token lifetime ends, HTTP 401 primarily signals authentication failure: the client credential or token is missing, expired, or otherwise invalid. 401 tells the caller that the server did not accept the identity material presented (or none was presented). In district roster integrations, the operational response is to refresh or reissue the SSO/OAuth token and retry with valid Authorization material—not to treat the call as a successful write or as generic server collapse.
Successful creation of a new roster resource fails by concept because create success is communicated with 2xx codes such as 201, not 401. A temporary redirect to a newer API hostname fails because redirects are 3xx responses with Location semantics; 401 is not a redirect signal. Treating 401 as server overload equivalent to 503 fails because 5xx classes describe server-side inability to serve, whereas 401 specifically points at the authentication challenge or failure on the request.
Exam caveat: distinguish 401 Unauthorized (authentication) from 403 Forbidden (authenticated but not allowed). Some platforms blur messaging, but on exams 401 after token expiry maps to invalid/missing credentials. Do not assume every failure after SSO change is 503 capacity loss.
Operational check: inspect whether the Authorization header is present and unexpired, renew the district SSO token through the IdP/token endpoint, confirm clock skew is not invalidating JWTs early, retry the roster call, and alert if 401 rates spike across many clients—which often indicates coordinated token or IdP misconfiguration rather than a single bad password.