
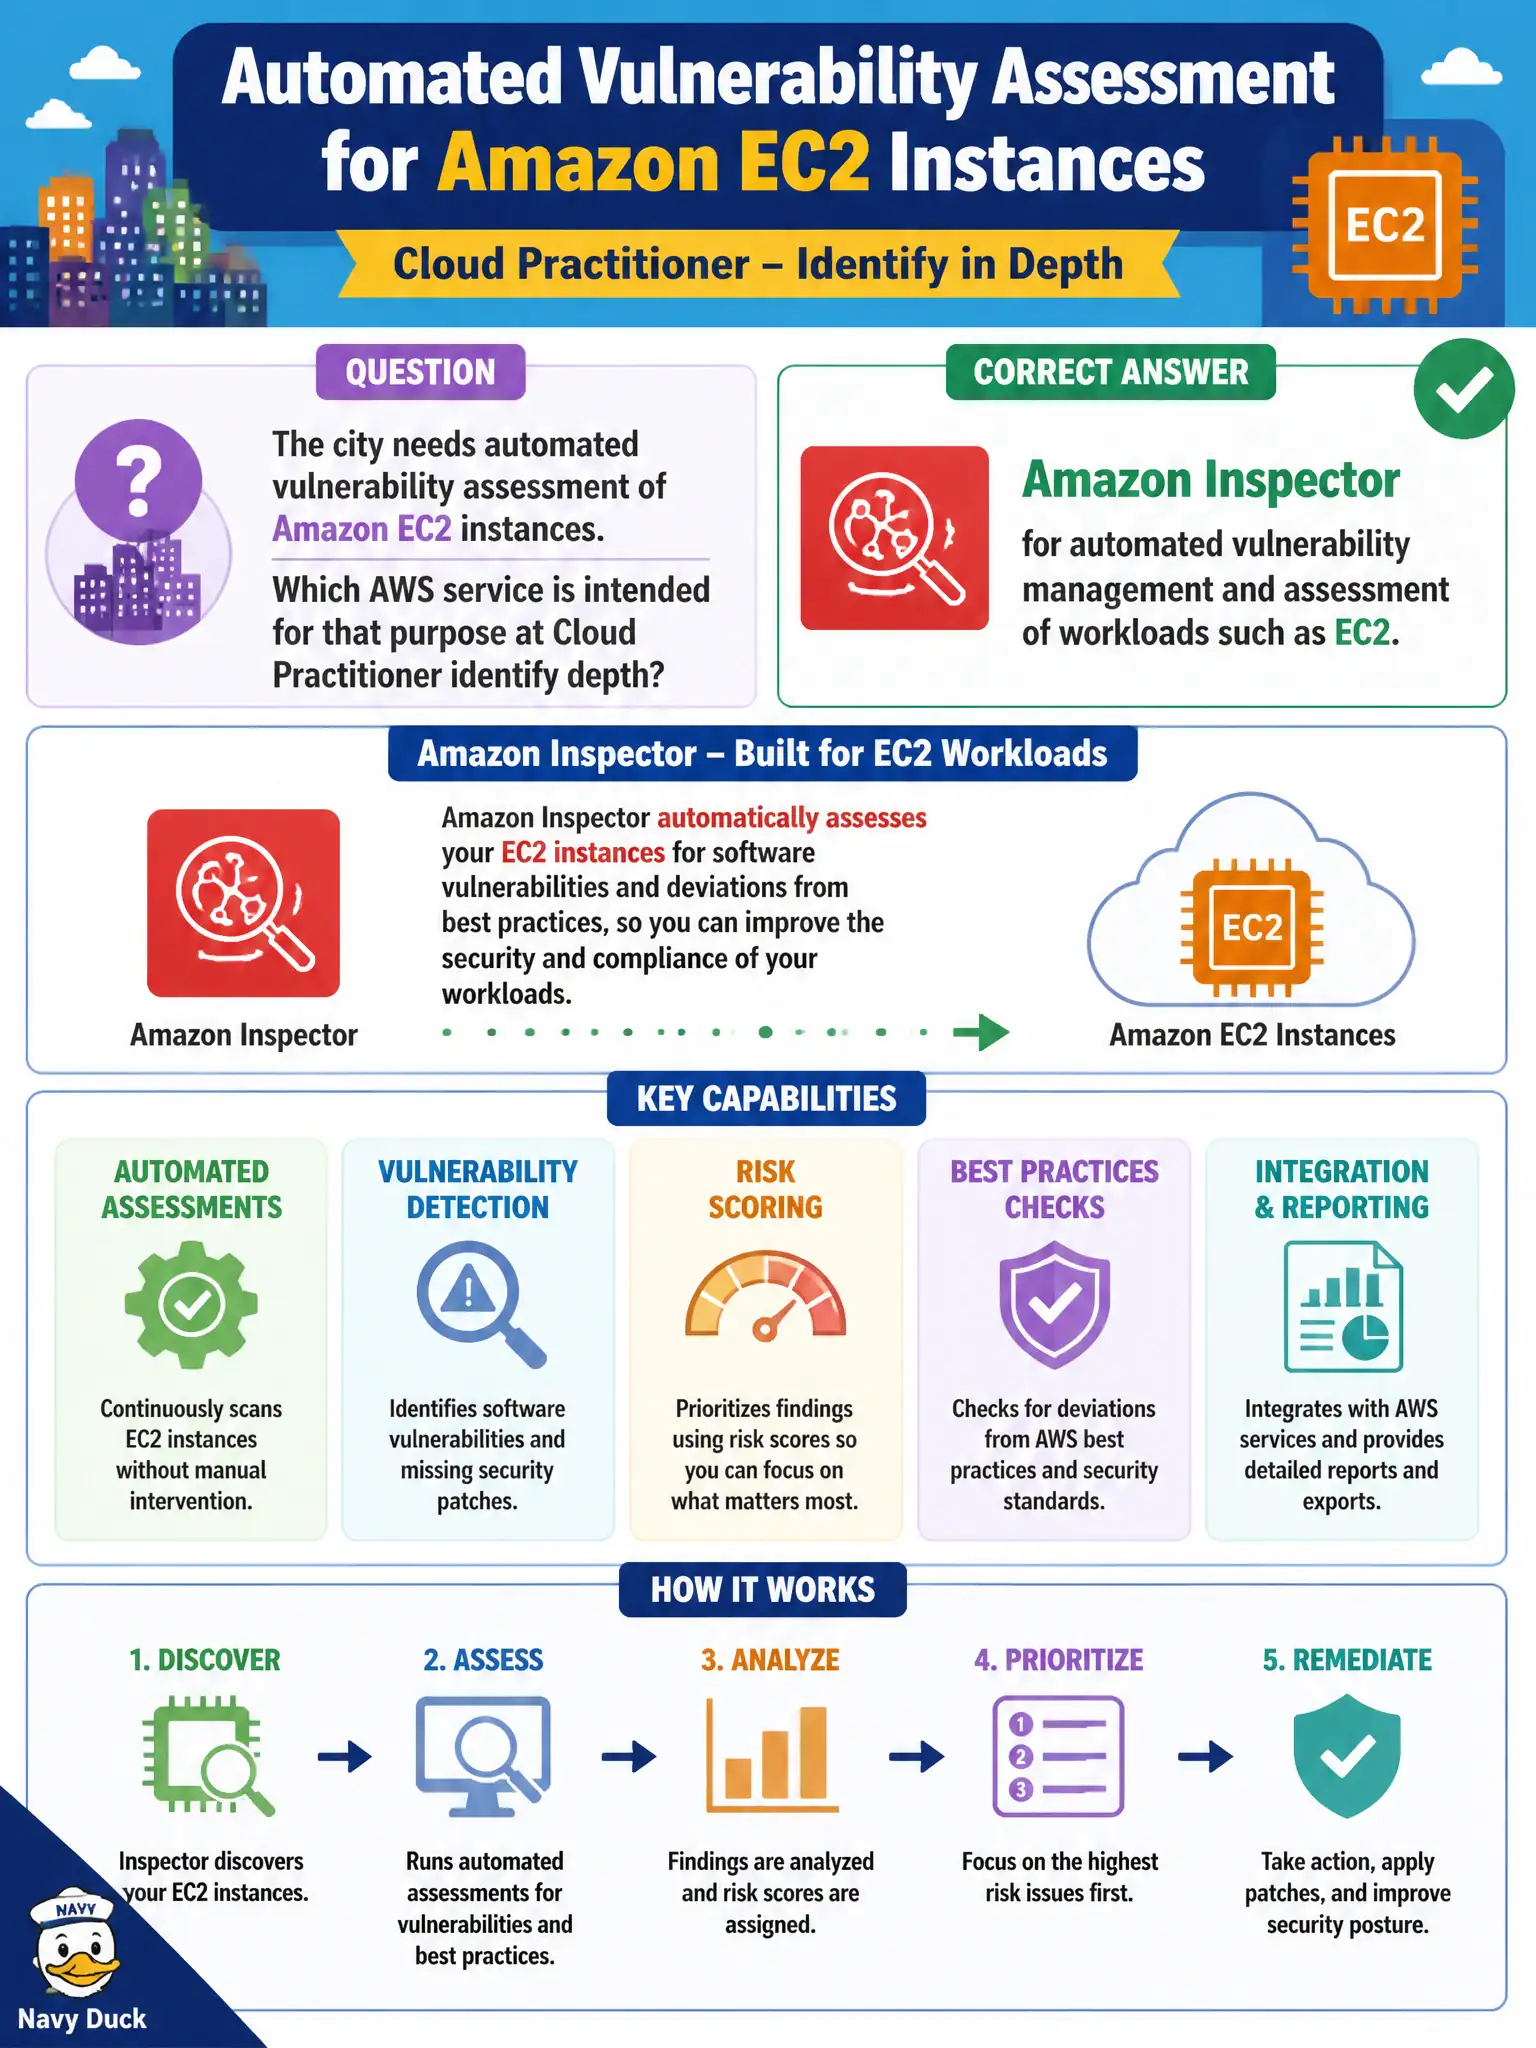
The city needs automated vulnerability assessment of Amazon EC2 instances. Which AWS service is intended for that purpose at Cloud Practitioner identify depth?
Select an answer to reveal the explanation.
Short Explanation
Think of Inspector as the scheduled safety inspection for your instances — looking for known weaknesses — not the paperwork library or the CDN. When the ask is vulnerability assessment on EC2, Amazon Inspector is the match. Artifact, CloudFront, and Route 53 play other roles.
Full Explanation
Amazon Inspector provides automated vulnerability management and assessment for workloads such as Amazon EC2, helping identify known weaknesses in a scheduled safety-inspection style for city fleets that host permitting, GIS, or utility APIs. When the municipal ask is vulnerability assessment on instances, Inspector is the service match rather than a paperwork portal or a network edge service. AWS Artifact is the compliance report portal, not a real-time guest OS CVE scanner. Amazon CloudFront is a content delivery network, not a host vulnerability scoring engine inside private subnets. Amazon Route 53 is DNS, not continuous package vulnerability detection on instances. Distractors fail by confusing paperwork, CDN, and DNS services with vulnerability assessment. Exam caveat: Inspector findings complement but do not replace patch management ownership on customer-managed guests and application packages under shared responsibility. Operational check: enable Inspector where appropriate for EC2 and supported workload types, integrate findings into patch SLAs for city fleets, prioritize critical CVEs on internet-exposed systems first, track exceptions with documented risk acceptance, and confirm assessment coverage after new accounts or Regions are brought online for municipal services.