
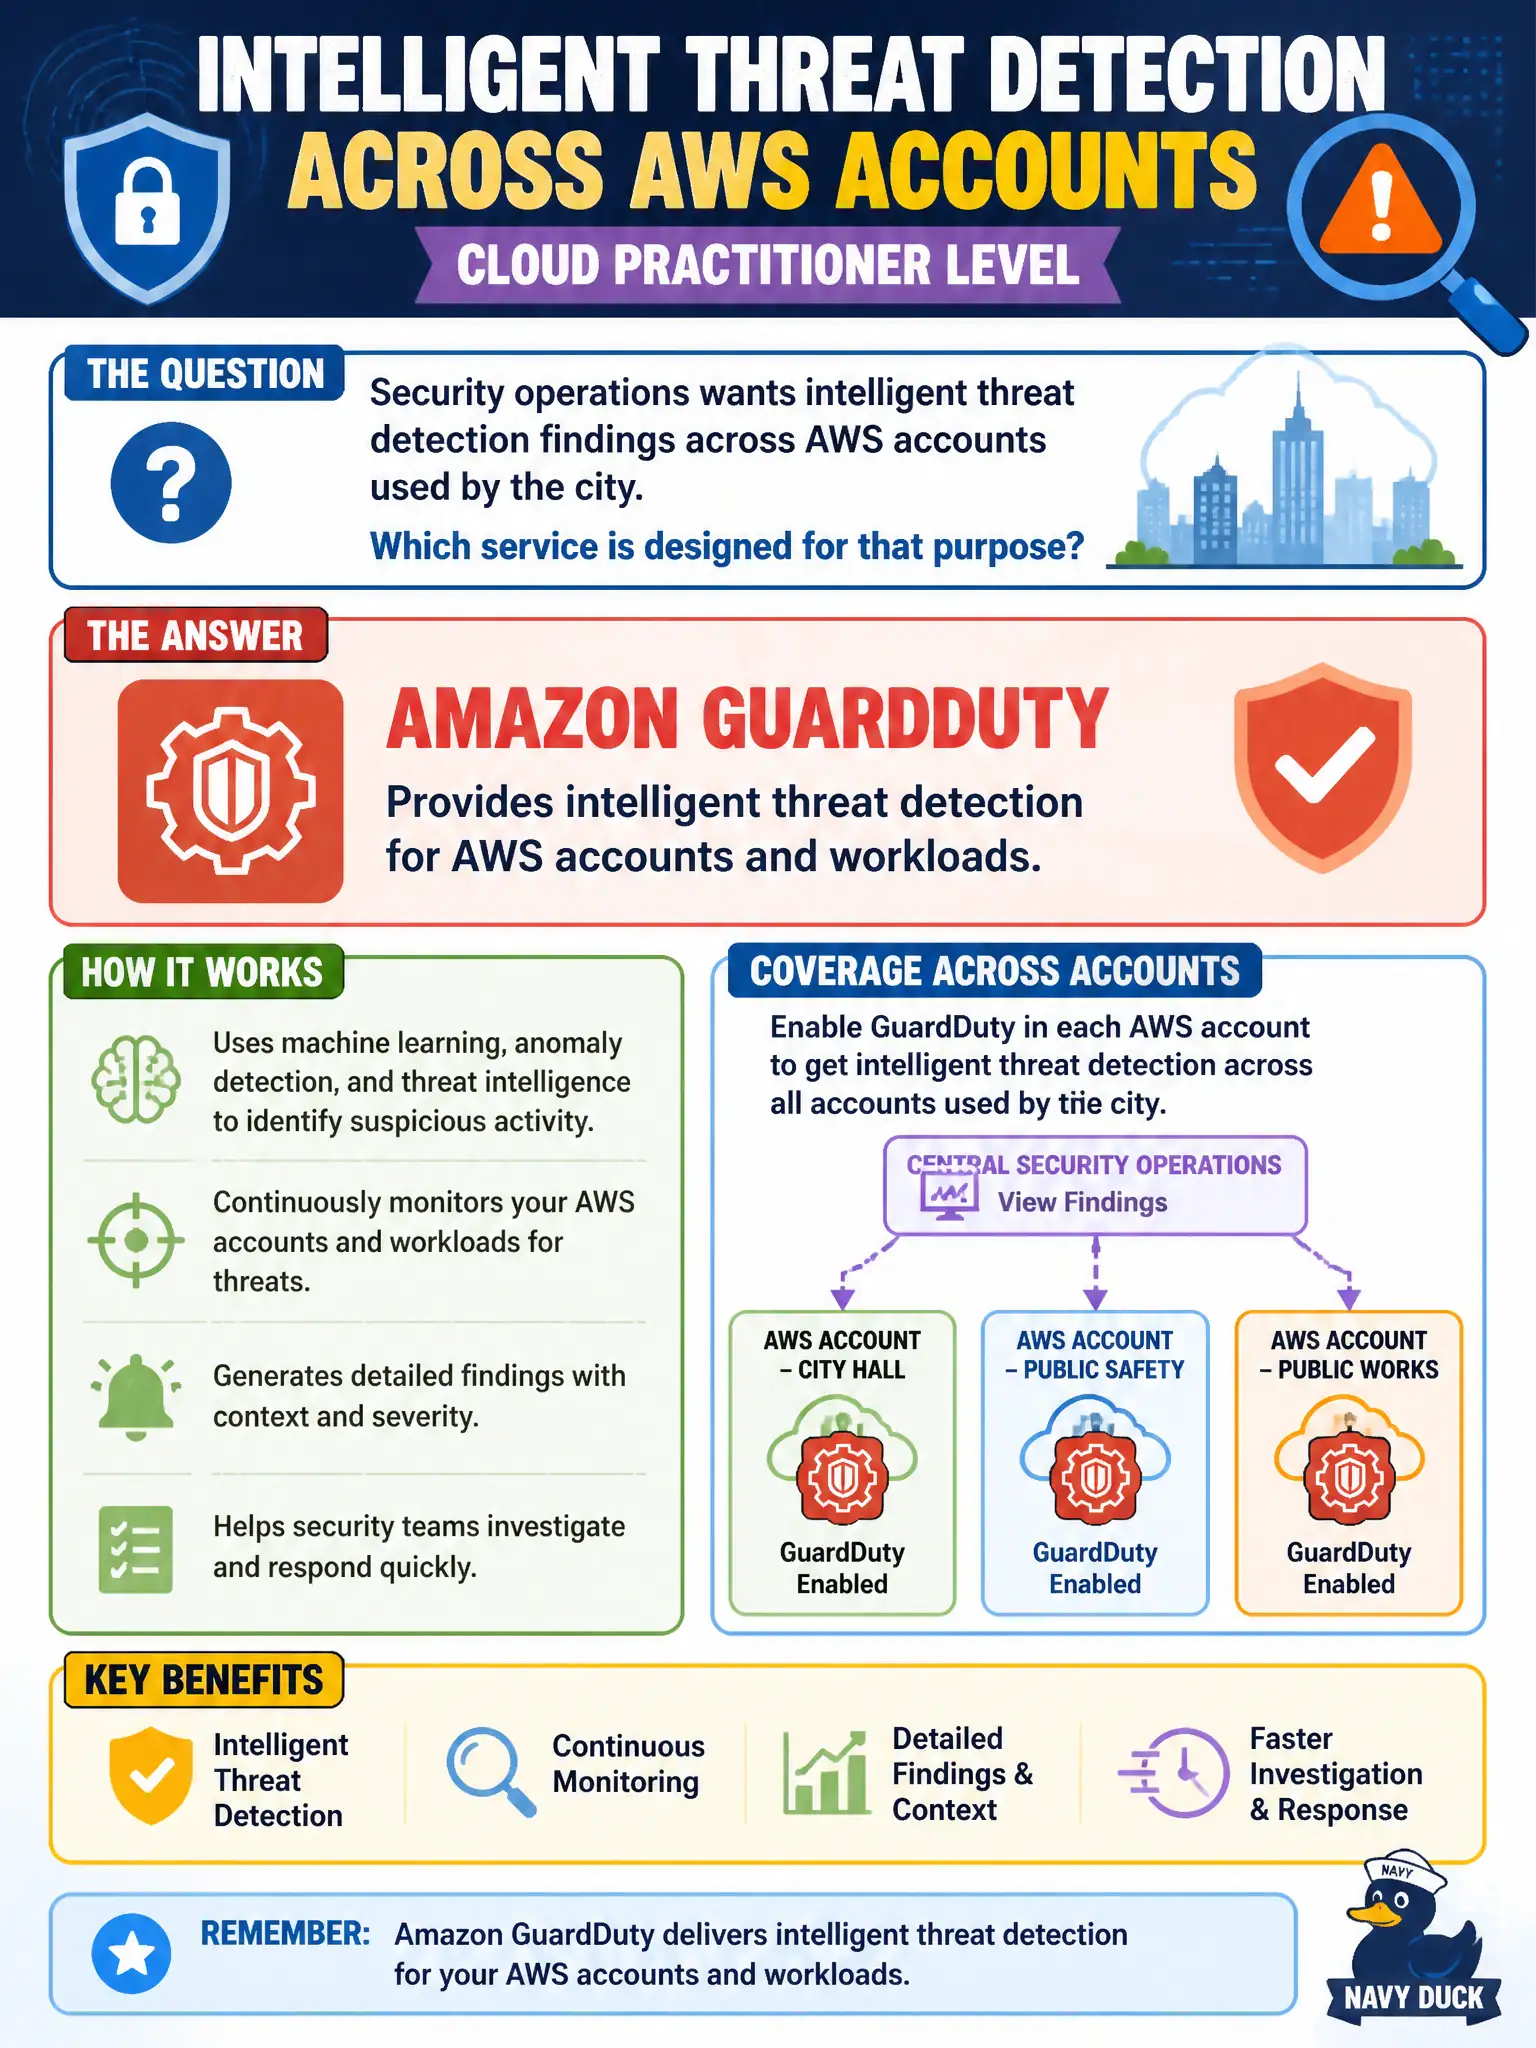
Security operations wants intelligent threat detection findings across AWS accounts used by the city. Which service is designed for that purpose at Cloud Practitioner depth?
Select an answer to reveal the explanation.
Short Explanation
When you want a security guard that watches for weird account and network behavior, pick GuardDuty — not a compliance PDF shelf or a migration suitcase. GuardDuty is the threat detection service. Artifact, S3 versioning, and Snowball are answering different questions.
Full Explanation
Amazon GuardDuty provides intelligent threat detection for AWS accounts and workloads, watching for suspicious API activity, potentially unauthorized behavior, and related findings that municipal security teams should investigate. That matches the metaphor of a guard watching for weird account and network behavior better than compliance libraries or migration devices. AWS Artifact is for compliance reports and agreements, not continuous malware signature updates on EC2 in the GuardDuty sense. Amazon S3 versioning does not generate network intrusion findings by itself. AWS Snowball is a data transfer appliance family, not a streaming threat-detection pipeline to tape. Distractors fail by mixing compliance paperwork, storage features, and offline transfer hardware with threat detection. Exam caveat: GuardDuty findings still require customer response playbooks — detection without triage and remediation ownership is incomplete under shared responsibility. Operational check: enable GuardDuty in municipal accounts and delegated admin patterns if used, route findings to Security Hub or ticketing, define severity-based response SLAs, suppress only with justification, and periodically verify detectors cover the Regions where civic workloads run.