
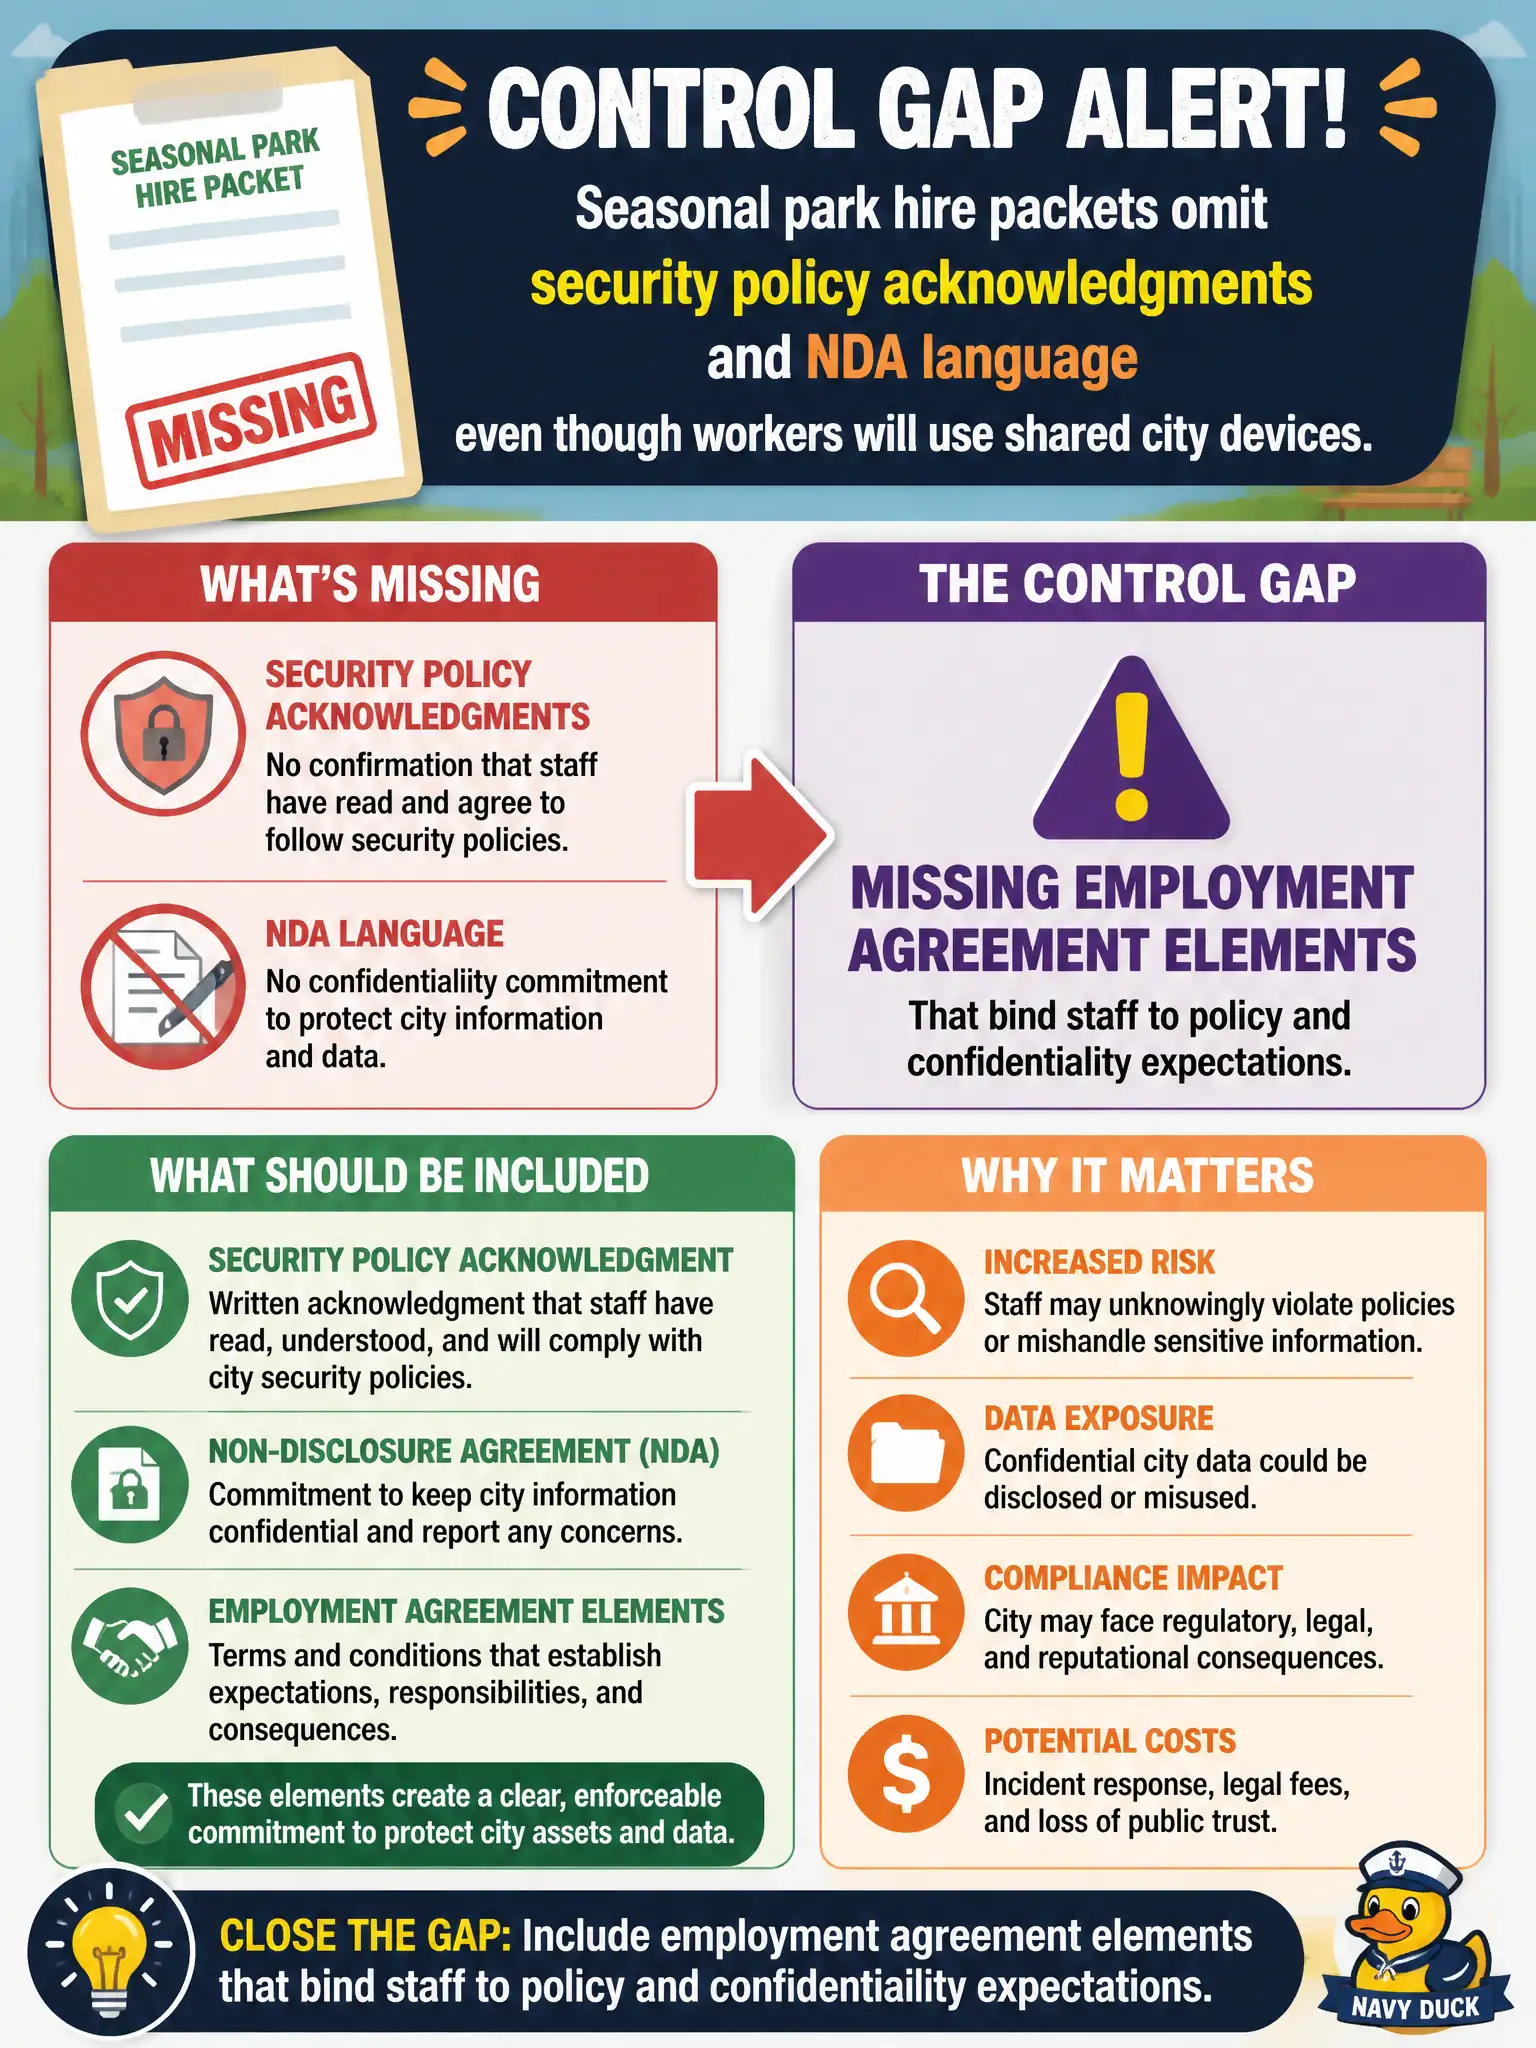
Seasonal park hire packets omit security policy acknowledgments and NDA language even though workers will use shared city devices. What control gap should be flagged?
Select an answer to reveal the explanation.
Short Explanation
If the packet never says 'here's the rules and keep city data quiet,' seasonal hires never formally signed on. Policy acknowledgments and NDAs are the handshake that makes expectations enforceable. Shared devices without that paperwork is a personnel-security miss.
Full Explanation
Employment and onboarding agreements should bind workers—including seasonal hires—to acceptable-use, security policy, and confidentiality expectations before they receive shared city devices. Omitting policy acknowledgments and NDA or confidentiality language leaves a control gap: staff may access systems and data without a clear, enforceable commitment to municipal rules. Hardware warranty stickers and public hiring announcements do not create accountability for handling city information on shared endpoints. Mandating biometric enrollment for every groundskeeper may be disproportionate and misses the core gap when agreement elements are absent; authentication strength is separate from contractual and policy binding. Seasonal parks staff often rotate quickly and share devices, which increases the need for explicit acknowledgments rather than informal verbal briefings. Exam caveat: CISSP personnel security covers employment agreements and onboarding controls that establish obligations; role duration does not remove the need for policy acceptance when access is granted. Operational check: include security policy acknowledgment and confidentiality clauses in seasonal hire packets, record signatures or electronic acceptance before account issuance, and cover shared-device rules, data handling, and return of credentials at end of season. Spot-check that device provisioning workflows block access until required acknowledgments are on file.