
The internet access policy must block destinations associated with malware, phishing and command-and-control while permitting business-category sites, and it must keep working as new malicious domains appear every day. How should the rules be built?
Select an answer to reveal the explanation.
Short Explanation
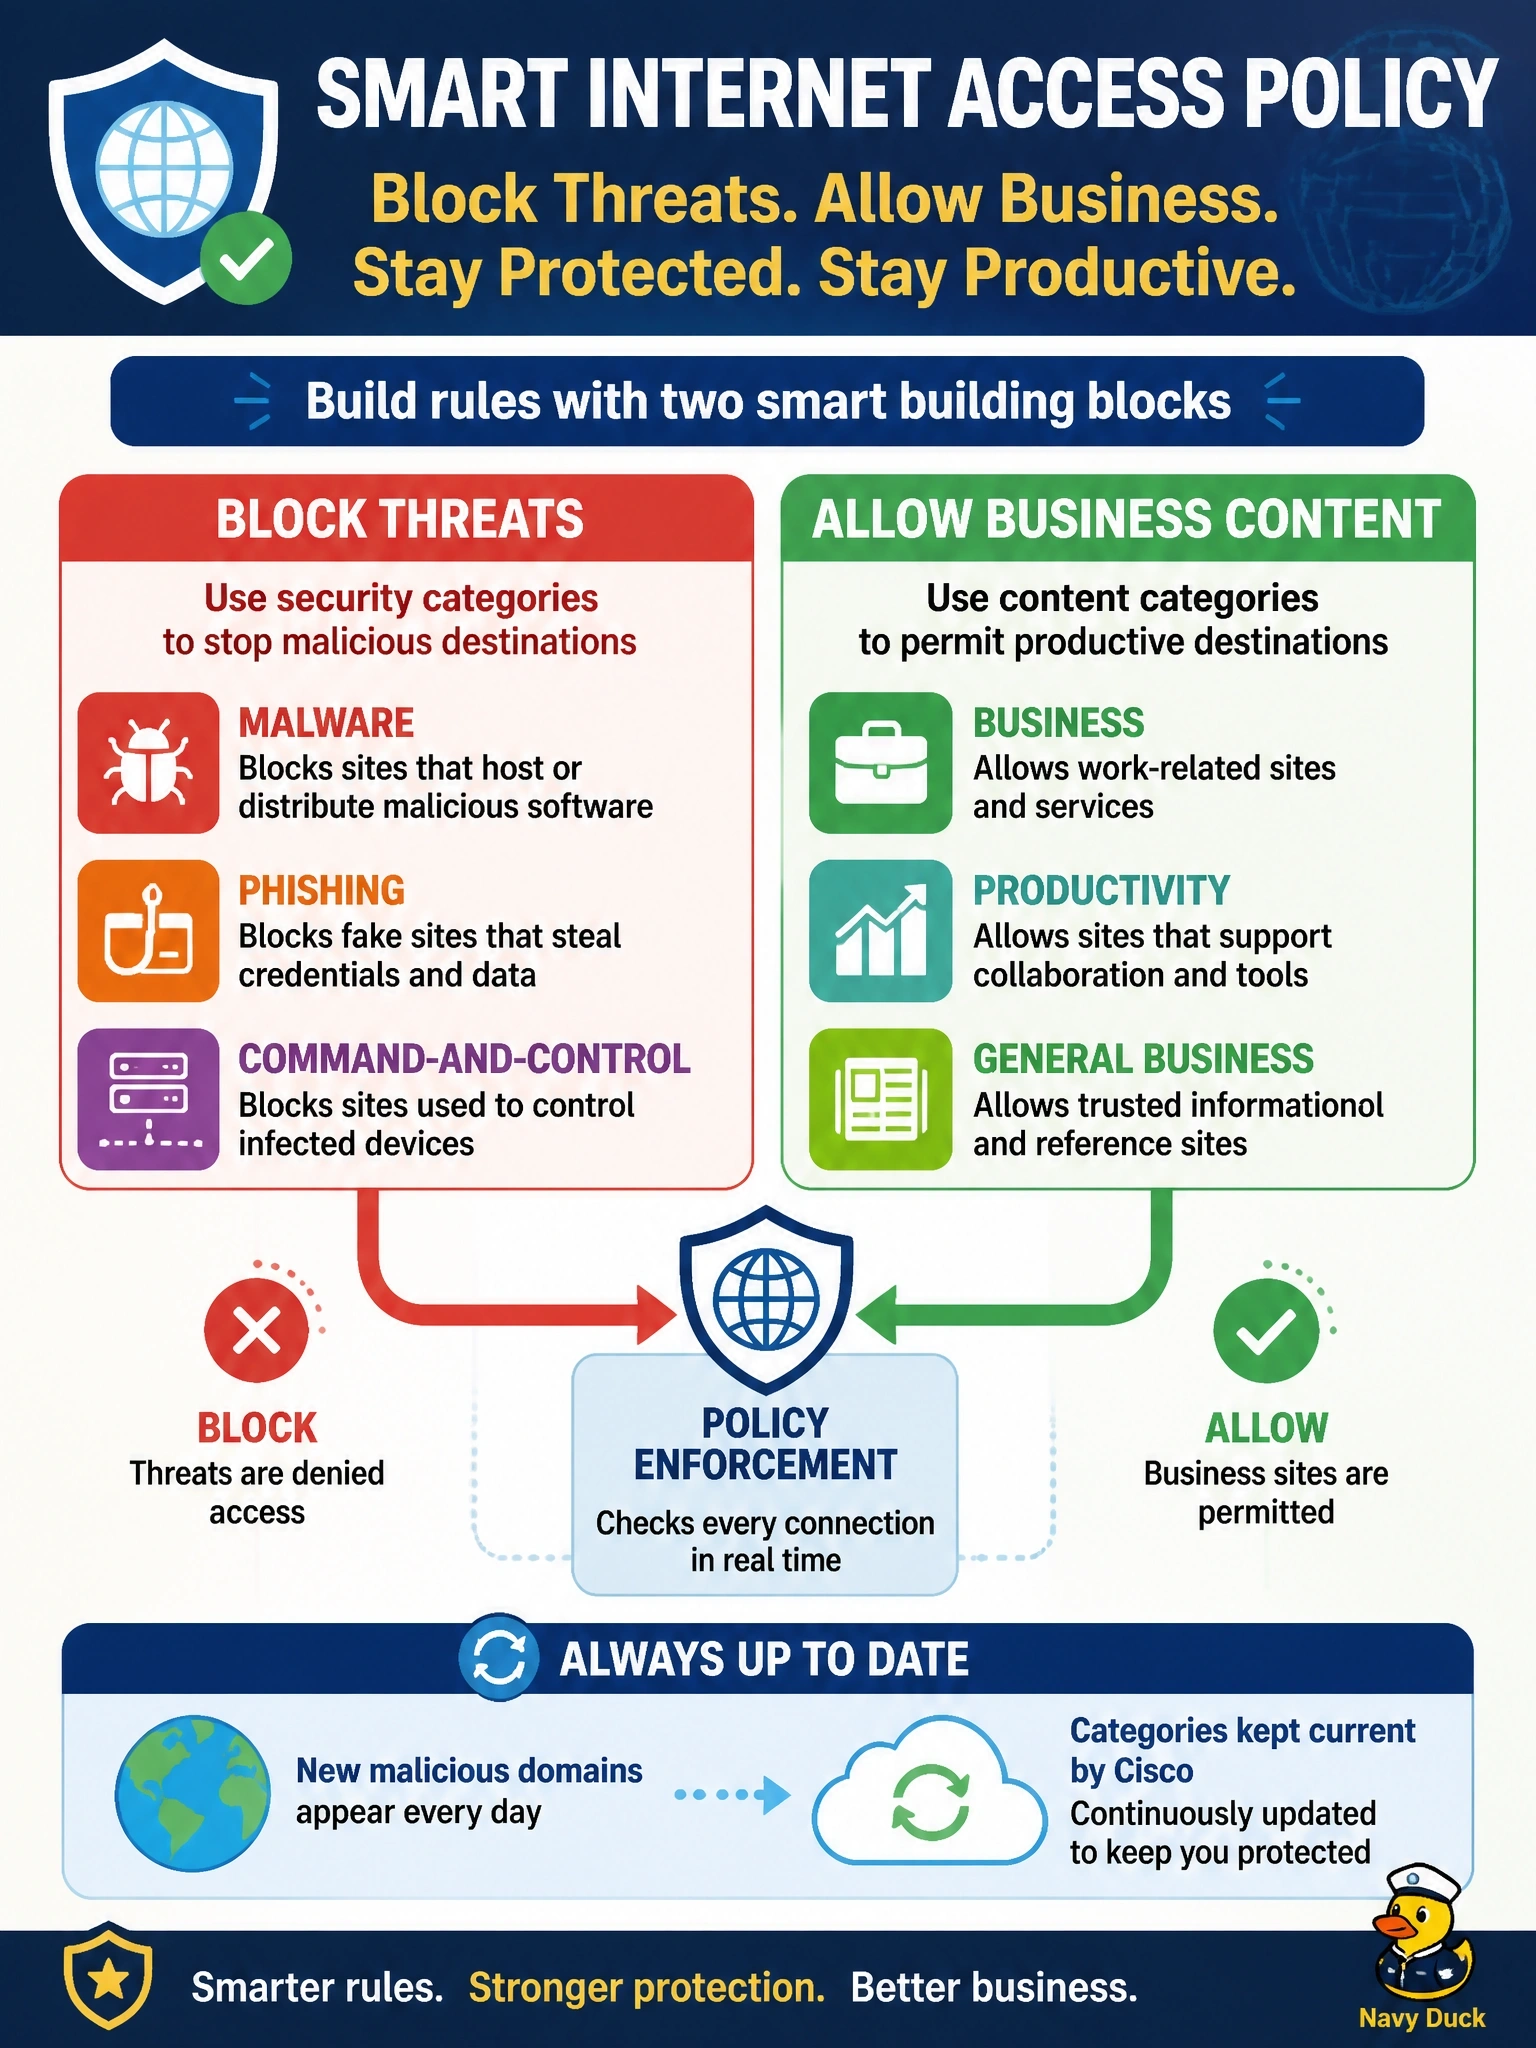
Why write your own phone book of crooks when Cisco's intelligence updates one for you every minute? Security categories cover malware, phishing and C2, and content categories handle business sites. The trap is the manual list — it's out of date the moment you save it.
Full Explanation
Cisco Secure Access internet access rules can match destinations by category. Security categories, backed by Cisco Talos threat intelligence and Secure Access's own analysis, classify domains and URLs associated with malware, phishing, command-and-control callbacks and similar threats, and Cisco updates them continuously as new malicious infrastructure is discovered. Content categories classify sites by subject, such as business and economy or software and technology, so policy can permit or restrict types of content. Building rules on these categories gives the policy daily freshness without manual work. A manual destination list of malicious URLs updated each morning is perpetually behind, labor-intensive and blind to domains that appear during the day, which is precisely what attackers rely on. Allowing everything and relying on endpoint antivirus abandons preventive network controls and leaves phishing pages and credential theft largely unaddressed. Blocking by IP address in a router ACL is brittle because malicious domains move between shared addresses and content delivery networks, and an ACL cannot interpret domains or categories. Exam caveat: category rules still need ordering and exceptions; a business partner site that is miscategorized is handled with a destination list rule placed above the category rule. Operational check: test a known security-category test domain and confirm the block, then confirm a business site is allowed.