
A script runs r = requests.post(fmc + '/api/fmc_platform/v1/auth/generatetoken', auth=(user, pw)), then tok = r.headers['X-auth-access-token'] and h = {'X-auth-access-token': tok}. Every later call is requests.get(url, headers=h). How does the script use the credentials and the token?
Select an answer to reveal the explanation.
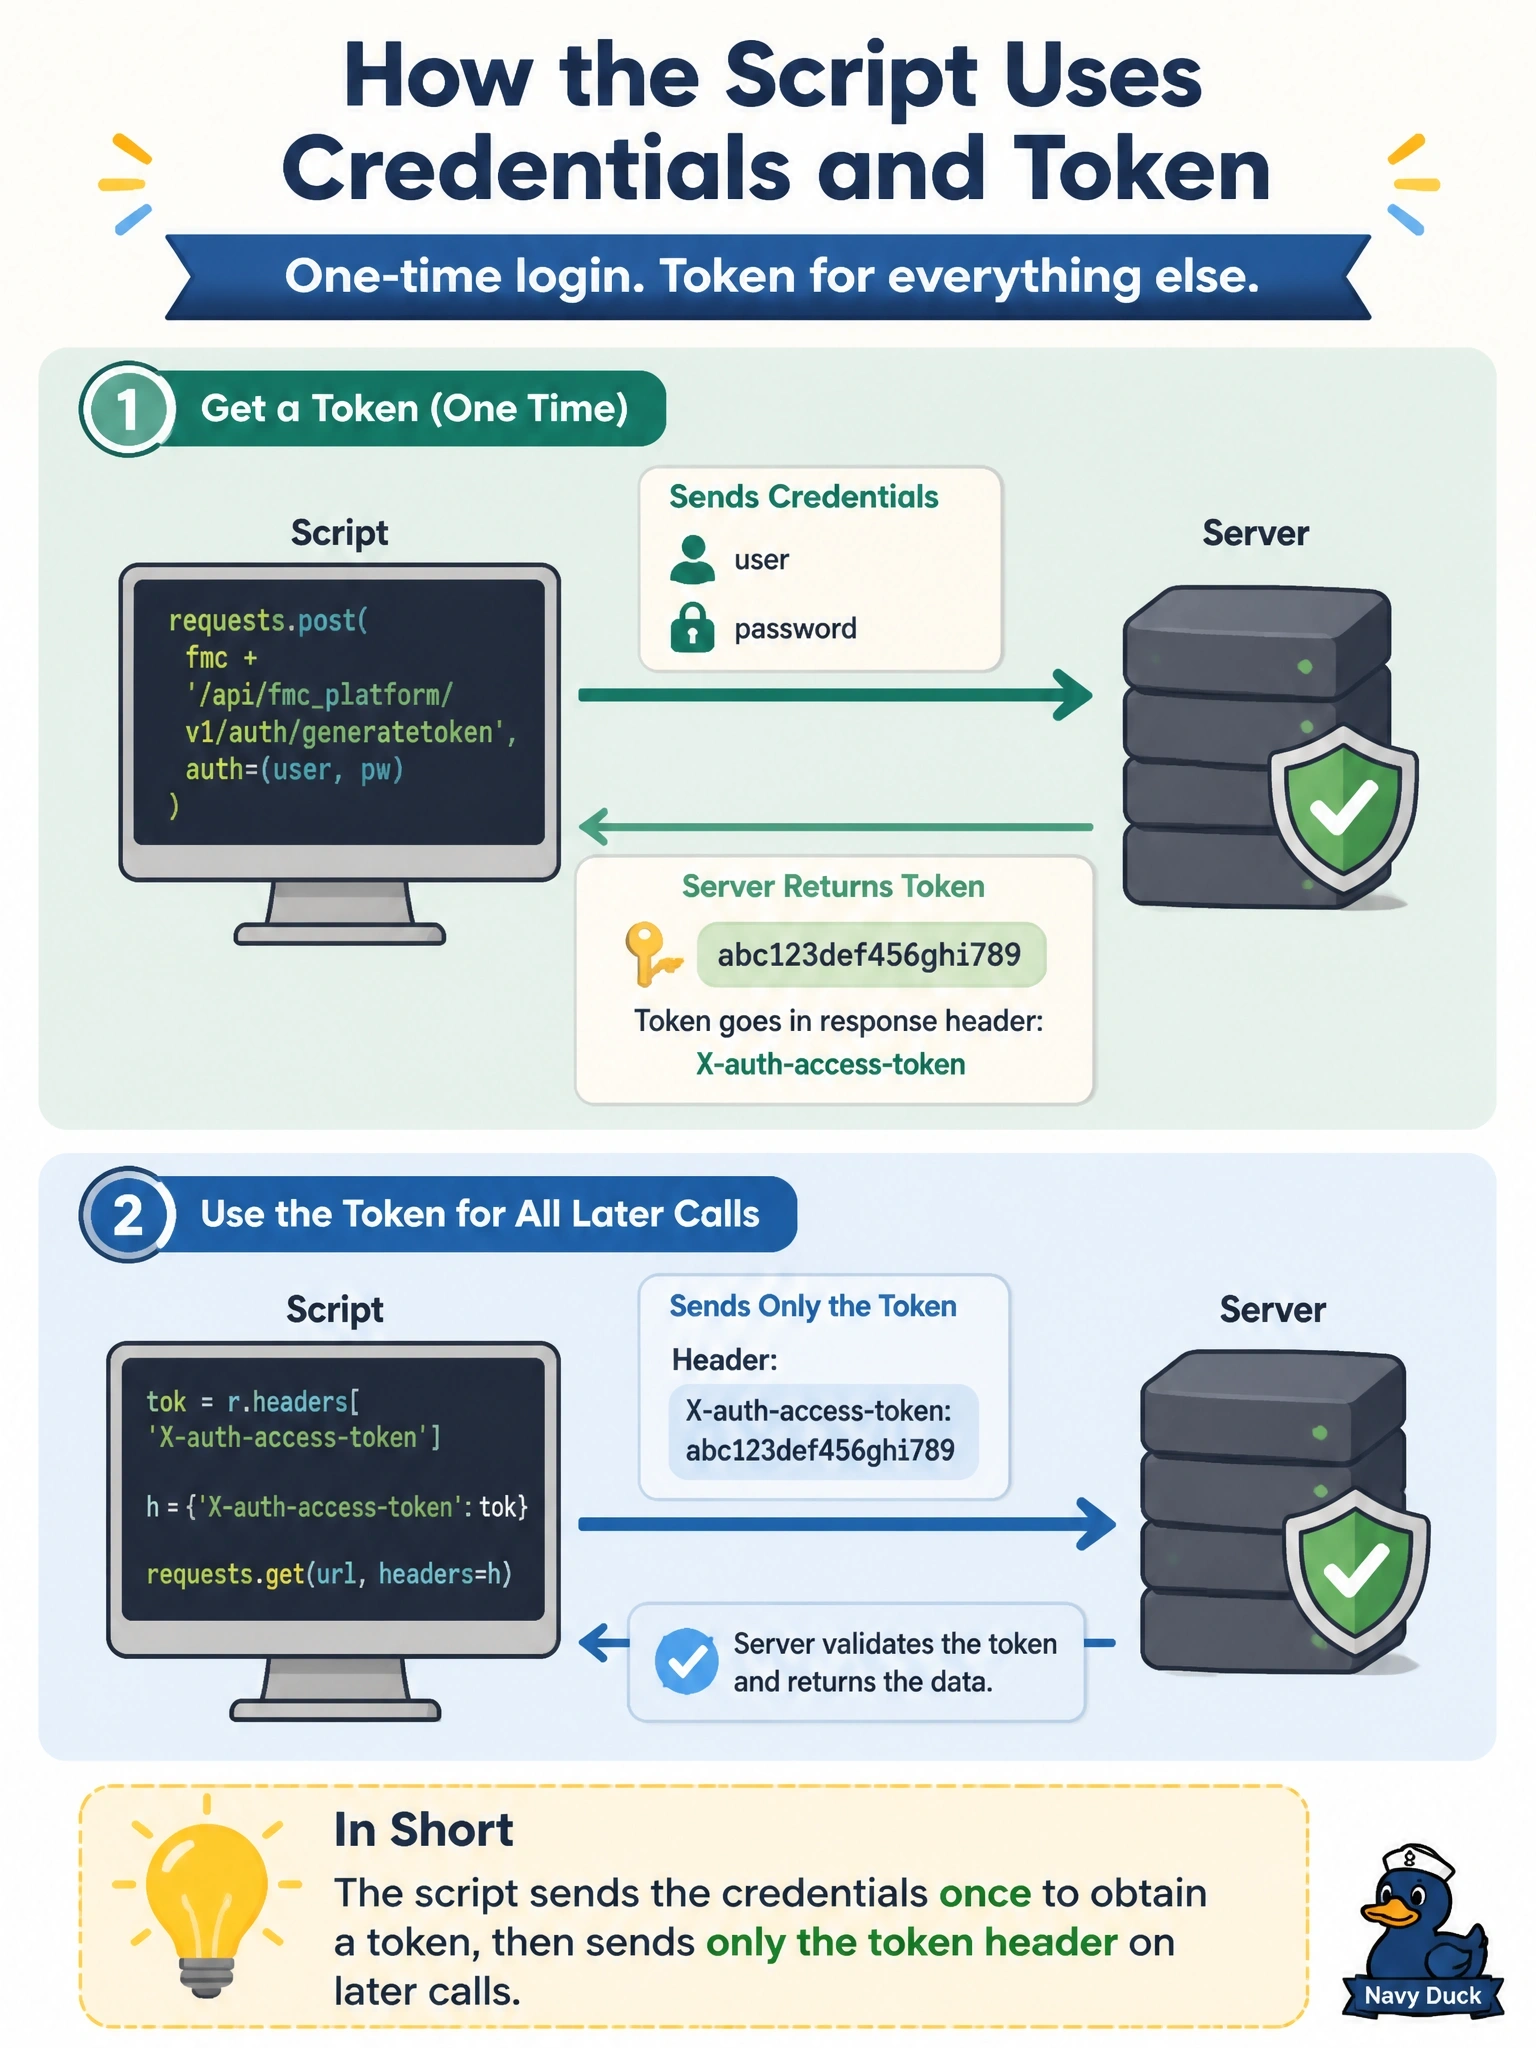
Short Explanation
It's like checking in at a hotel: you show your ID once at the desk, get a key card, and then just tap the card at your door. The script authenticates with basic auth once, pulls the token out of the response headers, and reuses it. Don't get tricked into thinking the password rides along on every call.
Full Explanation
Token-based API authentication separates the login from the work. The Secure Firewall Management Center REST API is a common example: a client sends a POST to the token-generation endpoint with HTTP basic authentication, and the manager returns an access token in a response header named X-auth-access-token. The script stores that value in a dictionary and passes it as a request header on each subsequent call, so the username and password are transmitted only once. Reading the code line by line confirms this: the auth tuple appears only in the POST, and every GET passes headers=h. The idea that credentials are resent on every call ignores that only the first request includes the auth argument. Nothing in the code encrypts the password; the token is issued by the server, not derived from the password by the client. The token is read from r.headers, not from r.json(), and it is placed in a header, not in the URL; tokens in query strings are also a poor practice because URLs are logged. Exam caveat: interpretation questions reward tracing each variable from where it is set to where it is used. Operational check: print the status code of the token request and confirm the header is present before using it, and handle token expiry by requesting or refreshing a token when a call returns 401.