
A new MDS joins a factory IoT network fabric and is given a Fibre Channel domain ID. Which switch granted that domain ID?
Select an answer to reveal the explanation.
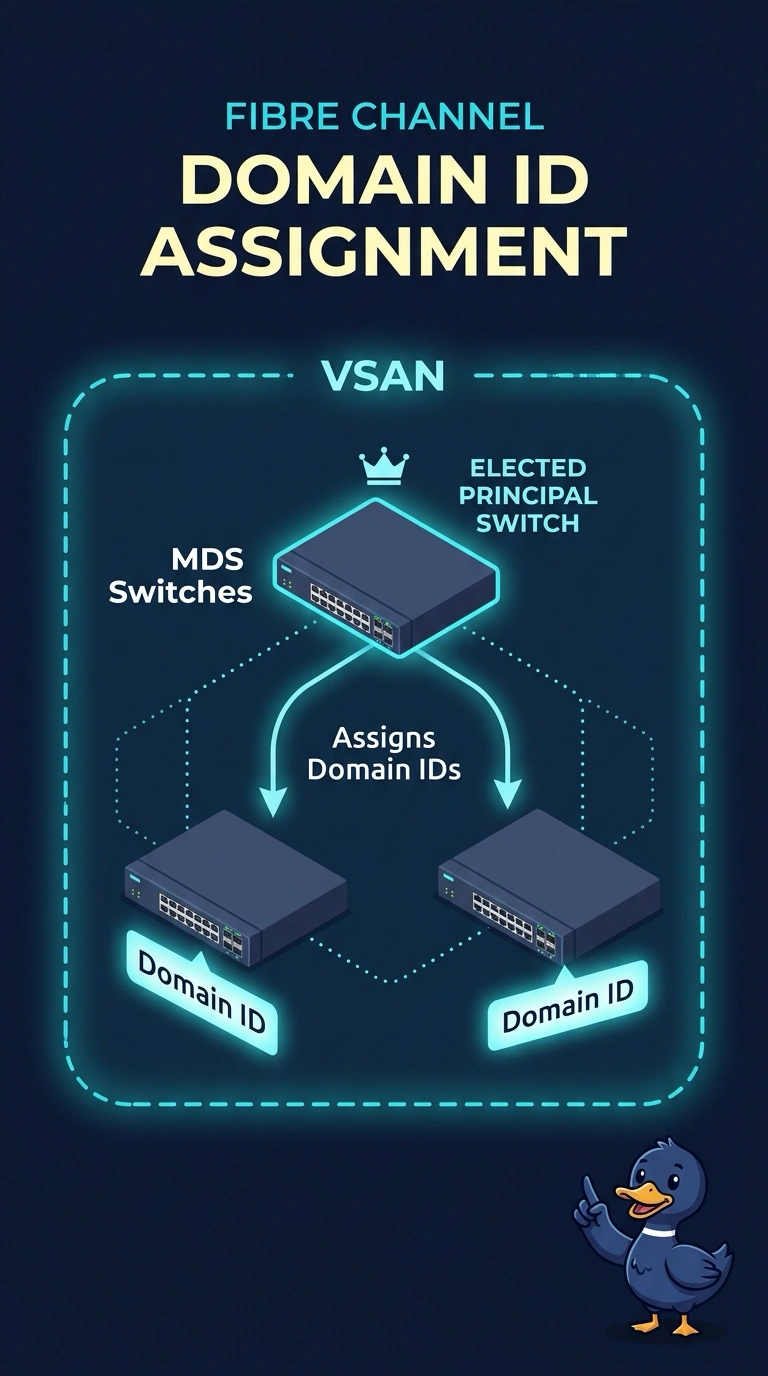
Short Explanation
The principal switch is the mayor who hands out city numbers. You look there when a new switch is given a domain ID, because that mayor is the switch allowed to grant it. The name server is the directory of hosts that already logged in, and it does not mint domain IDs.
Full Explanation
Each VSAN elects a principal switch, and that principal is the switch that allocates Fibre Channel domain IDs to the other switches in the VSAN. When a new MDS joins the factory fabric and receives a domain ID, the grant came from the principal for that VSAN, not from a host database or a configuration-sync master. The name server records N-port logins after FLOGI. Holding that directory does not make a switch the domain-ID authority. The low byte of an FCID identifies a port inside a domain that was already assigned. Comparing port bytes does not tell you which switch granted the domain. CFS distributes selected databases, including device aliases, and it can have its own merge behavior. The CFS role is not the principal-switch election and it does not hand out domain IDs. Caveat: the principal is per VSAN, so the switch that is principal in one VSAN can be a subordinate in another. Operational check: display the domain status for the VSAN, identify the principal, and confirm the new switch's domain ID is one that principal allocated.