
A SaaS storage admin adds a host and a target to a new zone, adds that zone to the zoneset, and the host still cannot see the target. The zoneset was not activated again after the edit. What is the missing step?
Select an answer to reveal the explanation.
Short Explanation
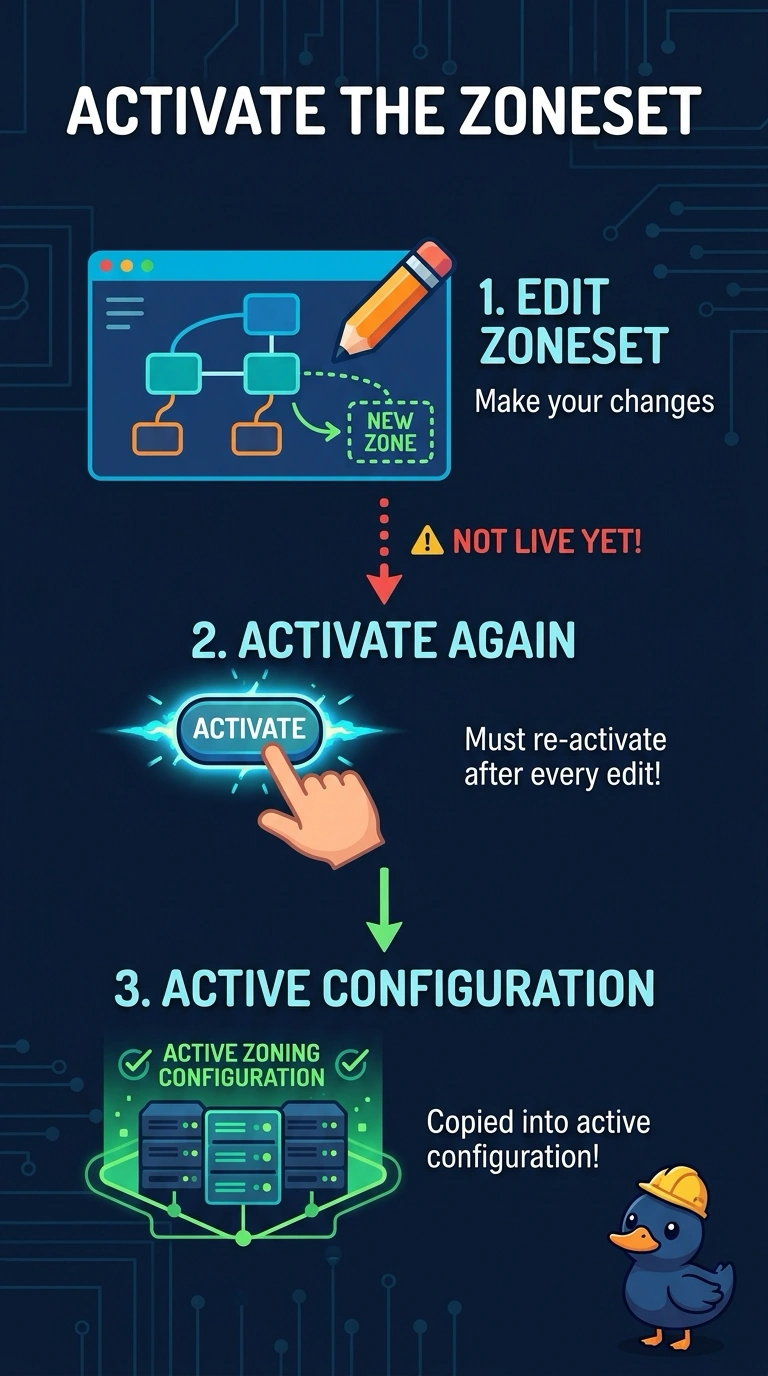
Editing a zoneset is drafting the guest list. You still have to activate it or the door staff keep using the old list. You are not waiting on a device-alias commit, and clearing the name server will not enforce a zoneset you never activated.
Full Explanation
On an MDS, changes to a zone or a zoneset stay in the configured database until the zoneset is activated for that VSAN. Activation is what copies the zoneset into the active enforcement plane the switch actually uses. The SaaS host cannot see the target because the new zone was never activated, even though it sits in the configured zoneset. A CFS commit of the device-alias database distributes friendly names. It does not activate zoning. NPV on the target's switch would change that switch into an edge that does not run a full fabric, and it does not inherit or activate a zoneset by itself. The FCNS name server records who has logged in. Clearing it drops directory entries until devices log in again, and it does not push a configured zoneset into the active set. Caveat: a full zoneset activation can briefly affect the VSAN, and if the zone is missing from the zoneset you activate, the members stay isolated. Operational check: activate the zoneset in the correct VSAN, confirm the zone is in the active zoneset, and have the host log in again and rescan for the target.