
A game studio built a VLAN pool and a physical domain, and the server port uses an interface policy group. Endpoints still do not come up on those VLANs. The attachable access entity profile on that group does not reference the domain. What should be linked?
Select an answer to reveal the explanation.
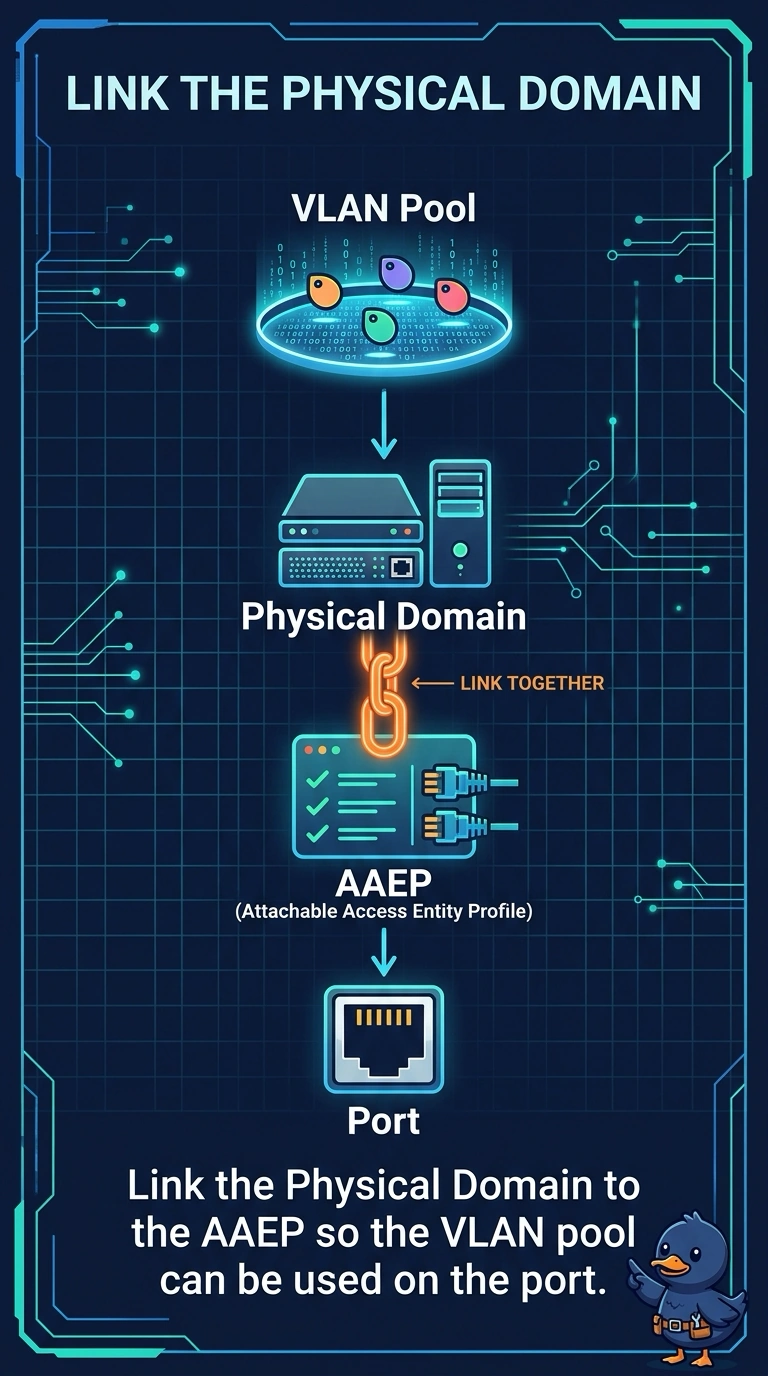
Short Explanation
The access policies are a chain, and one open link drops the whole VLAN. You attach the physical domain to the attachable access entity profile that the interface policy group uses. A contract does not deploy a VLAN pool onto a leaf port.
Full Explanation
ACI access policy is a chain from VLAN pool to domain, from domain to an attachable access entity profile, and from that profile to the interface policy group on the switch port. The studio built the pool and the domain, and the port has a policy group, but the attachable access entity profile does not reference the domain. Without that link the VLAN pool is not deployed on the port, so endpoints do not come up. Associating the physical domain with that profile closes the chain. A contract permits traffic between EPGs that are already classified. It does not push a VLAN pool onto a leaf interface. Hardware proxy tells the fabric how to handle unknown unicast inside a bridge domain. It does not attach access VLAN pools to ports. The infrastructure VLAN is reserved for fabric control. Putting it on a spine does not replace the attachable access entity profile and does not deploy a tenant VLAN pool. Caveat: the interface profile still has to be bound to a switch profile that includes this leaf, or a correct entity profile never reaches the port. Operational check: link the domain to the entity profile, then confirm the port accepts the VLAN and an endpoint learns.