
A SaaS UCS domain has free blades that meet every server pool qualification. New service profiles stay unassociated and report that a WWPN cannot be assigned. The WWPN pool has no free addresses. What has to be expanded?
Select an answer to reveal the explanation.
Short Explanation
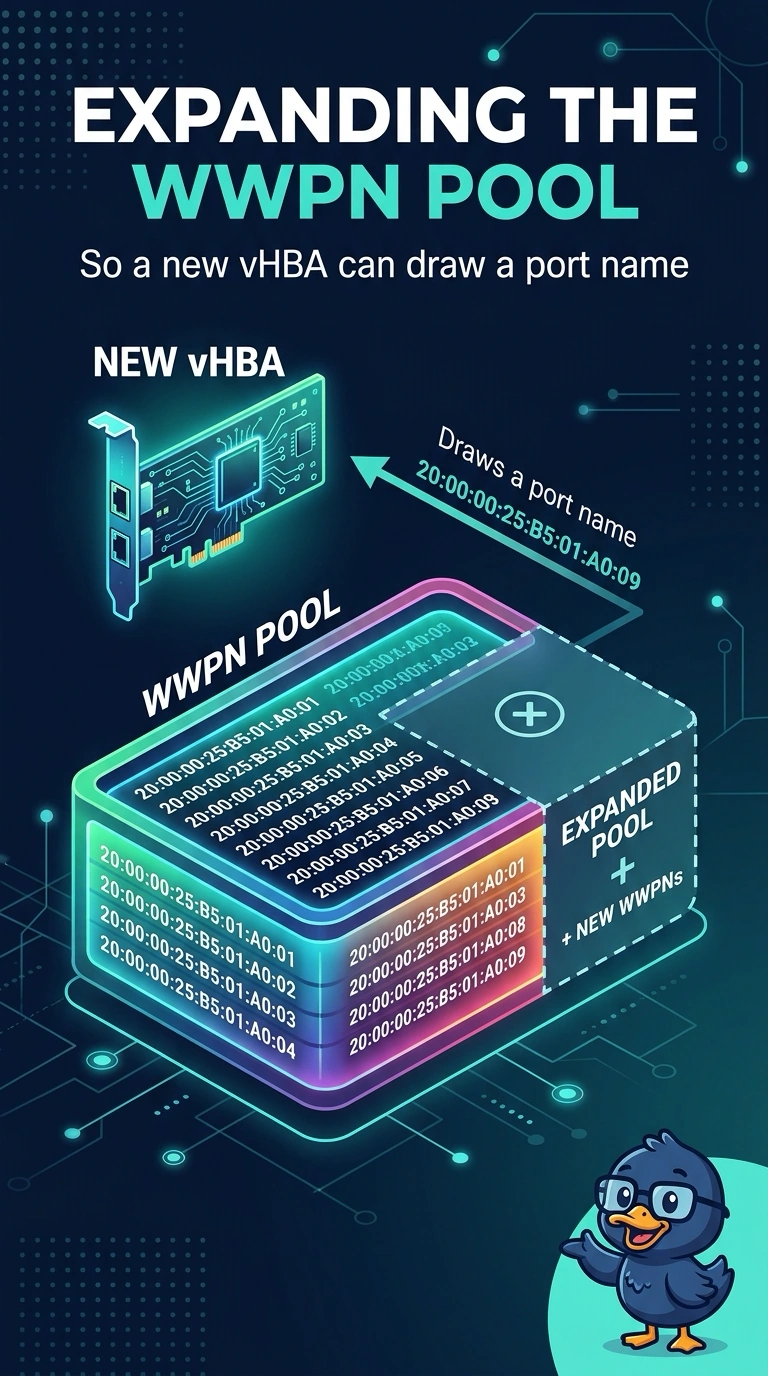
The desks are empty and your bin of name badges is not. The blades qualify for the pool, so the profile cannot associate because the WWPN pool has nothing left to hand a vHBA.
Full Explanation
A vHBA draws its port WWN from a WWPN pool when the service profile is associated. An empty pool stops that identity assignment, and the profile stays unassociated even though spare blades meet the CPU, memory, and adapter qualifications. Expanding the WWPN pool is what unblocks association, because that is the pool the vHBA draws from. Tightening or expanding a memory qualification would matter if a blade were failing the pool rules. These blades already pass. The discovery link count affects whether a chassis is discovered. It does not mint WWPNs. A host firmware package selects server code. It is not the identity pool that failed. Caveat: the new addresses have to be unique in the fabric. Overlapping another domain's WWPN range will let association succeed and then confuse the SAN. Operational check: add addresses to this WWPN pool, associate one profile, and confirm the vHBA WWPN came from the expanded pool before you associate the rest of the batch.