
A logistics company wants an Intersight server profile assigned to a new rack server. The server is powered and reachable on the management network, but it has never been claimed. What has to happen first?
Select an answer to reveal the explanation.
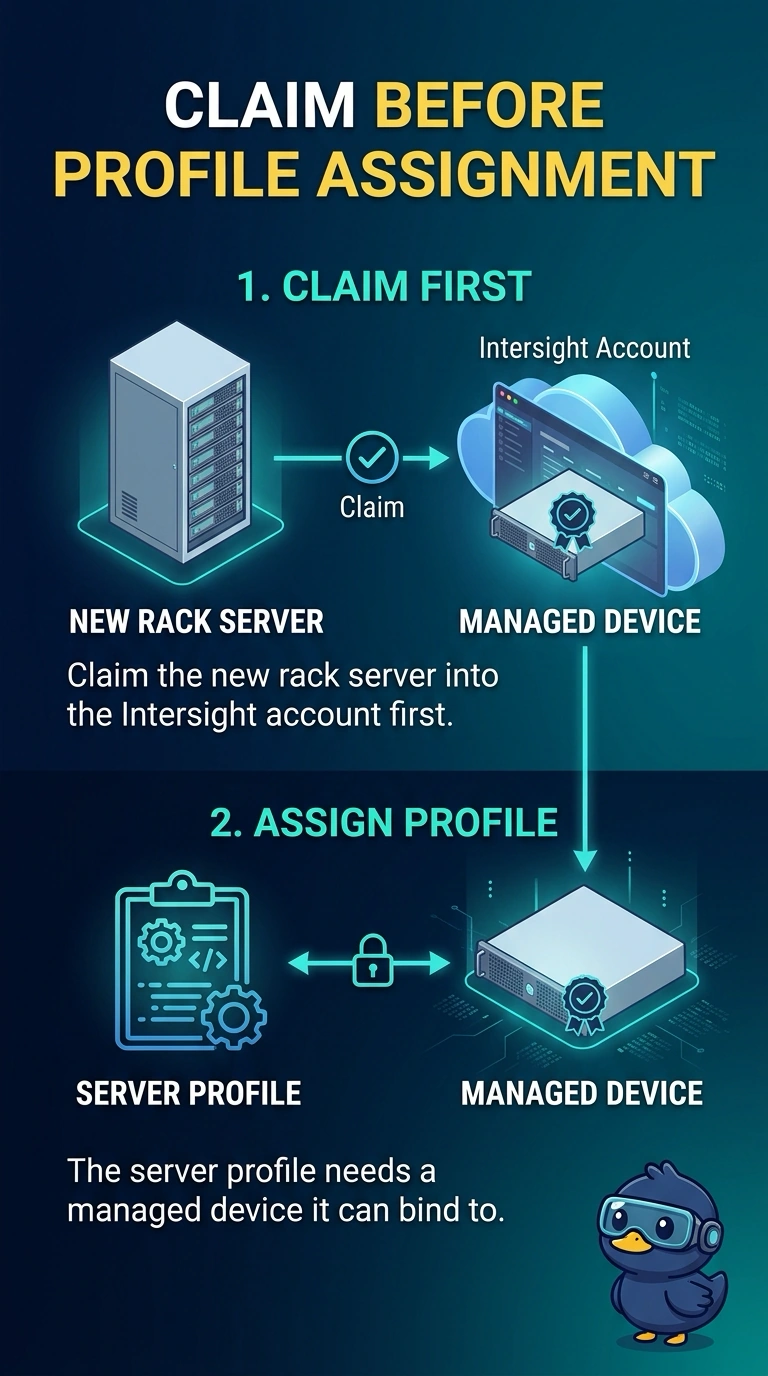
Short Explanation
Intersight cannot dress a server it has not been introduced to. You claim the rack server into the account first, and only then does a server profile have a device to attach to. A leaf bootstrap or a SAN zoneset does not perform that claim.
Full Explanation
Intersight automation acts on devices that have been claimed into the account. A claim ties the physical server, identified from its device connector, to the account so policies and server profiles have a target. Until that claim exists, the logistics server can be reachable on the management network and still be invisible to profile assignment. POAP bootstraps a switch that has no startup configuration. Running it on a leaf does not claim a rack server and does not create an Intersight server profile. An MDS zoneset controls which Fibre Channel devices may communicate in a VSAN. Naming a server there, even if you had a WWPN, is not an Intersight claim and does not attach a server profile. Guest shell is an on-box Linux environment for tools on a switch. Server profiles are not assigned from that shell, and the access switch is not the profile engine. Caveat: the claim uses the device identity the server presents, and a server that cannot reach the Intersight service will not complete the claim even if you start it. Operational check: claim the server, confirm it shows as claimed, then assign the server profile and verify the profile is associated to that device.