
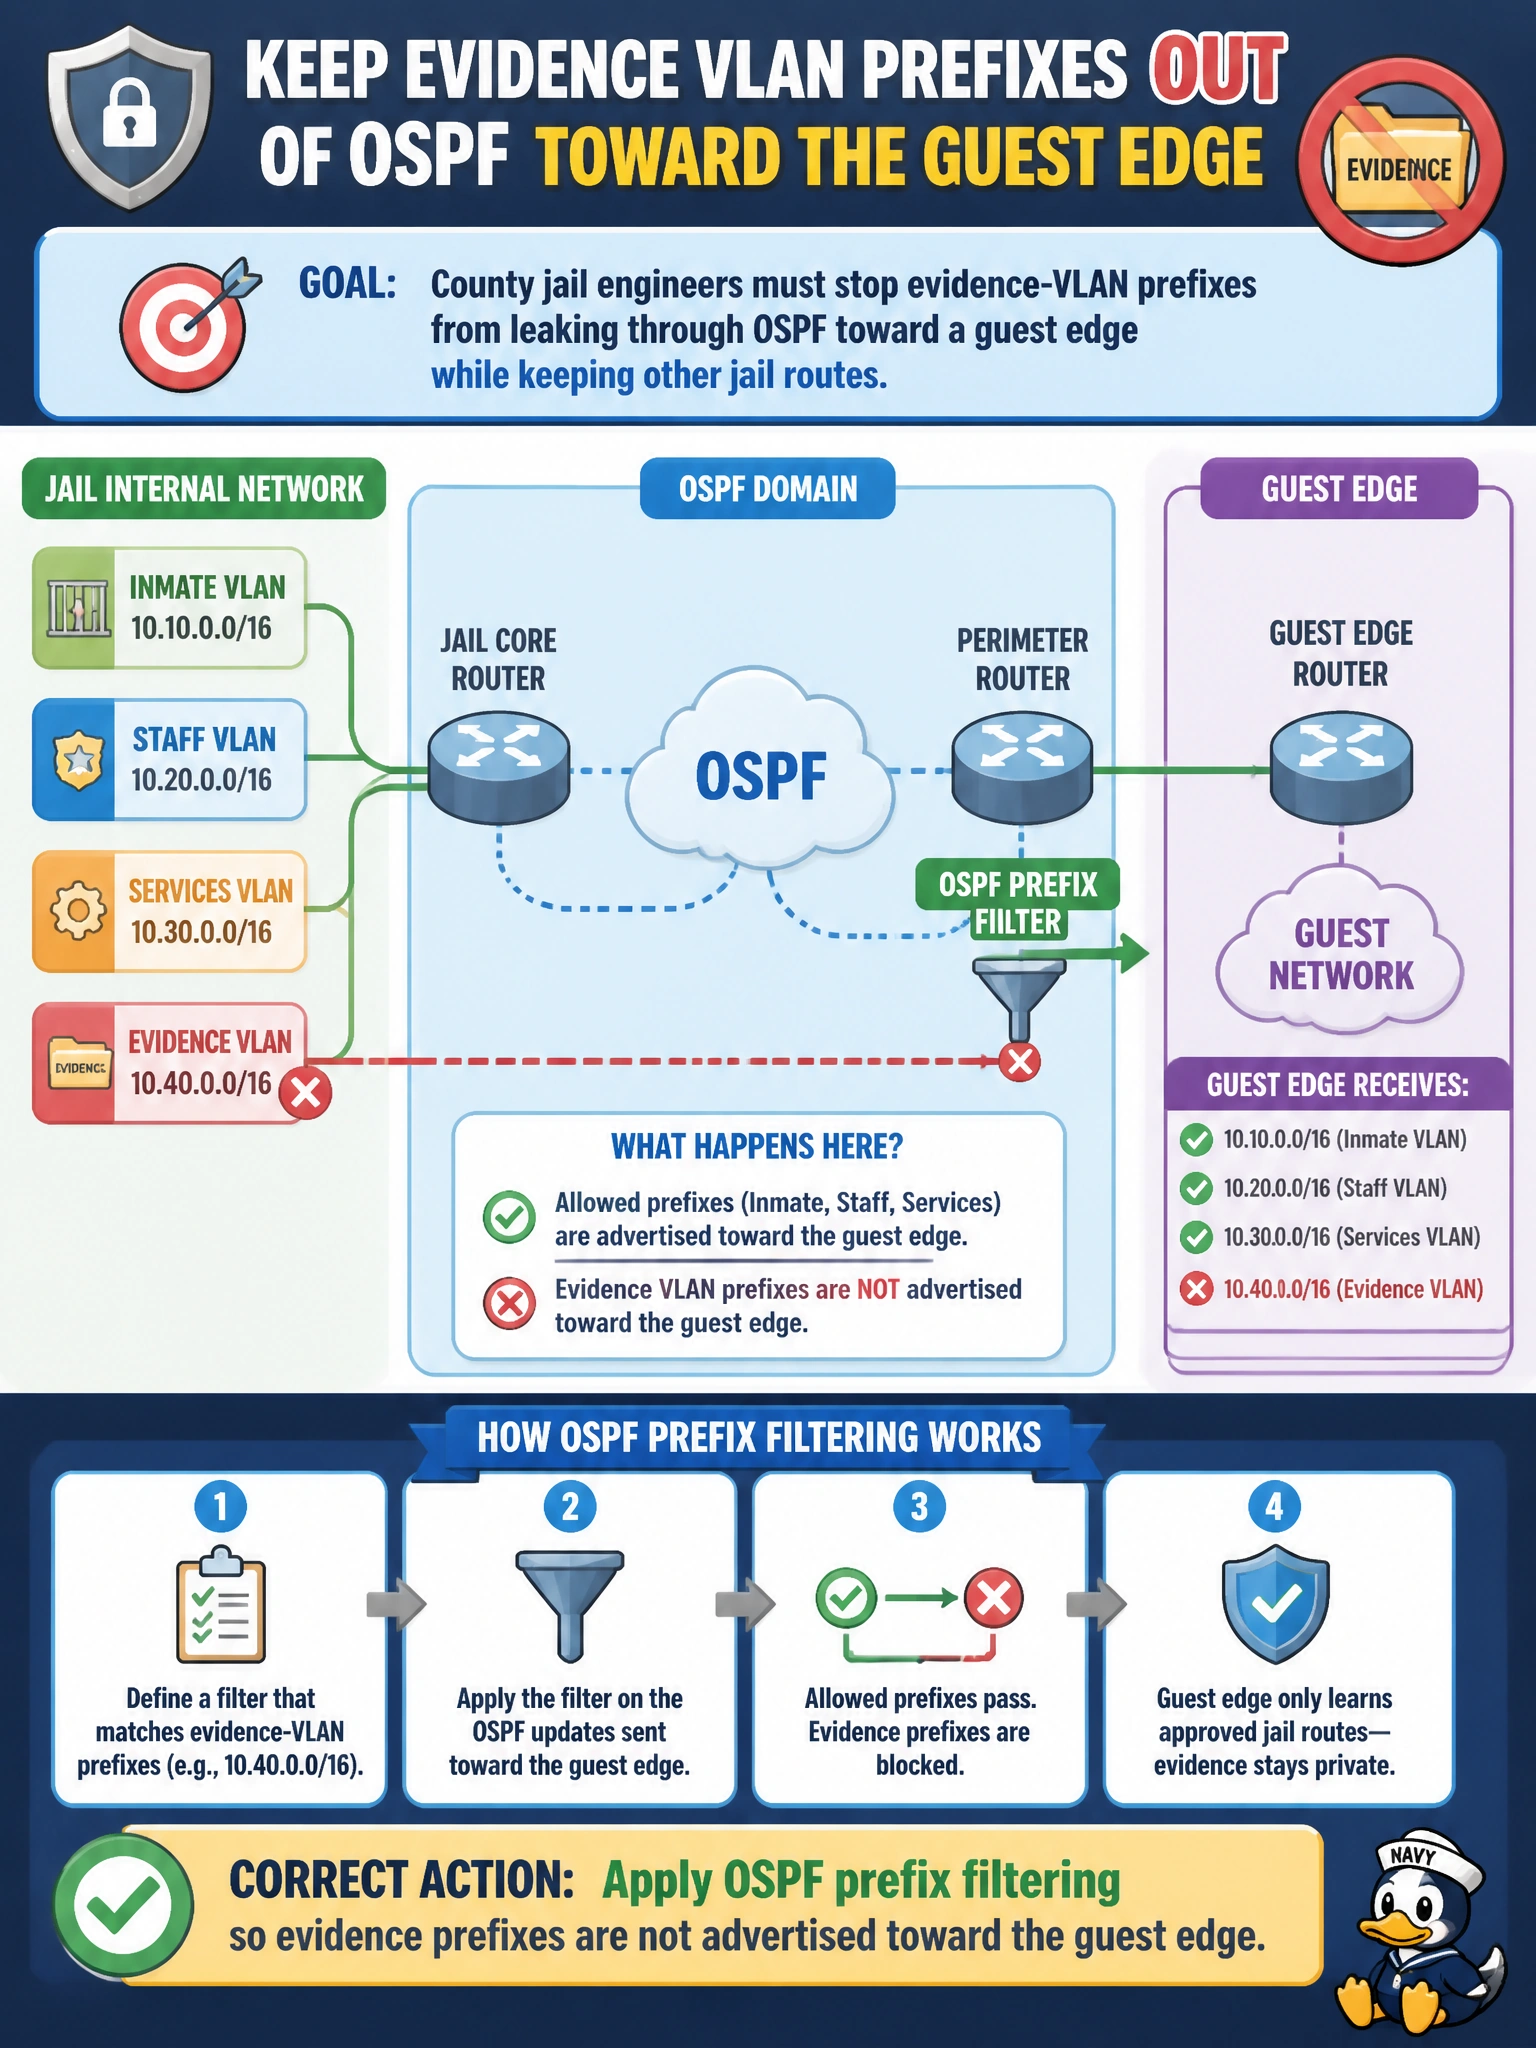
County jail engineers must stop evidence-VLAN prefixes from leaking through OSPF toward a guest edge while keeping other jail routes. Which action aligns with simple OSPF prefix filtering?
Select an answer to reveal the explanation.
Short Explanation
Prefix filtering is the jail's outbound mail screen — evidence folders don't get stamped for the guest wing. Other jail routes can still ship. Wiping gateways or DTP on NICs doesn't surgically filter OSPF advertisements.
Full Explanation
County jail engineers who must stop evidence-VLAN prefixes from leaking through OSPF toward a guest edge while keeping other jail routes should apply OSPF prefix filtering so evidence prefixes are not advertised toward that edge. Filtering at the appropriate OSPF advertisement boundary (commonly ABR/ASBR or distribute-list/prefix-list controls in simple designs) surgically suppresses evidence prefixes without deleting the VLAN's local routing role inside the jail. Other jail routes can continue to advertise as required.
Deleting the evidence VLAN's default gateway and hoping hosts discover NAT breaks local evidence networking and is not controlled OSPF filtering toward a guest edge. Enabling dynamic trunking on every evidence workstation NIC increases L2 risk and does not filter OSPF prefixes. Lowering all OSPF hello timers to one millisecond citywide risks instability and still does not selectively block evidence prefix advertisement.
Exam caveat: know where filters apply—inter-area Type-3 filtering vs external Type-5 vs redistribute filtering—and match the mechanism to the design. Intra-area LSAs are not freely filterable the same way; topology placement matters. ENCOR simple-prefix-filtering questions reward 'filter advertisements' over destructive gateway deletion.
Operational check: from the guest edge, confirm evidence prefixes are absent while other permitted jail routes remain; from inside the evidence VLAN, confirm local gateway and intra-jail routing still work. Review the prefix-list counters and document the evidence ranges for compliance. Re-test after any ABR change so guest Wi-Fi never re-learns evidence subnets via OSPF.