
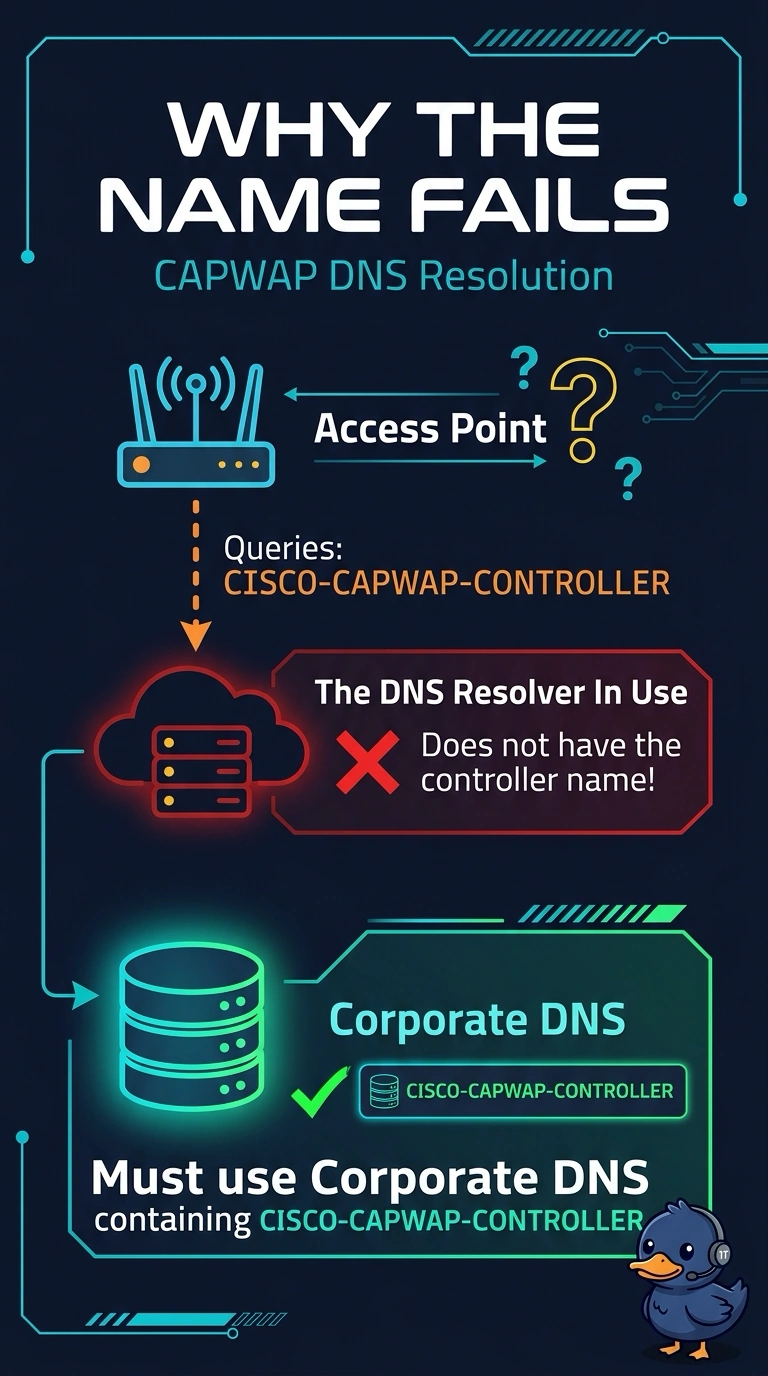
New access points use a public DNS resolver from the wrong scope. CISCO-CAPWAP-CONTROLLER exists only on the corporate DNS. They get an address and never join. Why does the name fail?
Select an answer to reveal the explanation.
Short Explanation
The access points are asking a resolver that has never heard of your controller. The name exists on the corporate DNS. Point them at that resolver, or stop handing them the public one.
Full Explanation
DNS discovery looks up CISCO-CAPWAP-CONTROLLER on the resolver the access point was given. These access points got a public resolver, and the name exists only on the corporate DNS, so the lookup fails and they never join. A public resolver does not automatically have a private controller name. The corporate DNS is not blocking the join by answering. It is the server that can answer, and these access points are not using it. Sniffer mode has nothing to do with which resolver answers. The access point uses a public resolver. The controller name exists only on the corporate DNS. The lookup fails. Check one live client after the change and leave the rest of the floor alone until that client matches the result you expected. Exam caveat: a correct resolver still fails if the domain suffix is missing and the record is not at the root of that zone. Check the name that is actually queried. Operational check: give an access point the corporate resolver, confirm the lookup returns the controller, and confirm the access point joins.