
Access points in the same VLAN as a Catalyst 9800 join by broadcast. Access points in a new VLAN never join. That VLAN has no DHCP option 43 and no DNS entry for the controller. Why do the new ones fail?
Select an answer to reveal the explanation.
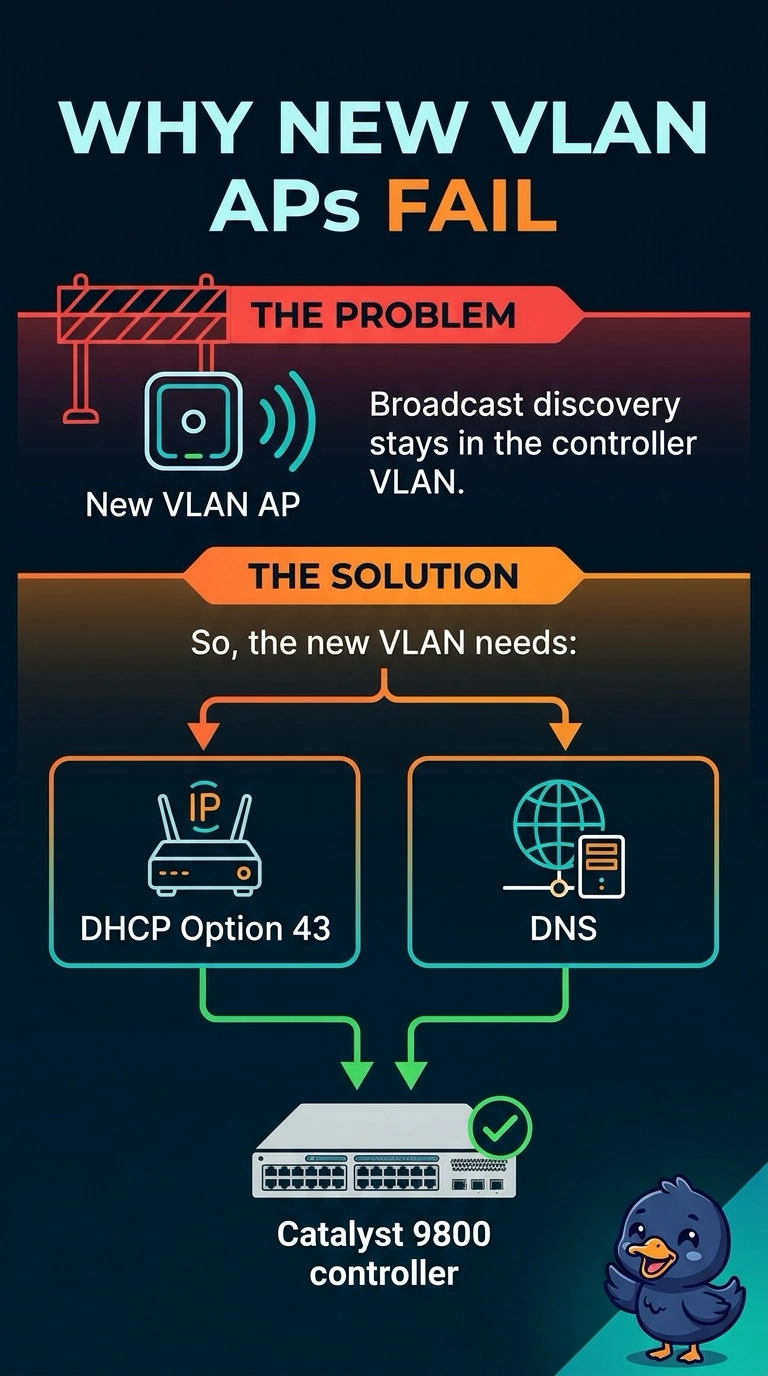
Short Explanation
Your local broadcast discovery stays in the controller’s VLAN; it does not reach the new VLAN. With no option 43 or DNS entry to point your access points to the controller, they cannot join. Add option 43 or the controller’s DNS name for that VLAN.
Full Explanation
Layer 2 broadcast discovery reaches the controller when an access point is in the same VLAN, but it does not cross into the new VLAN in the setup described. Since that VLAN has neither DHCP option 43 nor a DNS entry for the controller, its access points have no discovery direction and do not join. A local shout is not forwarded into every subnet, and the vendor field does not erase a hostname; option 43 supplies an address when configured. Sniffer mode is not a join method for access points in a new VLAN, regardless of option 43 or DNS. DNS is useful when an access point is outside the controller VLAN, not only when it is already local; the DNS name used for discovery is CISCO-CAPWAP-CONTROLLER. Exam caveat: apply the VLAN limit to the stated broadcast-discovery setup rather than assuming the broadcast reaches other subnets. Practical check: configure option 43 or the controller’s DNS name in the new VLAN, then confirm that an access point joins the production controller.