
A factory lab wants 802.1X for six laptops and has no RADIUS server on site. The production WLAN must keep using the corporate RADIUS servers. What fits the lab WLAN?
Select an answer to reveal the explanation.
Short Explanation
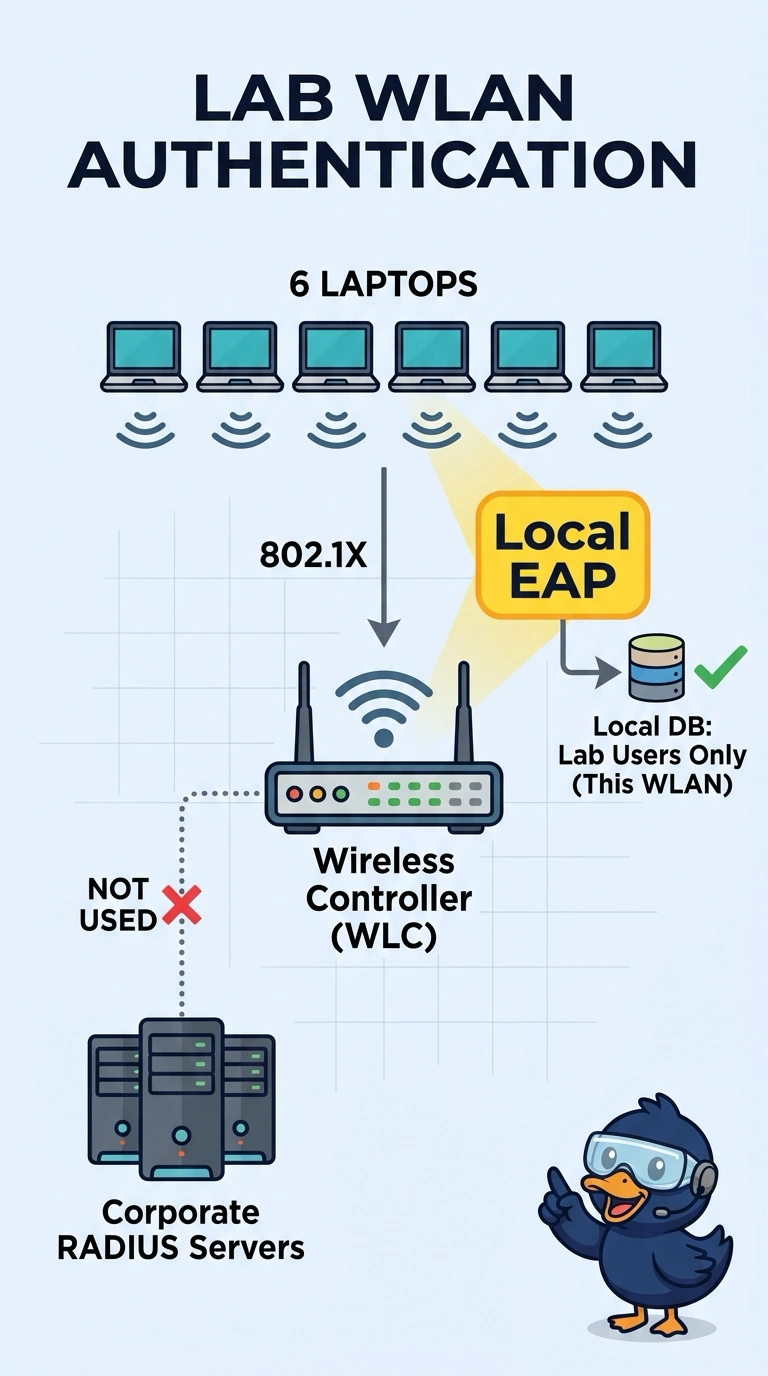
Six laptops need a real login, and you do not have a RADIUS server in the lab. The controller can be the authenticator and the user store for that one WLAN. An open network is not 802.1X with the password removed.
Full Explanation
Local EAP lets the controller terminate EAP for selected users it stores, which fits a six-laptop lab with no RADIUS server. The production WLAN can keep its corporate RADIUS servers. The lab WLAN is the one pointed at local EAP. Open authentication does not perform 802.1X and does not consult a user list. A hidden SSID only removes the name from beacons. It does not create credentials or an EAP exchange. Monitor mode scans and does not serve or authenticate clients. The six laptops would have no WLAN to join on that access point. The lab users exist only for that WLAN. Production clients continue to use the corporate servers, which is the split this factory needs. Exam caveat: local EAP is a small-scale tool. The lab user list is not a second copy of the corporate directory, and a laptop that works in the lab will fail on the production WLAN if its account exists only on the controller. Operational check: join a lab laptop, confirm the controller authenticates it locally, and confirm a production client still hits the corporate RADIUS server.