
A hotel reception desk runs the ISE sponsor portal. Desk clerks must create one-day visitor accounts when guests arrive, only the security manager may extend or revoke those accounts, and only the IT administrator may create or disable sponsor logins. Which sponsor group design applies the required permission split across the three roles?
Select an answer to reveal the explanation.
Short Explanation
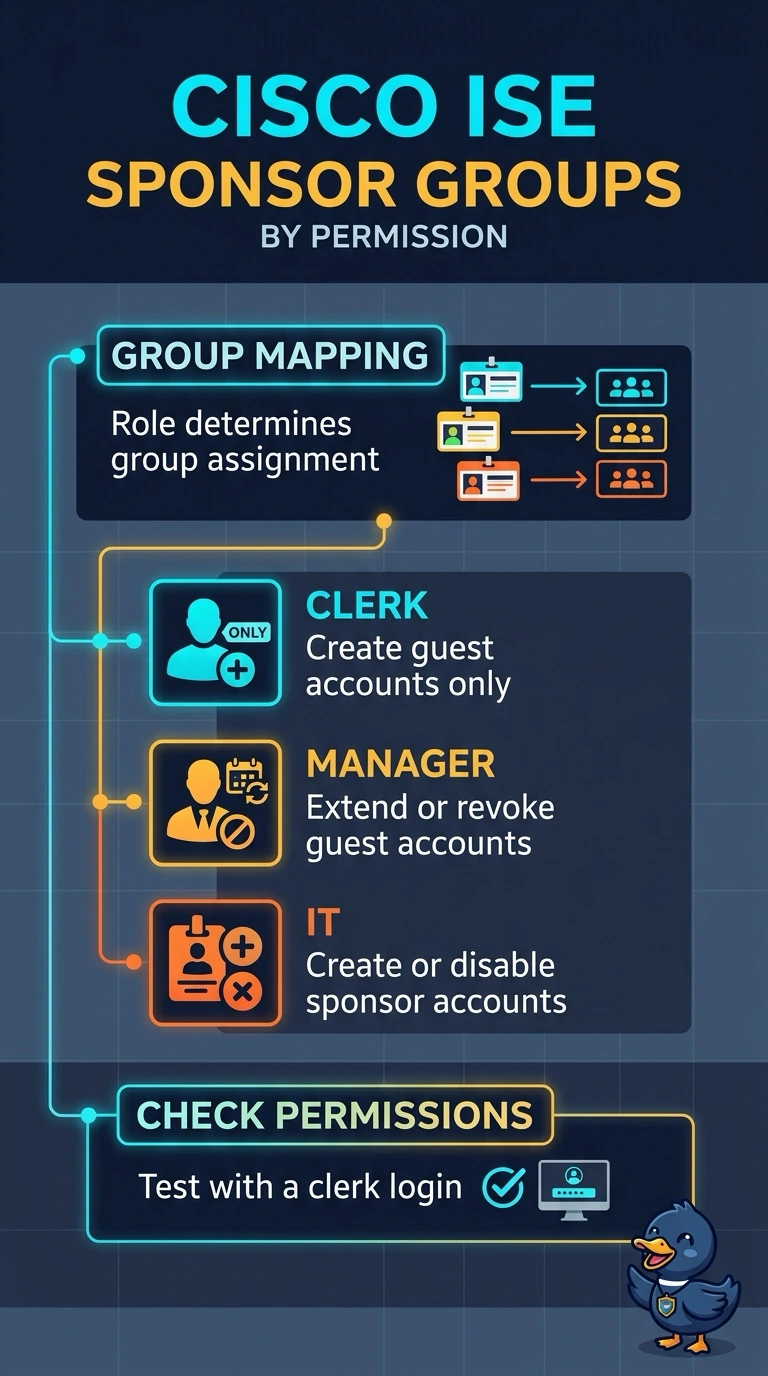
You can split the duties into three sponsor groups: clerks create guest accounts, the security manager manages those accounts, and IT manages sponsor logins. That keeps each person’s access focused on their role, so sponsor group permissions match your boundaries.
Full Explanation
The design that gives clerks guest creation only, the security manager guest-account management, and IT sponsor-account management matches the required split. Clerks can create the one-day visitor accounts needed at reception, while only the manager can extend or revoke them, and only IT can create or disable sponsor logins. Giving clerks both guest creation and management would let them extend or revoke accounts, violating the restriction that reserves those actions for the manager. Giving the manager guest-account management plus sponsor-login administration would let the manager create or disable sponsor logins, crossing the boundary reserved for IT. Giving IT both guest and sponsor-account management would let IT extend or revoke visitor accounts, which must remain the security manager’s responsibility. Exam caveat: distinguish guest-account management from sponsor-login administration; both involve accounts, but they are separate permission areas. Practical check: test representative clerk, manager, and IT logins. Confirm each can perform the permitted actions and is denied actions outside its role, especially extending or revoking a guest account and creating or disabling a sponsor login.