
During a compliance audit, a hospital must show which operating systems and server applications exist on a monitored VLAN. The FTD receives a copy of that VLAN's traffic on a passive interface, TLS on that segment stays encrypted, and the inventory must come from what the firewall already sees. Which Secure Firewall Management Center configuration produces the host and application inventory the auditor asks for?
Select an answer to reveal the explanation.
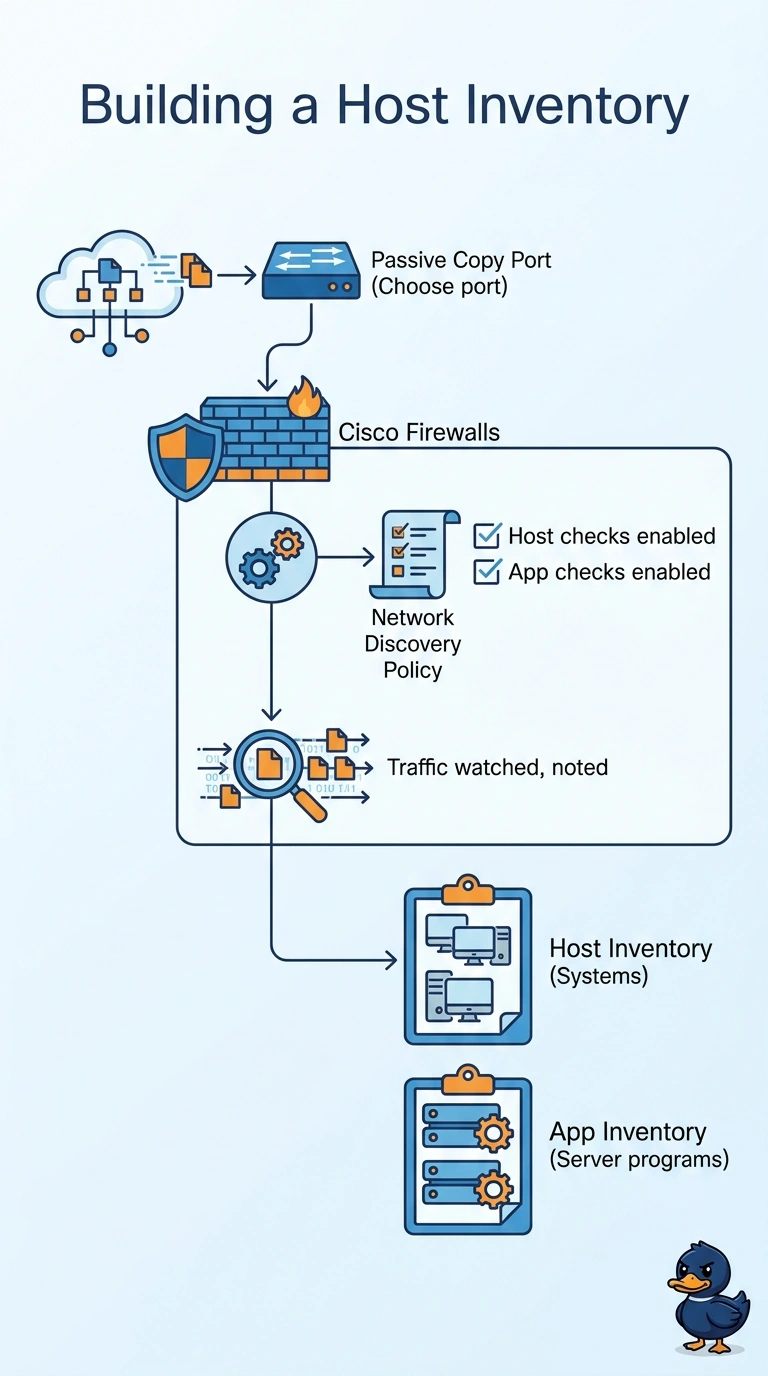
Short Explanation
Network discovery is the inventory engine, and its settings decide what actually gets written down. Enable host discovery and application detection, and the Management Center builds the host and application list for you. It's like a door attendant who notes every guest and what they carried in.
Full Explanation
Network discovery is built for exactly this audit: you attach a discovery policy to the interface that sees the segment's traffic, enable host discovery and application detection, and the Management Center accumulates host records such as operating system and device type plus application records such as server software and versions, and both collections sit in the inventory pages you can hand over. The encrypted visibility engine answers a narrower question, because it reads TLS fingerprints to label encrypted sessions, so it can enrich application knowledge but does not replace host discovery or supply the OS host records the audit needs. A correlation policy consumes events such as host discovery findings and raises an alert when a threshold is crossed, so it reports change rather than producing the baseline itself. The identity policy maps directory logons to addresses, which describes users instead of the software running on a machine. Exam caveat: discovery needs an interface that actually carries the segment's traffic, so the SPAN or passive copy port must be the one selected in the discovery policy. Practical check: after traffic has flowed, open the host inventory, sort by operating system, and confirm the counts match a quick spot check.