
A logistics firm wants external mechanics to reach one web-based maintenance portal while keeping their devices off the plant network. Security requires identity checks, device posture re-evaluated on every session, and reach limited to that single application. Which access design best fits the zero trust network access model?
Select an answer to reveal the explanation.
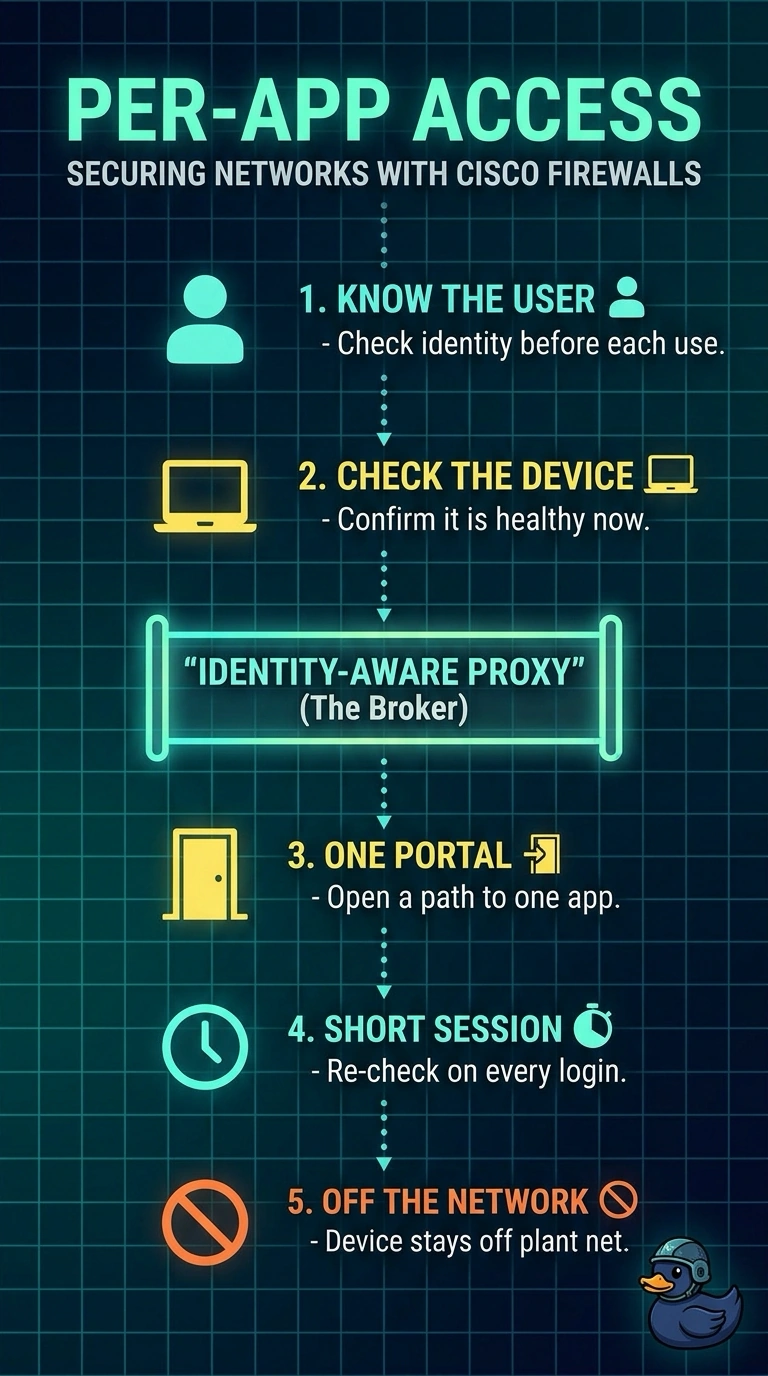
Short Explanation
Your rules call for per-application access that gets re-checked on every session, which a tunnel or a segment doesn't guarantee. An identity-aware proxy authenticates the mechanic, reads their device posture, then exposes just that one portal. Every new connection earns a fresh posture check instead of inheriting trust from the last one.
Full Explanation
The correct design uses an identity-aware broker to make an authorization decision for each session, checking both the mechanic’s identity and current device posture before granting access to the one web application. It keeps the device from joining the plant network and applies least privilege at the application level. A VPN can provide strong authentication, recurring posture checks, and a narrowly scoped firewall rule, but terminating the tunnel on the plant network still places the remote device on that network, contrary to the stated isolation requirement. A ZTNA gateway with per-session checks is not sufficient if its authorization exposes the entire maintenance segment: that grants network-segment access rather than access limited to the portal. A reverse proxy with MFA and device certificates can isolate the portal and verify identity, but a posture assessment only at enrollment does not re-evaluate device health on every session. Exam caveat: product labels such as “ZTNA” or “VPN” do not establish that a design meets the requirements; the actual enforcement scope and timing matter. Practical check: inspect policy and session logs to confirm each new session triggers identity and posture evaluation and receives a grant only to the portal, not to a subnet or other services.