
A hospital group's existing Management Center already governs its physical firewalls, and the team must add a Secure Firewall Threat Defense virtual appliance in AWS for a new outpatient portal. The cloud management interface must stay off the public internet, and policy must remain in the existing FMC. Which virtual deployment and registration design meets both requirements?
Select an answer to reveal the explanation.
Short Explanation
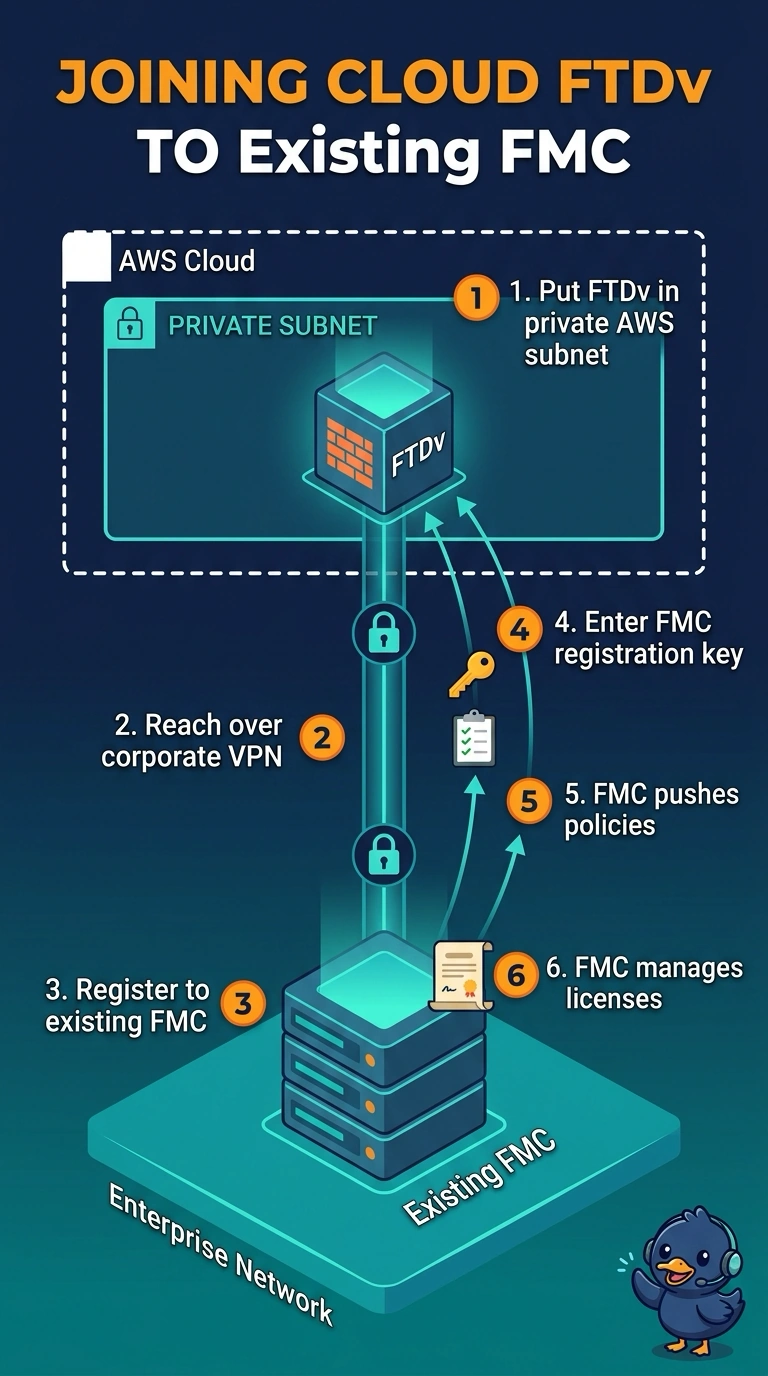
Your two constraints pull in different directions: one console has to keep control while the cloud management interface can't be exposed to the public internet. A private subnet reached over the corporate VPN and registered to the existing FMC satisfies both. The link works like a private hallway between your data center and the AWS account.
Full Explanation
The correct design keeps the FTDv management interface in a private subnet, provides corporate administrators a private route over the VPN, and registers the appliance to the existing FMC. This preserves the hospital group's established policy-management point while avoiding public exposure of the management interface. Registering the appliance to a new FMC in AWS would keep management private, but it would split policy administration across management centers rather than keep policy in the existing FMC. Using FDM locally is a valid way to manage some standalone FTD deployments, but it bypasses the required FMC and its centralized policy workflow. Placing the appliance in a public subnet and limiting access with VPN egress rules may restrict who can connect, but it still gives the management interface a public-internet path; access controls do not make that interface private. Exam caveat: distinguish the subnet's route-table classification from whether an interface is actually reachable from the internet; verify the management interface has no public IP or public route. As a practical check, confirm the VPN route and security rules allow management only from approved corporate networks, then verify the FTDv appears in the existing FMC and receives policy there.