
An FTD active/standby pair is cabled with a dedicated failover link, and the standby unit takes over promptly whenever the active unit loses power. After every switchover, established TCP sessions reset and users must reconnect. Which link carries the session data that keeps those connections alive?
Select an answer to reveal the explanation.
Short Explanation
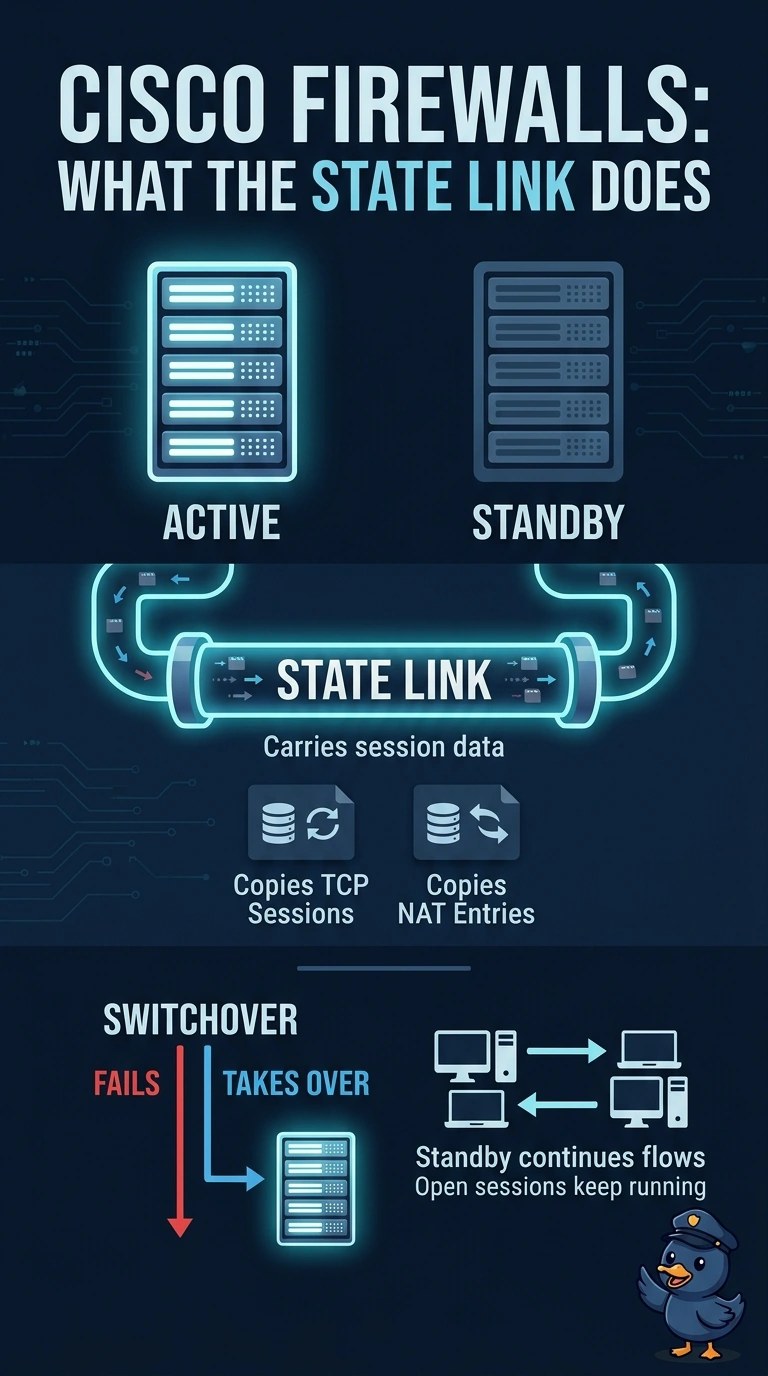
You're seeing the classic split of duties between the two HA cables: heartbeats move the role, sessions move elsewhere. The state link replicates connection and NAT entries so the standby can carry traffic mid-stream. It works like a substitute getting the playbook, not just a whistle from the sideline.
Full Explanation
The state link is the correct choice because it replicates the active unit’s connection and NAT table entries to the standby. When those entries are available at takeover, eligible established TCP flows can continue without requiring users to reconnect. The dedicated failover link has a different primary role: it carries health and role-status communication that lets the standby detect failure and assume the active role. That explains why takeover can be prompt even though sessions reset; failover detection alone does not preserve live connection state. Monitoring data interfaces is also useful in an HA pair, since a detected interface failure can trigger a role change, but interface monitoring reports health rather than copying connection-table entries. Configuration synchronization is necessary to keep the peers’ policies and NAT rules consistent, yet matching configuration does not provide the active unit’s current TCP and translation state. Exam caveat: failover and state functions may share a physical interface in some designs, so distinguish their logical roles rather than inferring them from cabling alone. Practical check: verify the state-link configuration and counters, then confirm that connection and NAT state is being replicated before testing a controlled switchover.