
For an upcoming audit, payroll and banking SaaS sessions on the inside zone must be decrypted so the web and intrusion policies see clear text. Pinned mutual-TLS health agents must keep connecting, and endpoints must show no certificate warnings. Which decryption policy arrangement meets all three requirements?
Select an answer to reveal the explanation.
Short Explanation
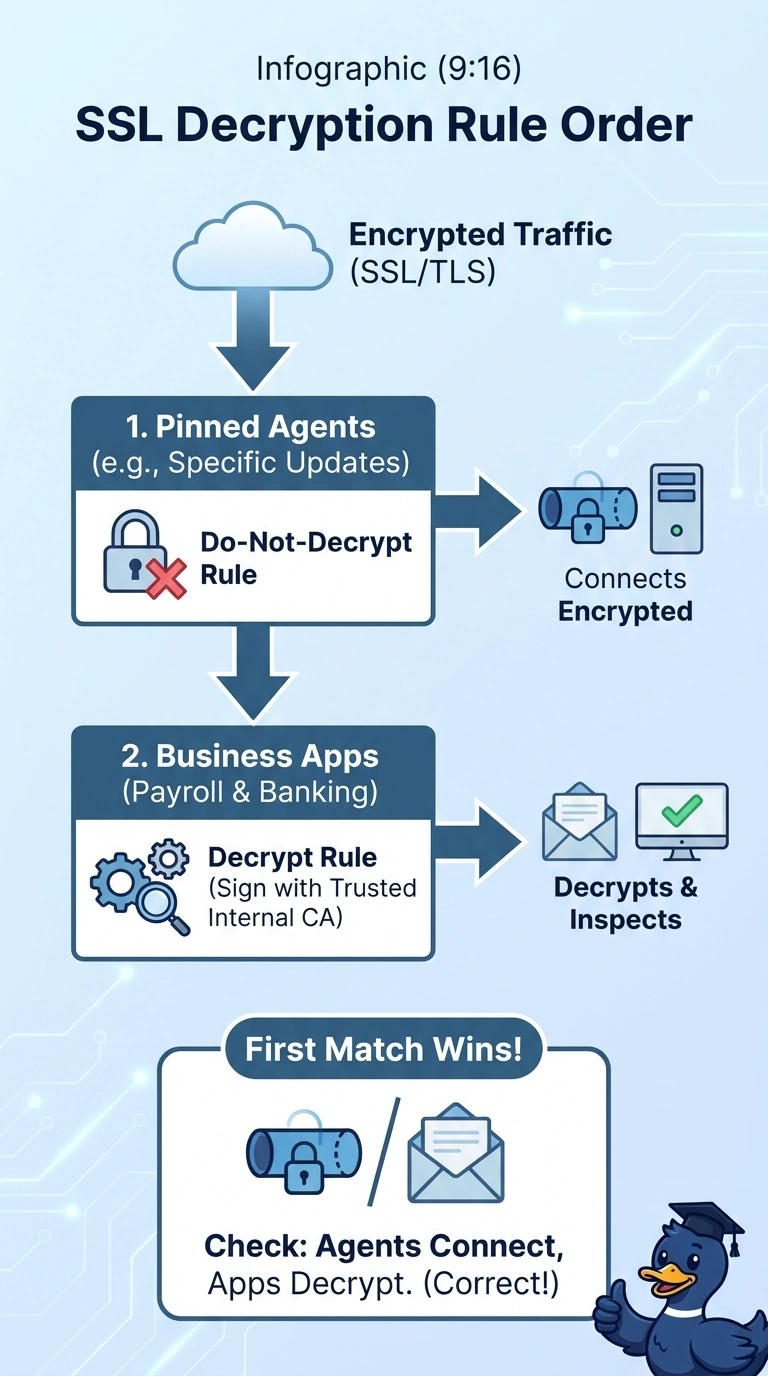
Your exception rule sits above the decrypt rules because policy matching stops at the first hit, so you'll never reach the second one. That works like an allergy note at the top of an order, seen before anything else. Your decryption policy then inspects payroll and banking while the pinned agents stay untouched.
Full Explanation
The correct arrangement exempts the pinned mutual-TLS health agents from interception, preserving their certificate and key expectations, while decrypting payroll and banking sessions with an internal CA trusted by endpoints. This gives the web and intrusion policies clear text for the SaaS traffic without causing certificate warnings. TLS metadata inspection is a legitimate way to apply controls when traffic must remain encrypted, and it preserves agent connectivity and endpoint trust; however, metadata such as certificates and names is not the clear-text session content required for these policies. Decrypting all inside-zone TLS with a trusted internal CA provides visibility and avoids warnings for ordinary clients, but interception changes the TLS peer seen by the pinned agents, so their mutual-TLS validation can fail and they may stop connecting. Using a private inspection CA can decrypt the SaaS sessions, but if endpoints do not trust that CA, they will display certificate warnings, violating the stated endpoint requirement. An exam caveat is that a no-decrypt exception must match the pinned agents narrowly; a broad exclusion could unintentionally leave payroll or banking traffic uninspected. In practice, verify the rule order and match criteria, confirm the inspection CA is trusted on managed endpoints, and test both SaaS decryption and agent connectivity with representative clients.