
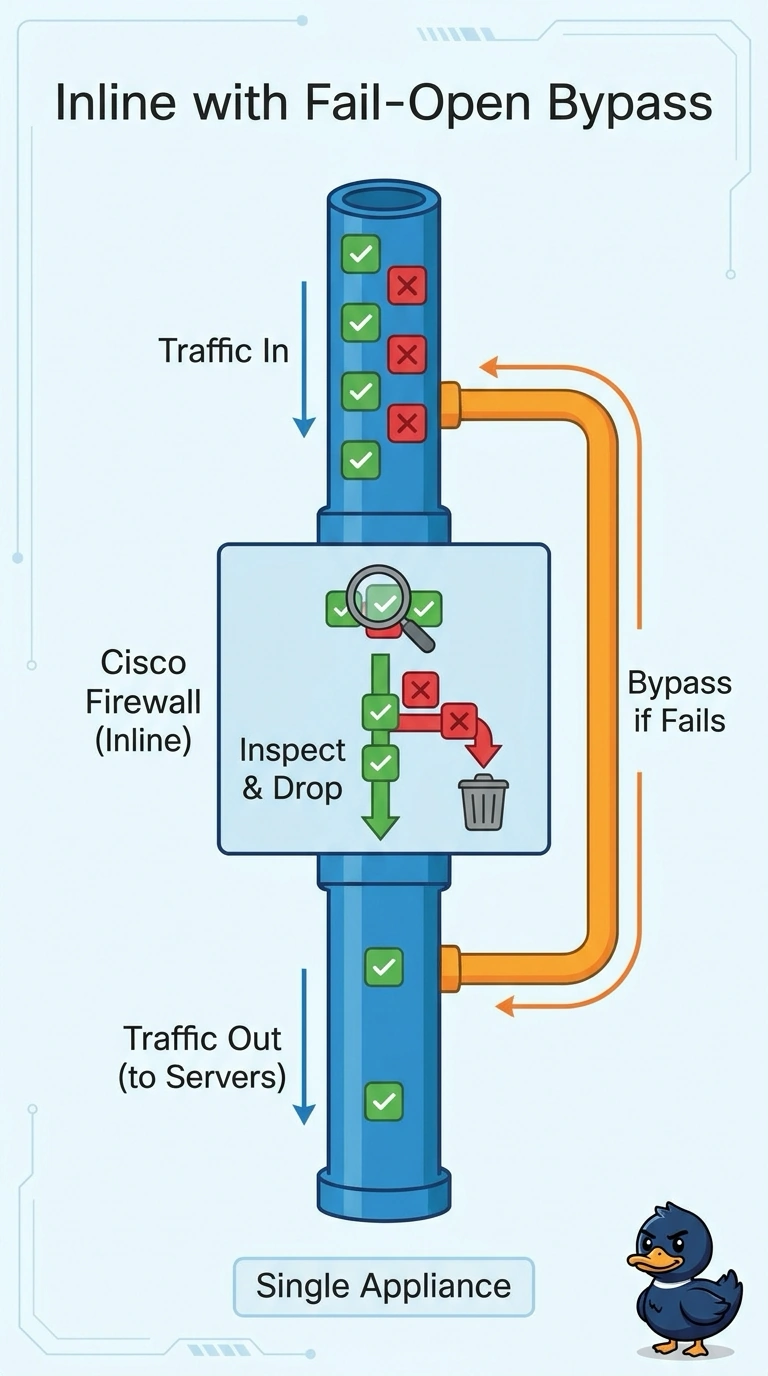
A mid-size insurer is placing one FTD appliance in front of its claims portal. The network team requires that exploit traffic be dropped before it reaches the servers, that the link keep forwarding if the inspection engine fails, and that only this single appliance be available. Which NGIPS deployment mode and failure behaviour should be used?
Select an answer to reveal the explanation.
Short Explanation
You need inline mode with fail-open bypass: it drops exploit traffic before it reaches your servers and keeps the link forwarding if inspection fails. Think of it as a security gate that blocks threats but swings open if its mechanism breaks.
Full Explanation
The required deployment is inline: inspection occurs in the traffic path, allowing a prevention policy to drop exploit traffic before it reaches the claims servers. Fail-open bypass addresses the separate availability requirement by allowing traffic to continue if the inspection engine fails, and the design uses only the single available appliance. Inline deployment with fail-closed bypass and a prevention policy can block attacks, but when inspection fails it stops forwarding rather than preserving the link. Inline deployment with fail-open bypass and an alert-only policy supports continuity, but reports matching exploits without dropping them; approval to enforce later does not meet the present prevention requirement. Inline deployment with fail-open bypass and a prevention policy that suppresses the relevant exploit signature has the right topology and failure behavior, but that exploit will not be detected and blocked by the IPS despite the general prevention setting. Exam caveat: fail-open describes behavior when inspection is unavailable; it does not mean traffic matching an active prevention rule is allowed through during normal operation. Practical check: verify the deployed policy contains an enabled blocking rule for the portal’s relevant exploit signatures, then test both a representative match and the configured inspection-failure bypass behavior.