
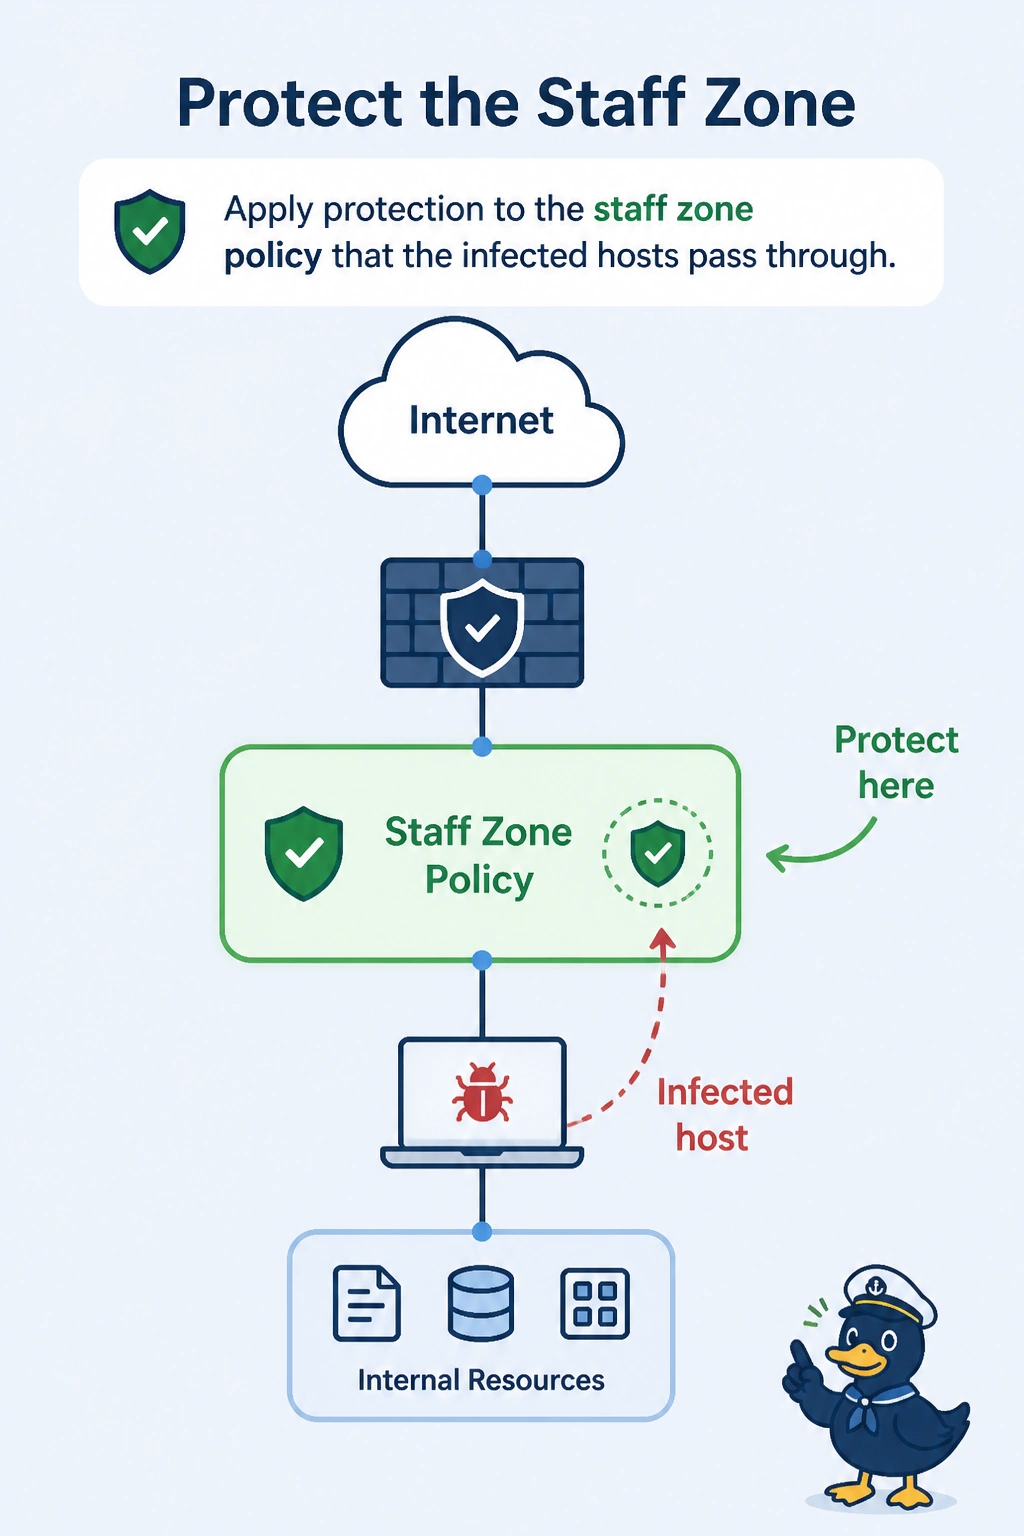
Malware protection is applied to the guest zone policy. Infected staff hosts in a different zone pass malware and never hit that policy. Routes exist. Where should the protection be applied?
Select an answer to reveal the explanation.
Short Explanation
The scanner is in the guest lobby, and the sick machines are in the staff hall. You apply malware protection to the staff zone policy those hosts actually pass through. Enabling it for guests does not scan a different zone.
Full Explanation
A security feature inspects only the zone policy it is attached to. Malware protection on the guest policy never sees staff hosts that use a different zone, so their malware passes even though routes exist. Attach the protection to the staff zone policy. The guest policy does not scan every zone because it is enabled. An OMP preference only changes a path. It does not inspect payload. A strict SLA does not scan for malware, and healthy loss would not be a reason to drop the staff sessions. Exam caveat: if staff also talk to guests, the guest policy still matters for that direction. The infected staff-to-internet flow needs the staff policy. Operational check: a staff test file the malware policy is built to catch should hit the staff counter and be dropped.