
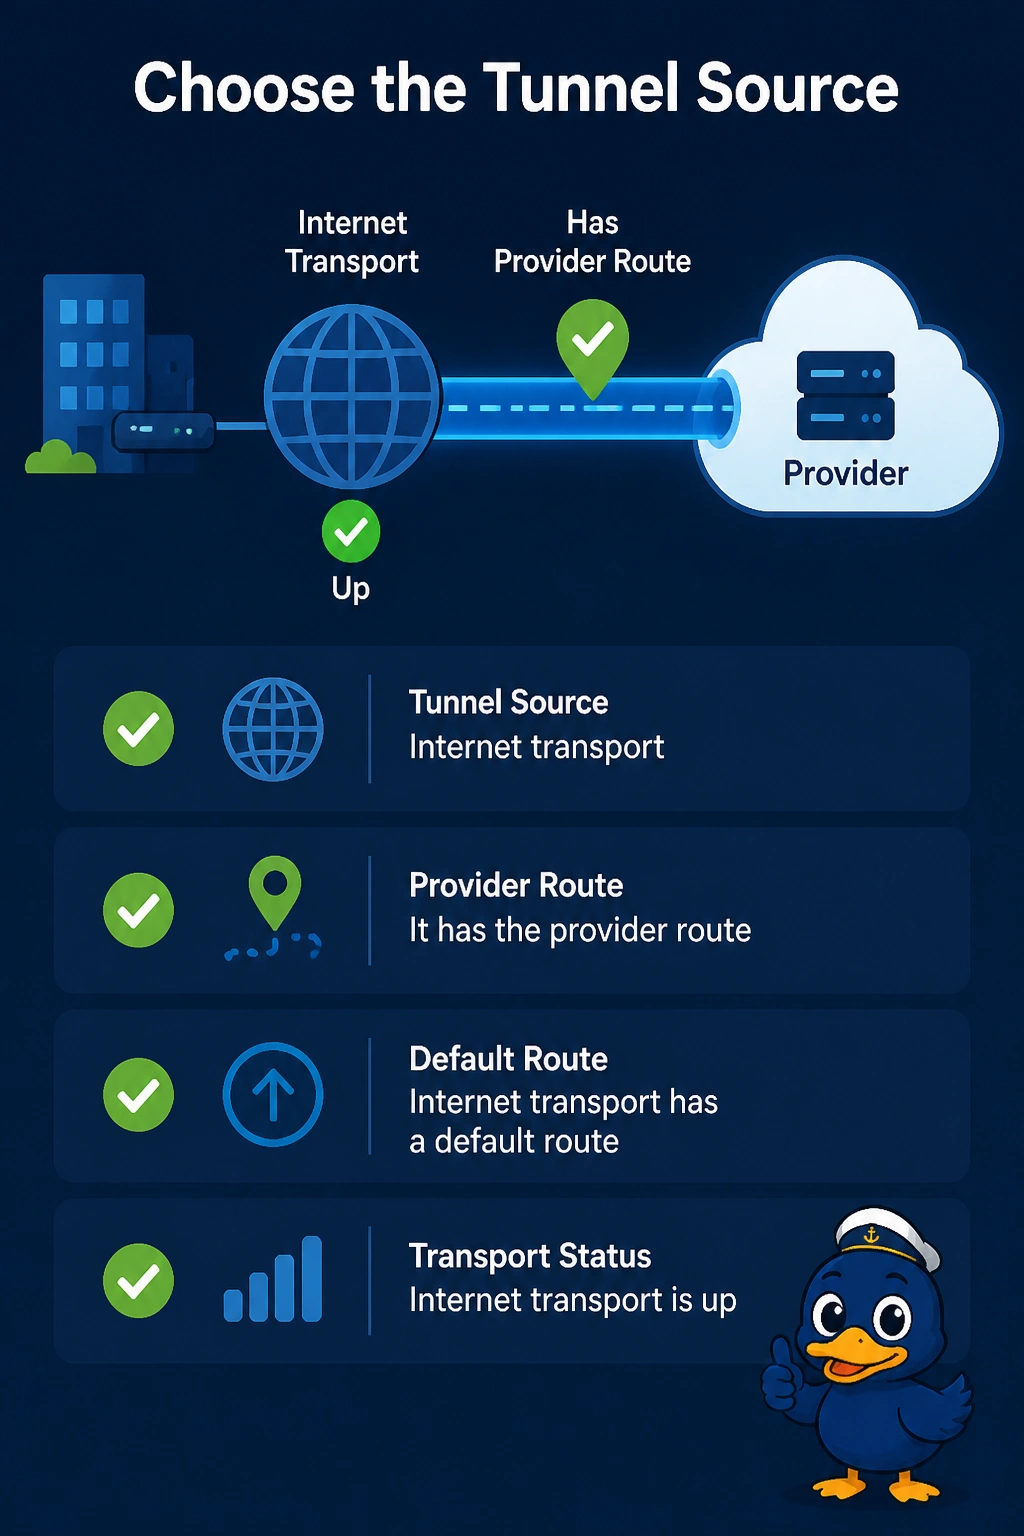
SIG tunnels from an edge stay down. They are sourced from an interface that has no route to the provider. The internet transport has a default route and is up. What should source the tunnels?
Select an answer to reveal the explanation.
Short Explanation
You addressed the inspection tunnel from a door that has no street to the provider. You source it from the internet transport that already has the route. An interface with an empty table will not reach the provider just because the feature is enabled.
Full Explanation
The SIG tunnel is ordinary underlay traffic toward the provider. Sourcing it from an interface with no route to that provider keeps it down. The internet transport has a default route and is up, so that is the source to use. The feature does not ignore the routing table. VPN 512 does not source SIG tunnels by default. The IaaS cloud gateway does not originate this edge's SIG tunnels. Those tunnels are built from the edge toward the security provider. Exam caveat: the source address still has to be one the provider allows, and NAT has to present that address if the transport is private. The right interface with the wrong public source fails the provider's allow list. Operational check: the SIG tunnel source should be the internet transport, and the provider portal should show the tunnel up.