
The secure internet gateway feature is set for one cloud security provider. The tunnel destination configured on the edge belongs to a different provider. The tunnels stay down. BFD to ordinary sites is up. What must match?
Select an answer to reveal the explanation.
Short Explanation
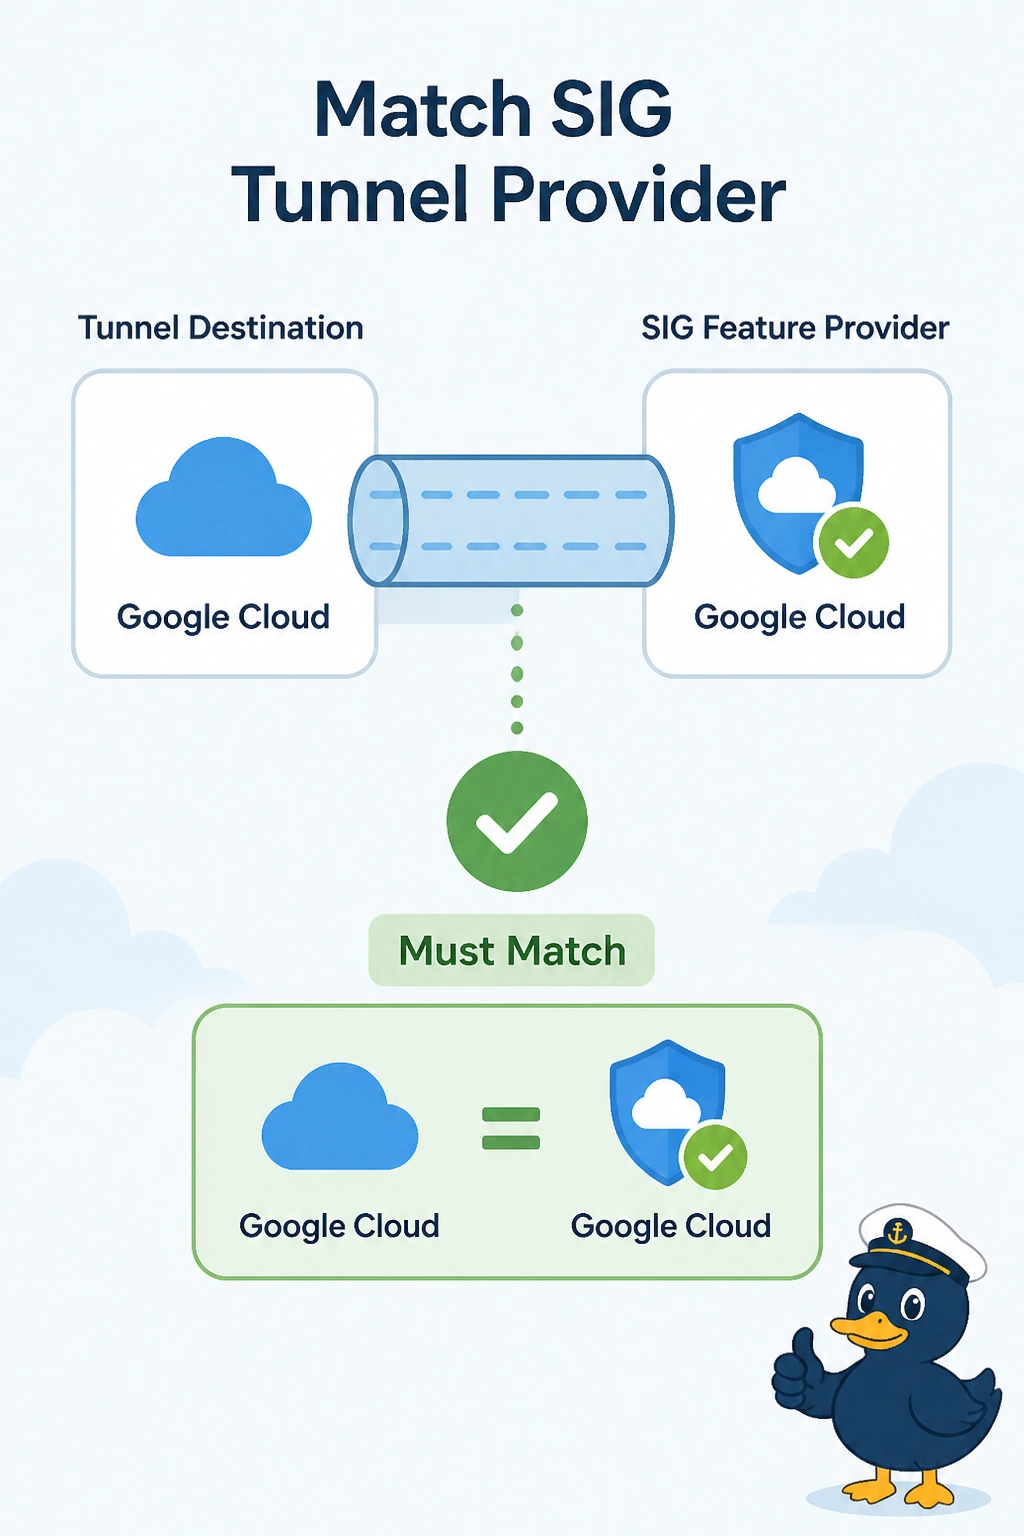
You aimed the inspection tunnel at a company you did not hire. You make the destination the provider the SIG feature is set to use. Ordinary sites are up, so the underlay is fine, and a voice class does not pick that provider address.
Full Explanation
The Secure Internet Gateway feature builds tunnels only to the provider it is configured for, at a destination that provider expects. This edge is pointed at a different provider, so the tunnels stay down while ordinary BFD proves the underlay. Change the destination to the selected provider, or change the feature to the provider you actually meant. The IaaS cloud gateway is a private VPC path. It does not terminate these inspection tunnels. VPN 512 is management and is not a prerequisite for the SIG destination. A voice SLA class chooses a path for voice. It does not select which security provider the tunnel should reach. Exam caveat: the encapsulation still has to match that provider's guide after the address is right. The correct company with the wrong GRE-versus-IPsec choice will stay down too. Operational check: the SIG tunnel destination should be the selected provider, and the provider portal should show the edge up.