
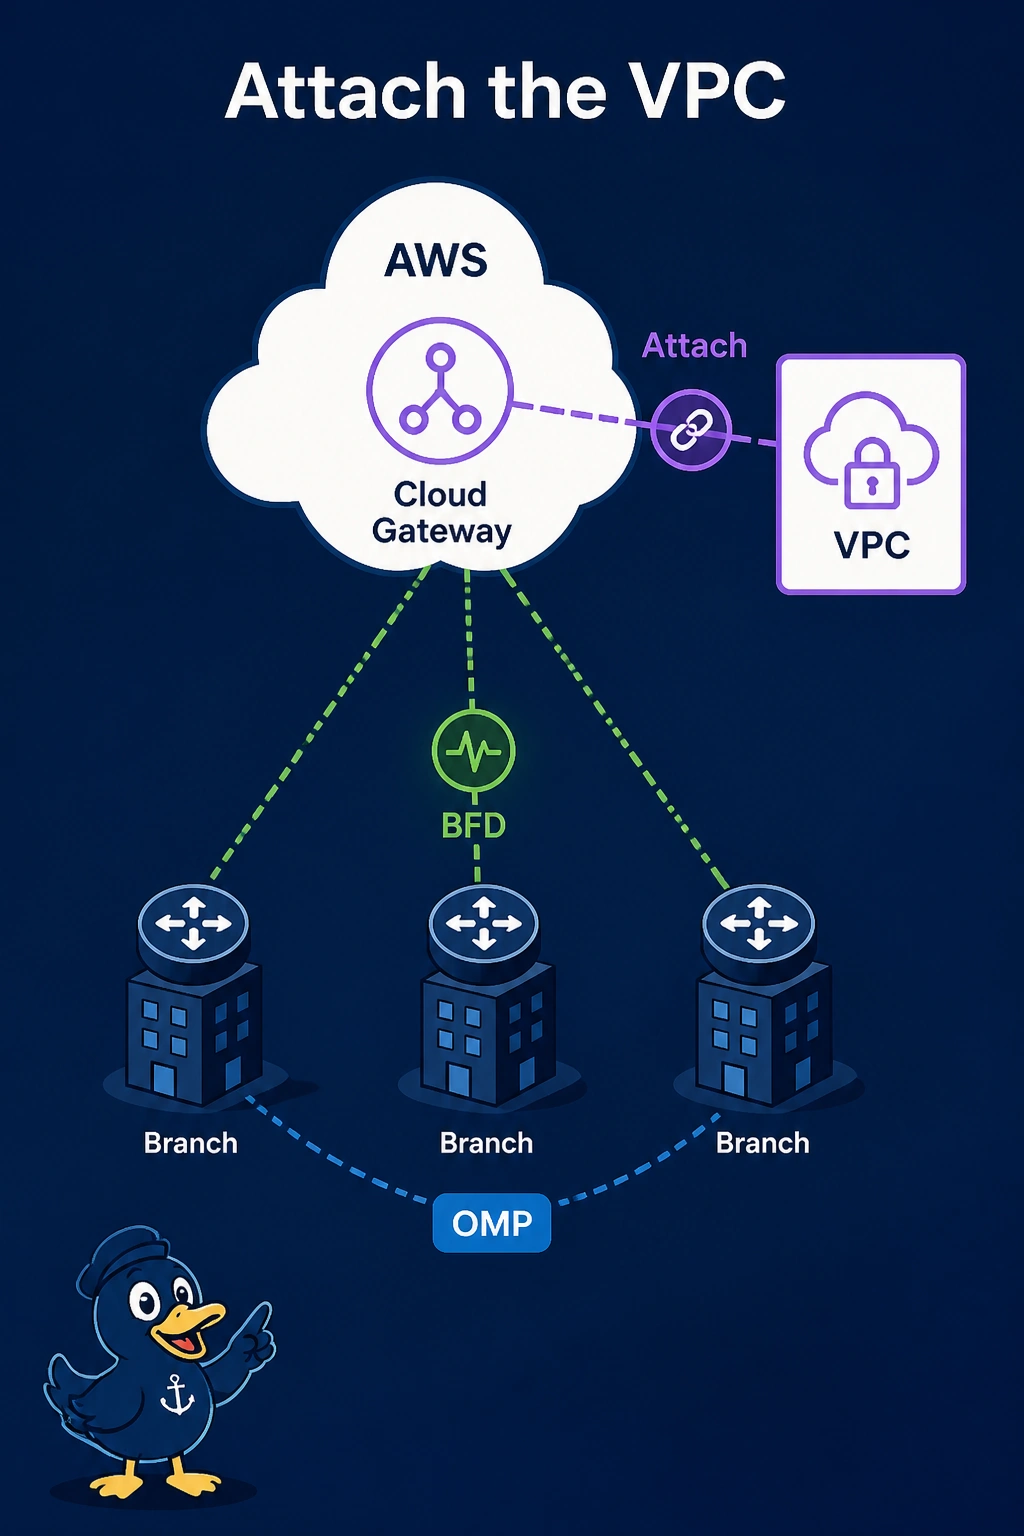
Branches have BFD up to an AWS cloud gateway and an OMP route for a VPC. Instances in that VPC stay unreachable. The VPC was never attached to the gateway. What is missing?
Select an answer to reveal the explanation.
Short Explanation
The branches can see the gateway, and the VPC was never plugged into it. You attach that VPC to the cloud gateway. A SIG tunnel does not finish an IaaS attachment, and a faster BFD hello will not create one.
Full Explanation
Cloud OnRamp for Multicloud reaches the instances only when the host VPC is attached to the cloud gateway and the routes land on both sides. BFD from the branches proves the overlay to the gateway. It does not prove the VPC is connected. This VPC was never attached, so the OMP route has nowhere to go inside AWS. Attach the VPC. A SIG tunnel inspects internet traffic. It does not connect a private VPC in place of the gateway attachment. VPN 512 is management and does not carry that attachment. A shorter BFD timer only sends hellos faster on a session that is already up. Exam caveat: the attachment still needs the VPC route table to point the campus prefixes at the gateway. Attaching the VPC and leaving the table pointed at a local internet gateway blackholes the return. Operational check: the cloud gateway should list this VPC as attached, and an instance should respond to a branch host after the route table is pointed at the gateway.