
Guest users in VPN 20 can see a VPC prefix that only staff in VPN 10 should reach. OMP installed the prefix in both VPNs. What should limit it to the staff VPN?
Select an answer to reveal the explanation.
Short Explanation
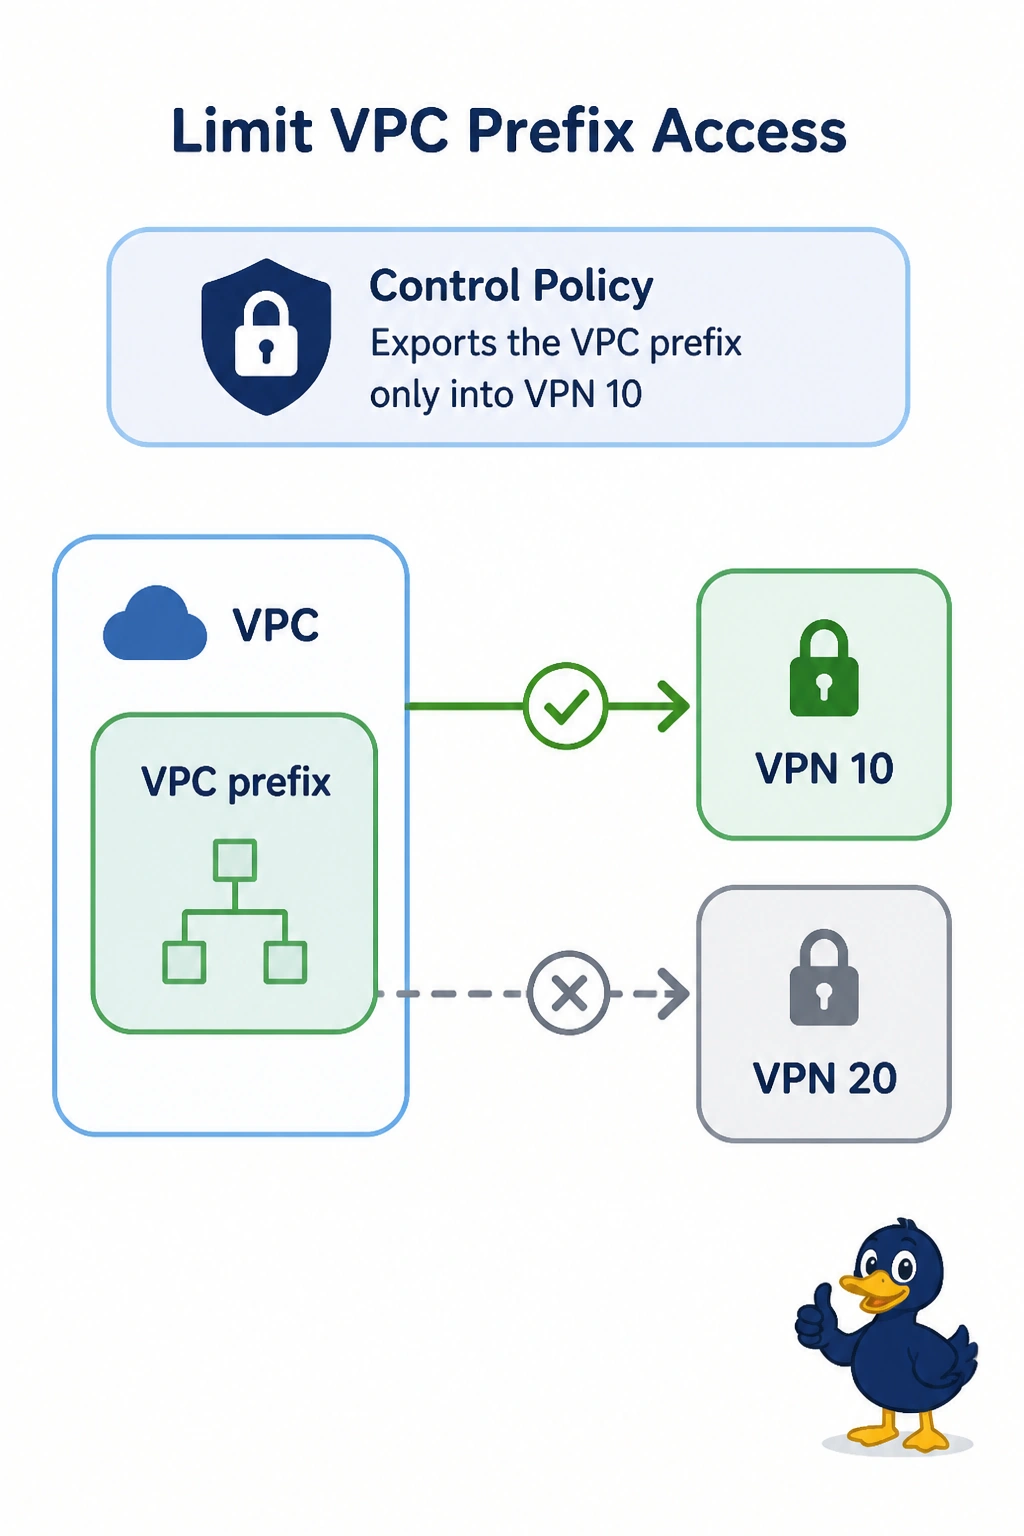
You can keep the VPC prefix for staff by using a control policy to export it only into VPN 10. A strict voice SLA does not hide an OMP route, a shorter BFD timer detects tunnel failure rather than filtering routes, and an IKE identity does not filter OMP by VPN.
Full Explanation
A control policy determines which VPNs receive a prefix through OMP. Because the VPC prefix is installed in both VPN 10 and VPN 20, guests in VPN 20 can see it; configure the policy to export that prefix only into VPN 10 so staff retain it and guests do not learn it. A strict voice SLA governs forwarding behavior for traffic matching the voice application; it does not control OMP route distribution or hide a prefix from VPN 20. A shorter BFD timer detects tunnel failure more quickly and can trigger route withdrawal when a tunnel is down, but it does not filter routes while the tunnel is up or distinguish staff from guests. An IKE identity is used in the gateway’s IKE authentication context, not to filter OMP routes by VPN, so it does not enforce this prefix’s VPN scope. Exam caveat: limiting route export to VPN 10 addresses which VPN learns the prefix; the policy must match the intended VPC prefix and VPN correctly. Practical check: inspect OMP routes on an edge in VPN 20 and confirm the VPC prefix is absent, then inspect an edge in VPN 10 and confirm the prefix remains present.