
A store's only AWS cloud gateway is a single point of failure for the VPC. Catalyst SD-WAN needs a live alternate gateway, and only one cloud gateway can be created per AWS region. What should they add?
Select an answer to reveal the explanation.
Short Explanation
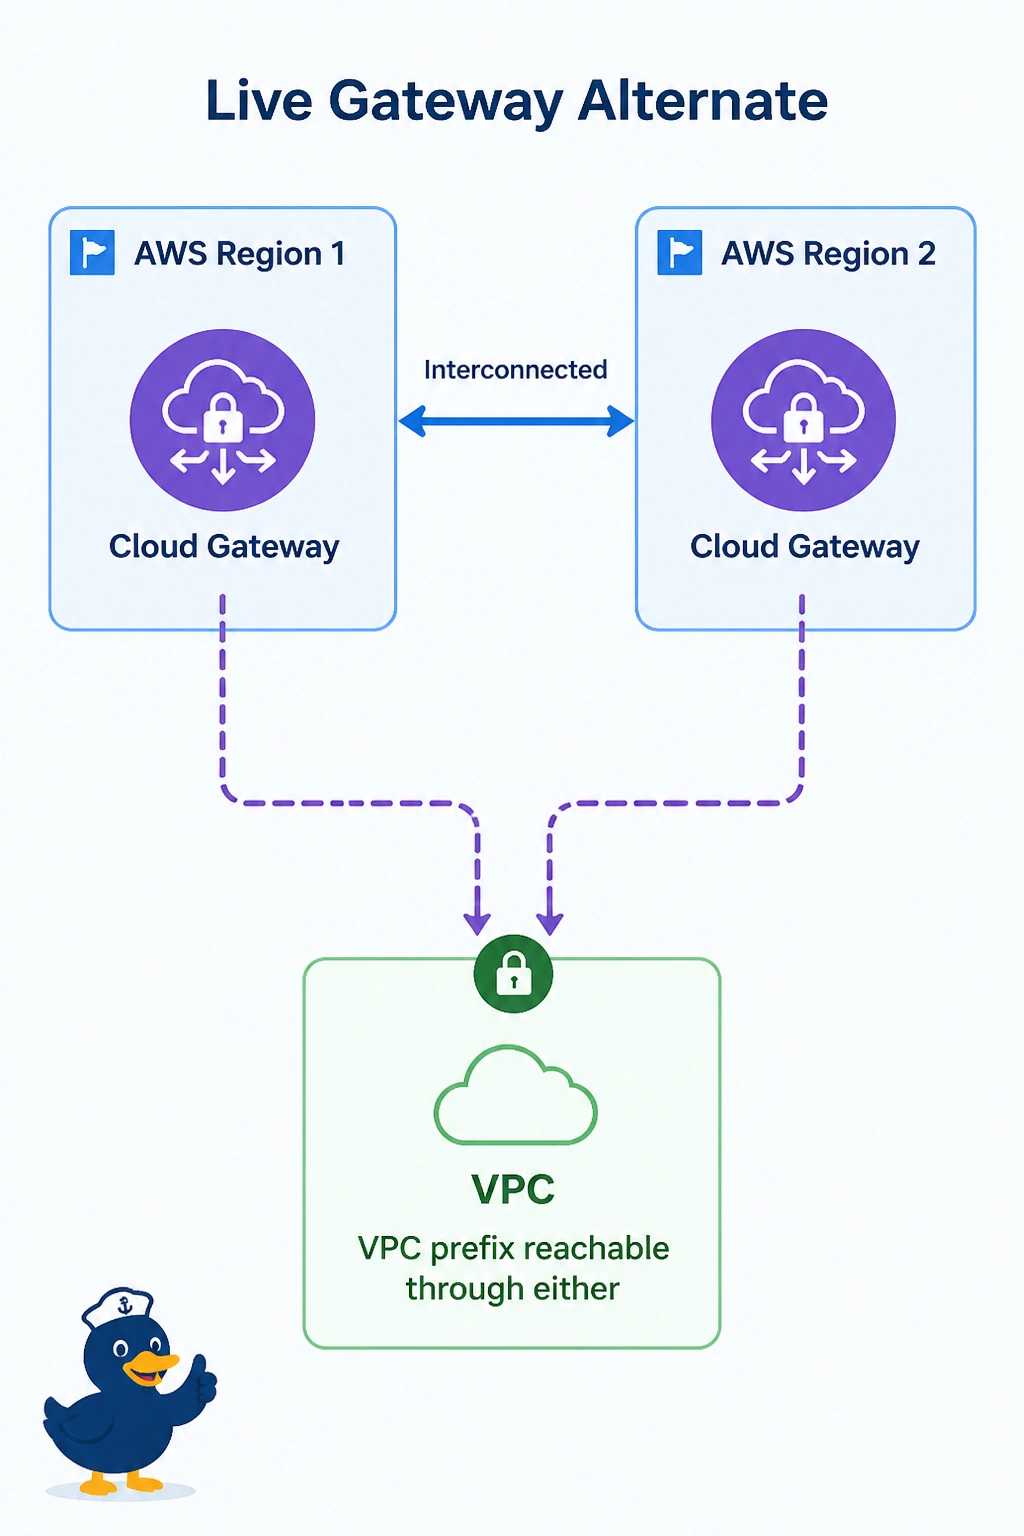
One gateway is one front door, and AWS lets you build only one cloud gateway per region. You add a cloud gateway in a second region and interconnect the two so the VPC prefix is reachable through either one. A SIG tunnel does not inherit private VPC prefixes, and shutting the internet color removes the road both gateways need.
Full Explanation
Cloud OnRamp for Multicloud supports only one cloud gateway per AWS region, so a second gateway in the same region is not an option. Each gateway already runs a pair of virtual routers for in-gateway resiliency, but a design that needs a live alternate to the whole gateway adds a cloud gateway in a second region. Cloud OnRamp interconnects the regional gateways, for example through Transit Gateway peering, so the VPC prefix is reachable through either gateway and the stores keep BFD to both. A SIG tunnel inspects internet-bound traffic. It does not advertise the private VPC or take over when an IaaS gateway fails. A tracker that shuts the internet color removes the underlay used to reach every gateway. VPN 512 is management and does not load-balance VPC traffic. Exam caveat: both gateways must be reachable from the service VPN the stores use, and the inter-region path adds latency. Operational check: shut the first gateway and confirm store BFD and the VPC prefix move to the second.