
A hotel will send guest web traffic through Cisco Umbrella using the Catalyst SD-WAN Secure Internet Gateway feature. An engineer also plans a manual crypto map, in VPN 0, to the same Umbrella headend. What should they do?
Select an answer to reveal the explanation.
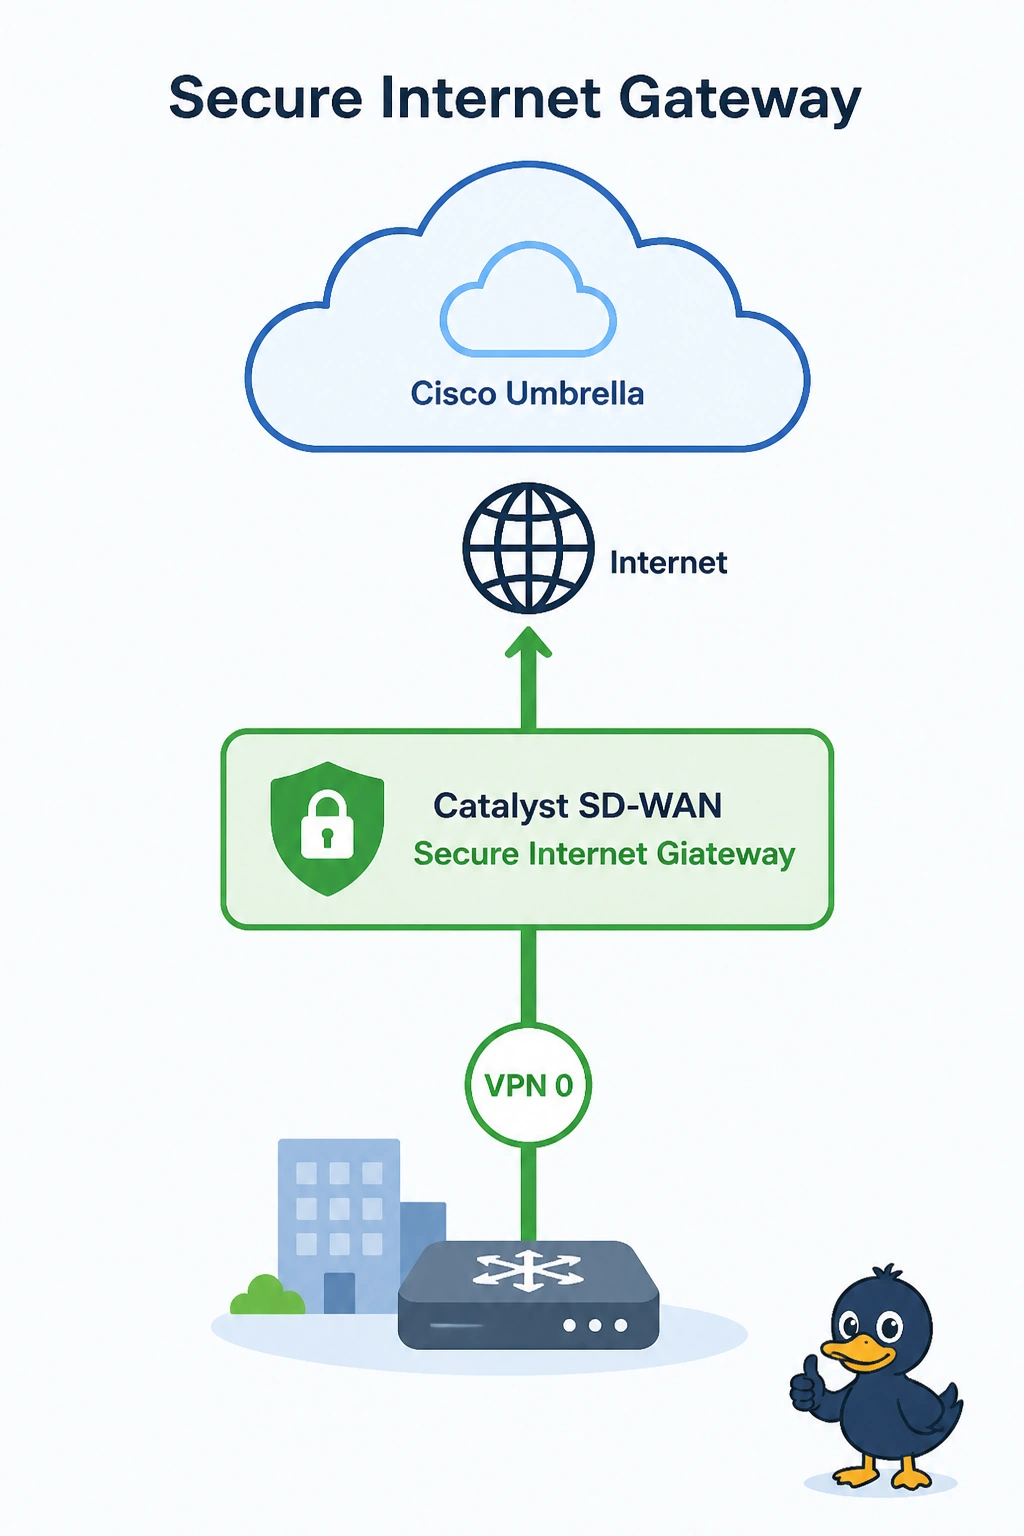
Short Explanation
Two captains steering the same ship will fight over the wheel. You let the Secure Internet Gateway feature build the Umbrella tunnels and steer guest web into them. A hand-built crypto map to the same headend competes with that feature, and VPN 512 is only management.
Full Explanation
The Catalyst SD-WAN Secure Internet Gateway feature creates the IPsec or GRE tunnels to Umbrella and expects policy to steer the chosen traffic into those tunnels. Adding a manual crypto map in VPN 0 toward the same headend creates a second, conflicting negotiation for the same job. Use the feature, not both. Disabling the SIG feature to keep the crypto map throws away the integration the hotel selected and leaves steering and health checks to a one-off map. A crypto map aimed at an AWS virtual private gateway reaches a VPC, not Umbrella, so it is not the SIG tunnel. VPN 512 is the management VPN. Guest web sessions belong in a service VPN and are steered into the SIG tunnels that live on the transport side. They are not carried as management traffic in VPN 512. Exam caveat: the feature still needs a correct SIG credential and a data policy that matches guest web. Turning the feature on without the steer builds tunnels nobody uses. Operational check: the edge should show SIG tunnels up to Umbrella, and the running configuration should not also contain a crypto map to those same Umbrella addresses.