
A hotel chain runs Catalyst SD-WAN and wants branch web traffic inspected by Cisco Umbrella before it reaches the internet. VPC connectivity is a separate project. Which feature should they configure?
Select an answer to reveal the explanation.
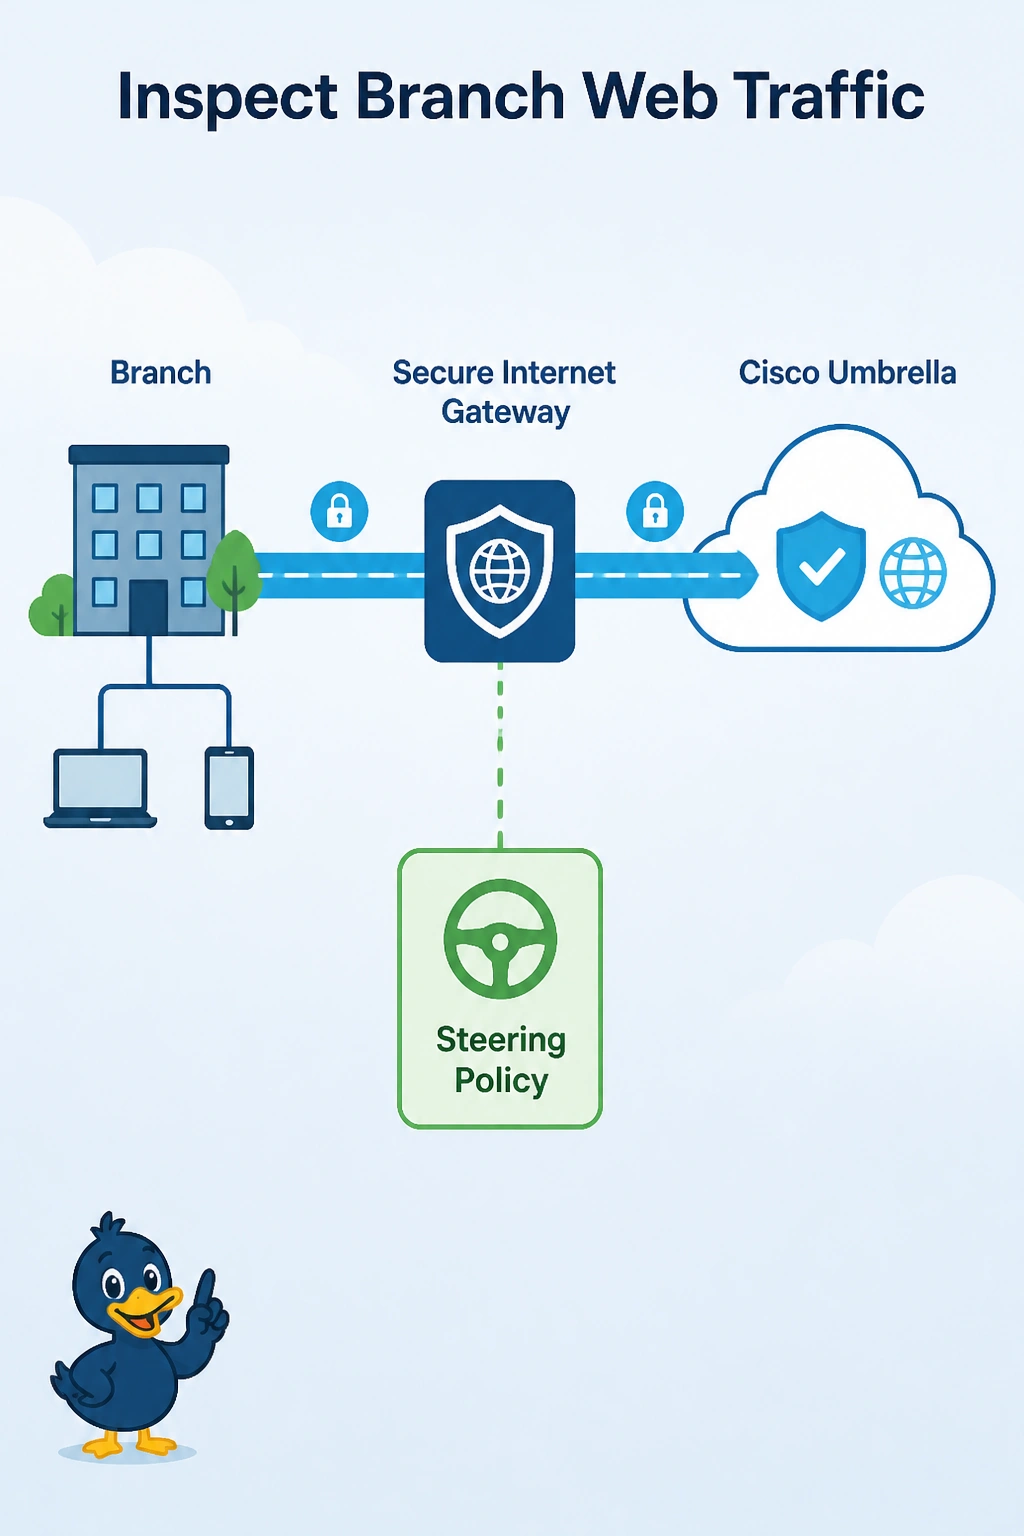
Short Explanation
You want a guarded on-ramp to the whole internet, not a private road into one VPC. The Secure Internet Gateway feature builds the tunnels to Umbrella and steers web traffic there. Multicloud OnRamp is the other project, the one they postponed.
Full Explanation
The Catalyst SD-WAN Secure Internet Gateway feature builds IPsec or GRE tunnels from the edge to a provider such as Cisco Umbrella and uses policy to steer the intended traffic into those tunnels for inspection. That matches a hotel chain that wants branch web traffic inspected before internet destinations, with VPC work still out of scope. Cloud OnRamp for Multicloud provisions a cloud gateway and attachments for IaaS. Inventing an inspection VPC is a different design and is not what the SIG feature does. Cloud OnRamp for SaaS measures and steers specific enabled SaaS applications. It does not treat every web destination as one application and it does not replace Umbrella inspection. A control policy that prefers only the data-center TLOC forces backhaul to the hotel data center. That can be a centralized internet exit, but it does not build Umbrella tunnels or apply Umbrella inspection. Exam caveat: SIG steering is selective. Voice or VPC prefixes can stay on their own paths while web traffic uses the Umbrella tunnels. Operational check: the edge should show the SIG tunnels up, and a web session from a branch host should appear in Umbrella rather than leaving by an unsteered NAT default.