
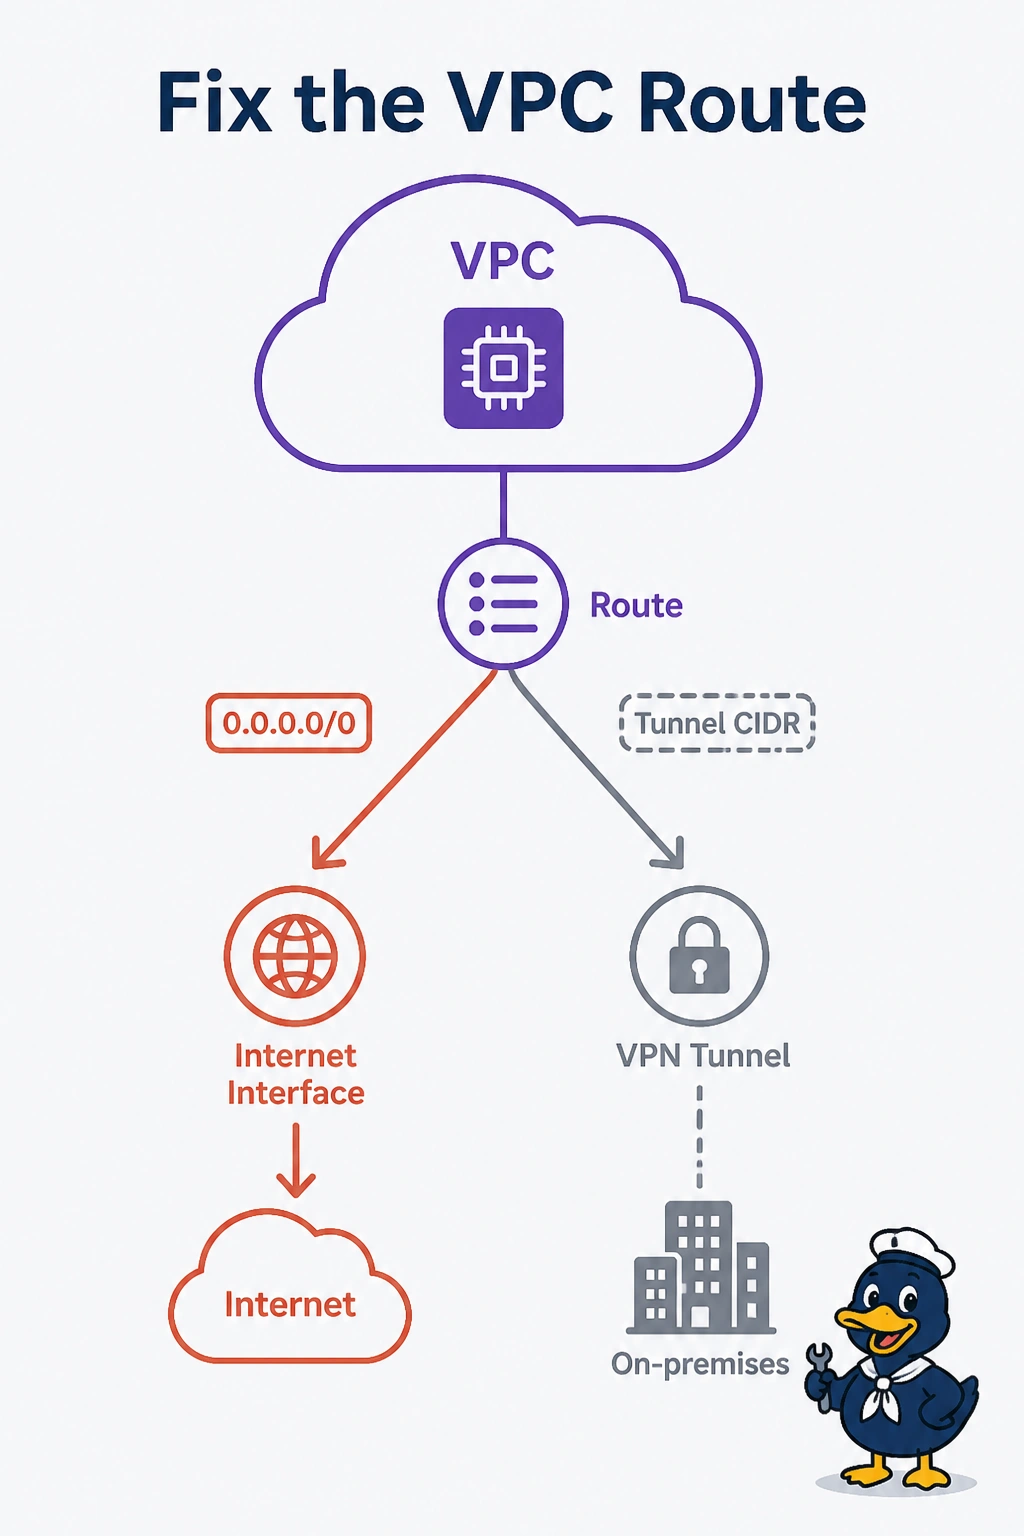
An IPsec SA to AWS is up. The encaps counter stays at zero while users fail. The campus route for the VPC points out the internet interface, not the tunnel. What is wrong?
Select an answer to reveal the explanation.
Short Explanation
The safe is locked and ready, and you are handing the package to the street. You point the VPC route at the tunnel so packets are encapsulated. A zero encaps counter with the SA up means the traffic never entered the tunnel, not that IKE failed.
Full Explanation
Encapsulation increases only when packets are routed into the protected tunnel. The SA is up and the counter stays at zero because the VPC route points out the raw internet interface, so the packets leave unprotected or die on the internet. Point that route at the tunnel interface. IKE has already succeeded. A down SA is not what a live SA with zero encaps means. Anti-replay drops packets that already entered the SA and arrived out of order. It does not keep the encaps counter at zero. The virtual private gateway does not run OSPF and does not encapsulate traffic that the campus never sends into the tunnel. Exam caveat: a more specific route can still point a single host out the internet interface after you fix the aggregate. Check the route the failing host actually uses. Operational check: show ip route for the VPC prefix should list the tunnel, and the encaps counter should rise on a new ping.